Blog

  • Top Applications of Wiki LLMs

    Top Applications of Wiki LLMs

    Discover the top 5 applications of Wiki LLMs and how they transform knowledge management. Learn from Mobeen Abdullah, AI expert.
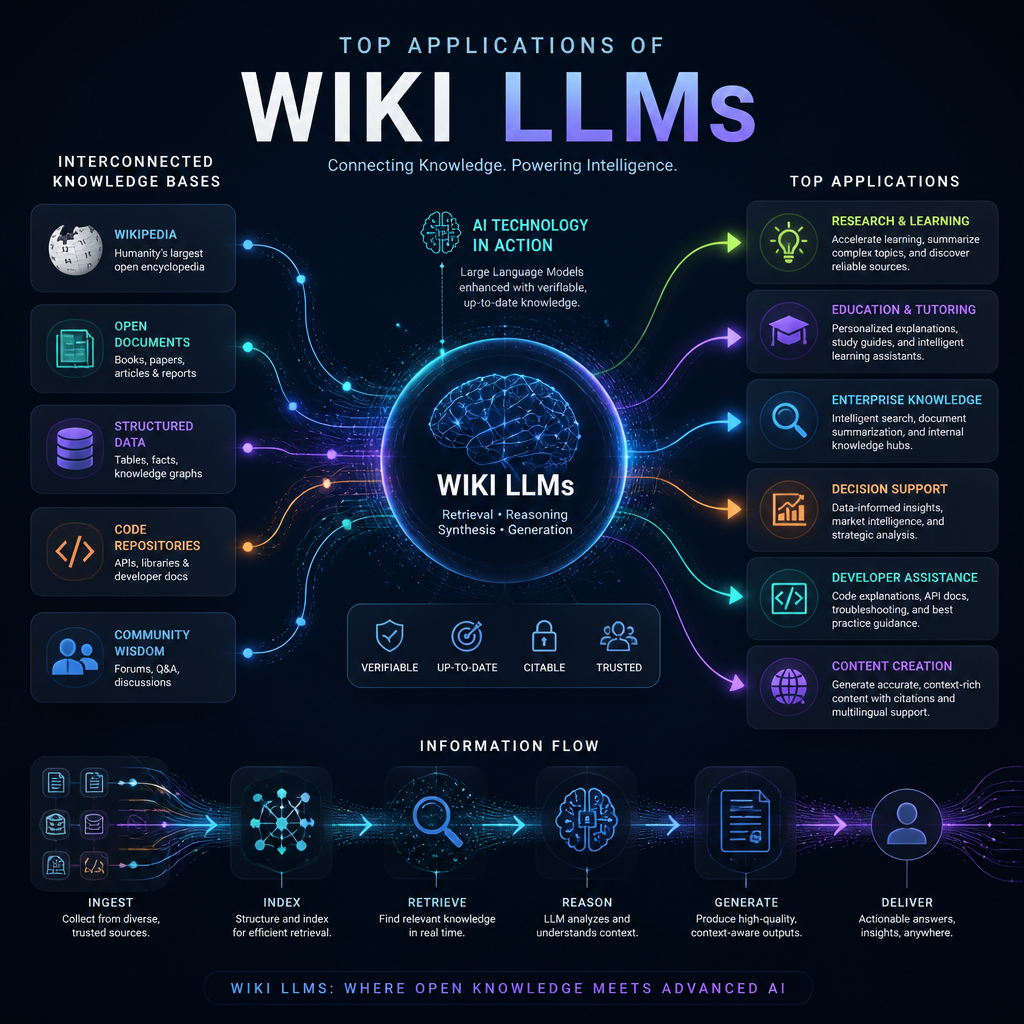
    Featured image for Top 5 Applications of Wiki LLMs You Need to Know About

    Understanding LLM Wiki and Its Applications

    An LLM Wiki (a framing that got a lot of attention via Andrej Karpathy) blends large language models with structured, editable knowledge. The point isn’t “chat over PDFs.” It’s creating a repository that improves over time — pages get refined, links between concepts get clearer, and gaps become obvious.

    A good mental model: RAG retrieves. A wiki accumulates. An LLM Wiki tries to do both, but with the wiki being the long-term memory you keep grooming.

    One practical application I’ve seen work well is taking thousands of scattered notes, docs, and research snippets and turning them into a navigable knowledge graph. The patterns in the Karpathy LLM Wiki are useful because they force you to think in “pages and connections,” not “search results.” In one real project, the first win wasn’t accuracy — it was discoverability. People stopped asking the same question in Slack because the answer lived on a stable page that kept getting better.

    If you want to get your hands dirty, the LLM Wiki GitHub repo is a solid starting point. I like it because it’s not pretending this is magic. You still need ingestion rules, review loops, and some discipline around what gets written back to the wiki.

    LLM Wiki vs RAG: Key Differences

    RAG is great when your source documents are already high quality and relatively stable. You embed text, retrieve top-k chunks, and generate an answer. That’s a clean pipeline, and it ships fast.

    But RAG can get weird as your corpus grows. Chunking breaks context, duplicates creep in, and different docs contradict each other. Then you’re stuck: do you “fix” the source docs, or just hope retrieval picks the right chunk? I’ve watched teams quietly add prompt band-aids for months because it’s cheaper than cleaning a messy knowledge base.

    LLM Wikis take the opposite stance: consolidate the knowledge into fewer, better artifacts. Instead of answering from a random pile of excerpts, you build canonical pages (“How auth works here,” “Pricing rules,” “Experiment methodology”) and keep tightening them.

    The tradeoff is obvious, though. Someone has to own those pages. In practice, I’ve had success with a lightweight workflow: the model drafts updates, a human reviewer approves them, and the wiki logs what changed. Without that loop, you’ll end up with confident-sounding nonsense that looks official.

    Educational settings are where this feels almost unfair. A student doesn’t need ten disconnected paragraphs from ten documents; they need one coherent explanation, plus links out to deeper pages. That coherence is exactly what a wiki structure enforces.

    Understanding the Meaning of LLM

    LLM stands for Large Language Model — a model trained to predict and generate text based on patterns in huge datasets. That sounds abstract, but the practical point is simple: it can summarize, rewrite, connect ideas, and answer questions in a way that feels conversational.

    Still, an LLM doesn’t “know” your organization’s truth by default. It knows language patterns. So, if you don’t anchor it to a governed knowledge base (documents, wiki pages, citations, review history), you get answers that may sound right while being subtly wrong.

    In other words: the LLM is the fluent interface. The wiki is the memory you can audit.

    As we get deeper into Wiki LLMs, that split matters. Every time I’ve seen these systems succeed, the team treated knowledge like software: versioned, reviewed, and maintained.

    Practical Applications of LLM Wikis

    1. Educational Resources: LLM Wikis let educators assemble material into a structured learning map instead of a folder dump. The nice part is the navigation: prerequisites can be explicit (“read this first”), and examples can be attached to the concept page that needs them.

    A simple scenario: a student working through linear algebra gets stuck on eigenvectors. In a normal LMS, they bounce between lecture slides, a textbook chapter, and maybe a forum post. In an LLM Wiki, the eigenvector page can include the definition, an intuition section, two worked examples, and links back to prerequisites (matrices, determinants). Because the content is centralized, you fix it once — everyone benefits.

    1. Corporate Knowledge Management: Enterprises lose time to tribal knowledge. I’m talking about onboarding docs that don’t match reality, runbooks that assume one specific environment, and “ask Jane” processes that don’t survive a vacation.

    With an LLM Wiki, you capture that institutional knowledge into canonical pages. Then you wire your support or internal assistant to answer from those pages. The big win isn’t just productivity; it’s consistency. When the answer changes (new pricing rule, new escalation path), you update one page instead of hoping every doc and slide deck gets updated too.

    1. Research Projects: Research is brutal on knowledge systems because everything changes weekly. Hypotheses evolve, definitions shift, and related work piles up fast.

    A wiki structure helps because it encourages stable “concept pages” and “paper pages.” I’ve seen teams use it to keep a living bibliography where each paper gets: a one-paragraph summary, key claims, weaknesses, and how it connects to the project. Then, when someone says “why are we not using method X?”, the answer is already linked and documented — not trapped in one person’s head.

    1. Developer Tools: For developers, LLM Wikis can become the “how we build software here” brain. Not just API docs, but the messy stuff: deployment quirks, common incident patterns, migration gotchas, and why a past decision was made.

    One mistake I’ve personally seen: a team auto-generated wiki pages from code comments and called it “documentation.” It looked impressive, yet it didn’t help anyone debug a production issue at 2 a.m. The fix was to treat the wiki like a runbook-first system: pages centered on workflows (deploy, rollback, rotate secrets), each with checks, commands, and failure modes. Then the LLM helped by proposing updates after incidents, while engineers approved the final wording.

    1. Content Generation: Writers and content teams can use an LLM Wiki as a source-of-truth for voice, product claims, and approved messaging — basically a guardrail against accidental contradictions.

    The practical flow is straightforward: keep pages for brand voice, product features, pricing, and “do not claim” rules. When you draft a new post, the model pulls from that curated wiki, not from whatever it remembers. That reduces rework. It also avoids the awkward situation where two different blog posts describe the same feature in two different ways.

    In my experience, the teams that get the most value don’t try to automate everything. They automate the boring parts (drafting, summarizing, linking) and keep humans in the loop for judgment calls.

    My Experience With This

    As the founder and CEO of Revnix, I’ve built cloud-native and AI systems where knowledge sprawl quietly becomes a tax on every team. When we introduced wiki-style LLM workflows, the early wins were surprisingly unglamorous: fewer repeated questions, faster onboarding, and less time spent hunting for “the latest doc.”

    One rollout lesson I’d emphasize: start with a narrow scope. Pick one area with frequent questions (onboarding, support troubleshooting, incident response), build 20–40 high-quality pages, and enforce ownership. After that, expand.

    If you skip ownership, the wiki becomes a graveyard. If you skip review, it becomes a rumor mill. But when you get those two right, you end up with something rare — a knowledge base that actually keeps up with the business.

    Conclusion

    Wiki LLMs aren’t a novelty. They’re a practical answer to a real problem: knowledge keeps changing, while most documentation systems assume it won’t.

    Across education, corporate knowledge management, research, developer documentation, and content workflows, the pattern is the same. Use the LLM to help you write and connect concepts, then use the wiki structure to make those concepts durable and auditable.

    If you’re considering adopting one, don’t start by asking “what model should we use?” Start by asking “who will own the pages, and how will updates get approved?” Get that right, and the tech part becomes much easier.

    Frequently Asked Questions

    1. What is a wiki LLM?
    A wiki LLM refers to a large language model that organizes and structures knowledge in a wiki format. It allows users to build, maintain, and query a dynamic knowledge base, which evolves over time.

    2. How does an LLM Wiki differ from traditional RAG systems?
    Unlike traditional Retrieval-Augmented Generation systems that pull documents for every query, an LLM Wiki creates a persistent knowledge base that can be accessed and updated incrementally, making it more efficient for users.

    3. What does LLM actually mean?
    LLM stands for Large Language Model, which refers to sophisticated AI models designed to understand and generate human-like text based on extensive linguistic data.

    4. Where can I find resources on LLM Wiki implementations?
    The LLM Wiki GitHub provides comprehensive resources and tools for developers interested in building LLM-driven wikis tailored to their needs.

    5. Can LLM Wikis be used for educational purposes?
    Absolutely! LLM Wikis can be tailored to create rich educational resources that help students access and interact with knowledge efficiently.
  • Top Free WordPress Security Plugins in 2026

    Top Free WordPress Security Plugins in 2026

    Discover the best free WordPress security plugins in 2026 that protect your site from attacks and vulnerabilities.

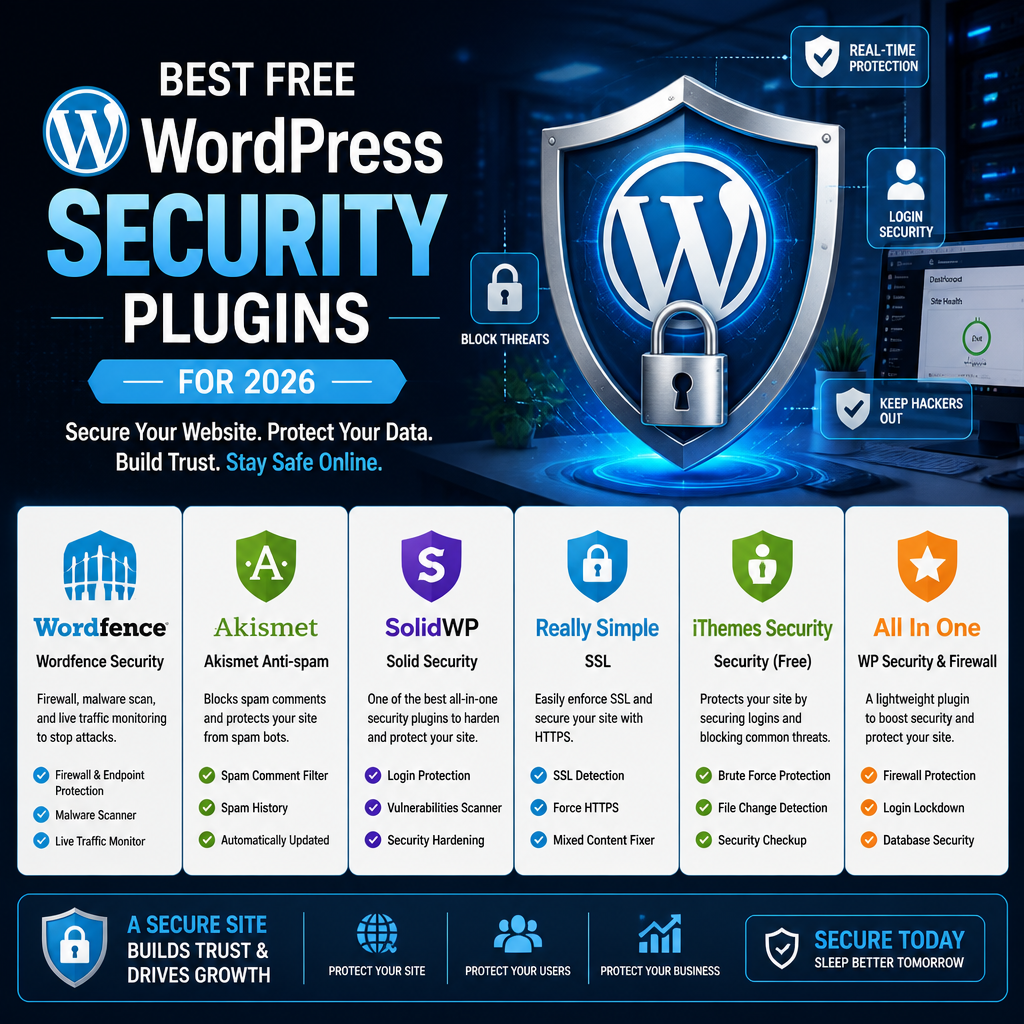
    Featured image for The Best Free WordPress Security Plugins for 2026

    The Best Free WordPress Security Plugins for 2026

    Most WordPress security problems aren’t Hollywood hacking scenes. They’re boring:

    • A plugin update gets delayed “until after the campaign.”
    • Someone reuses a password from an old breach.
    • The login page gets brute-forced all night.
    • A compromised admin account installs a sketchy plugin, and now you’re hosting a spam farm.

    A good free security plugin won’t make you invincible, but it will reduce your attack surface, catch obvious issues early, and give you a fighting chance when something goes sideways.

    Here are the free tools I actually see used in the wild, plus what I’d watch out for.

    1. Wordfence Security

    Wordfence is the “default pick” for a lot of site owners for a reason. The free version gives you a web application firewall (WAF), a malware scanner, and brute-force protection. It’s also one of the few plugins that makes you look at your traffic like an adult—you can see what’s hitting /wp-login.php, which IPs are being noisy, and what’s getting blocked.

    Where Wordfence shines (free tier):

    • WAF rules that block common exploit patterns
    • Malware scanning and file change detection
    • Login security controls (rate limiting, lockouts)
    • Visibility: live traffic, blocked requests, attack patterns

    Common mistake I keep seeing: people install Wordfence, feel safer, and then ignore the alerts. If you’re going to run it, you need to tune notifications so you don’t end up with inbox fatigue.

    How I configure it on a typical small business site:

    1. Turn on brute-force protection and set lockouts (don’t go extreme; you can lock out legit users).
    2. Disable XML-RPC if you don’t need it (a lot of sites don’t).
    3. Run an initial full scan, then schedule scans during off-hours.
    4. Check the “Live Traffic” view once a week for a month. After that, monthly is fine unless you’re under active attack.

    If you run WooCommerce or membership sites, be careful with aggressive blocking. I’ve seen stores block payment gateway callbacks and break checkouts—usually because someone flipped on strict rules without testing.

    2. Sucuri Security

    Sucuri Security is a solid “audit and integrity” tool. In practice, I like it when I want a simple security activity trail and file integrity monitoring without making the dashboard feel like a SOC.

    What it’s good at:

    • Security activity auditing (who did what, when)
    • File integrity monitoring (unexpected file changes)
    • Post-hack actions (useful if you’re recovering)

    Tradeoff: the plugin alone isn’t a magic shield. People confuse “scanner alerts” with “protection.” The alerts are still valuable because they push you to fix the root cause: outdated plugins/themes, suspicious file changes, or admin activity you don’t recognize.

    Mistake I’ve seen: site owners assume Sucuri will stop a brute-force attack by itself. You still need login protection (from Sucuri or another plugin) and decent hosting-level controls.

    3. iThemes Security

    iThemes Security packs a lot into one plugin: enforcing strong passwords, limiting login attempts, 2FA options, and general hardening.

    What it’s good for:

    • “Set it and forget it” hardening options
    • Strong password enforcement (huge, honestly)
    • Limiting login attempts and tightening admin behavior

    Where people trip: turning on every feature at once. I’ve watched teams enable aggressive file change detection + database tweaks + admin URL changes, and then forget what they changed. The next dev comes in, things don’t match documentation, and now you’ve got a mystery box.

    My approach: enable it in layers.

    • Start with password policy + login rate limiting
    • Add 2FA for admins and editors
    • Only then consider deeper hardening features

    4. All In One WP Security & Firewall

    This one is popular because it’s organized like a checklist—basic, intermediate, advanced—so non-security folks don’t feel lost.

    What it’s good at:

    • Login lockdown and brute-force protection
    • Basic firewall rules
    • IP blacklisting / whitelisting
    • A UI that encourages gradual improvement

    The tradeoff: “advanced” settings can cause real breakage if you don’t understand them. I’ve seen a site block legitimate RSS access and third-party integrations because someone toggled a rule without knowing what endpoint it affected.

    If you’re not sure, move one step at a time, test your contact forms, test checkout, test search, and check that your caching/CDN still behaves.

    5. MalCare Security

    MalCare’s big promise is simple: scan, detect, and help you clean up without burning a weekend. Even on the free side, it’s focused on malware detection and monitoring.

    Where it helps:

    • Malware scanning and alerts
    • Quick visibility into whether you have a real infection vs. “something feels off”

    Reality check: no scanner catches everything perfectly. You still need backups and an update routine. But a tool that spots infections early can be the difference between a 30-minute fix and a full “Google flagged my domain” nightmare.

    Importance of Free Security Plugins

    Free plugins aren’t “toy versions.” They usually cover the 80/20: stop the dumb automated stuff, warn you about risky changes, and give you controls that WordPress doesn’t ship with by default.

    But here’s the part people don’t like hearing: security plugins don’t replace basic hygiene.

    • Update WordPress core.
    • Update plugins/themes.
    • Remove what you don’t use.
    • Use real passwords and 2FA.
    • Keep clean backups.

    In 2026, it is reported that 13,000 WordPress sites are hacked daily due to outdated plugins and weak passwords, showcasing the critical need for proactive security measures (TechTide Solutions). If that number is even close to reality, it matches what I’ve seen firsthand: most compromises aren’t “zero-day genius.” They’re old vulnerabilities plus easy credentials.

    A practical “first hour” setup (what I’d do on a fresh install):

    1. Install one security plugin (don’t stack three WAFs).
    2. Turn on login protection (rate limiting + lockouts).
    3. Enable 2FA for admins.
    4. Run a full scan.
    5. Delete unused plugins/themes.
    6. Set a weekly update slot on your calendar.

    If you do just that, you’re already ahead of a lot of sites that get popped.

    Exploring WordPress SSO Solutions for Enhanced Security

    SSO isn’t about convenience. It’s about control.

    When you move logins to a central identity provider (Google Workspace, Microsoft Entra ID/Azure AD, Okta, etc.), you get a few things WordPress alone struggles with:

    • consistent 2FA enforcement
    • quick offboarding (disable one account, access dies everywhere)
    • fewer reused passwords floating around

    Yes, it makes login smoother. But the security win is that WordPress stops being the primary password vault for your team.

    MiniOrange SSO

    MiniOrange SSO is one of the more common WordPress SSO plugins because it supports multiple identity providers and different protocols depending on what you’re using (SAML, OAuth/OIDC).

    It can integrate with Google, Facebook, and Microsoft, which covers the reality for most small orgs: people already have those accounts.

    Benefits of SSO in WordPress Security

    1. Reduced Password Fatigue: Users are less likely to use weak or reused passwords since they only need to remember one.
    2. Streamlined Login Process: SSO allows for quicker access, improving user experience.
    3. Centralized User Management: Admins can manage user access more efficiently, monitoring who has access to what.

    I’ll add a fourth, because it’s the one that saves your skin during incidents:

    1. Faster containment: if you suspect an account is compromised, you kill the identity provider session and rotate credentials in one place.

    A real SSO scenario (where it helped)

    A team I worked with had a WordPress site with ~20 authors and editors. Turnover was normal—contractors, guest writers, marketing interns. The site didn’t get hacked through some exotic exploit. Someone left the company and their WordPress user never got removed. Months later, that same credential set worked (password reuse is undefeated), and suddenly new “admin” users appeared.

    Nothing fancy. Just neglected access.

    After switching to SSO tied to their Google Workspace:

    • offboarding became “disable Google account”
    • 2FA was enforced centrally
    • WordPress stopped storing the primary password people cared about

    That change didn’t solve every security problem, but it shut down a whole class of them.

    Step-by-step: how I roll out SSO safely

    SSO can absolutely lock you out if you rush it. Here’s the rollout order I trust:

    1. Create a break-glass admin account
    2. A separate WordPress admin with a long random password.
    3. Store it in a password manager.
    4. Do not use it day-to-day.

    5. Pick one identity provider

    6. If you’re already on Google Workspace or Microsoft, start there.
    7. Don’t add multiple IdPs “just in case” unless you have a real reason.

    8. Enable SSO for a pilot group

    9. Start with yourself and one other admin.
    10. Confirm you can log in, log out, and log back in.

    11. Map roles carefully

    12. Make sure an “employee” in the IdP doesn’t become an “administrator” in WordPress by default.
    13. Least privilege wins.

    14. Enforce 2FA at the identity provider

    15. This is the whole point. If you don’t enforce MFA/2FA, you’ve just moved passwords around.

    16. Roll out to editors/authors

    17. Communicate what’s changing.
    18. Expect questions like “why can’t I use my old login?”

    19. Disable WordPress password login (optionally)

    20. Only after you’ve proven SSO works.
    21. Keep the break-glass admin as your fallback.

    Common SSO mistakes (I’ve seen all of these)

    • No break-glass admin → one misconfig, and you’re locked out.
    • Role mapping too generous → users get admin when they shouldn’t.
    • Not enforcing 2FA in the IdP → you gain convenience, not security.
    • Ignoring service accounts → integrations still need access; plan them.

    As a CEO, I’ve dealt with countless security issues, and one of my biggest lessons learned is that managing user access is just as crucial as protecting the website itself. Implementing an SSO solution can drastically reduce potential entry points for attackers.

    Conclusion: Your Security Strategy Matters

    The uncomfortable truth: security plugins are only as good as your habits.

    If you install a plugin and never update anything again, you’ll still get hit. If you lock down logins but keep five abandoned plugins active, you’re still exposed. If your team shares one admin account, you’ve basically opted out of accountability.

    With over 11,334 new vulnerabilities disclosed in the WordPress ecosystem last year (TechTide Solutions), you don’t need to be paranoid—you need to be consistent.

    Here’s the security strategy I push because it holds up under real-world mess:

    • Pick one main security plugin (Wordfence or iThemes or All In One, etc.). Stacking overlapping tools tends to create conflicts and alert fatigue.
    • Harden logins (rate limits + 2FA for privileged roles).
    • Patch like it’s your job (weekly schedule; emergency updates when a critical bug drops).
    • Backups you’ve actually tested (a backup that can’t be restored is a feel-good file).
    • Access control that matches your org (remove users, enforce least privilege, consider SSO once your team grows).

    One more thing that doesn’t get said enough: measure the boring stuff.

    • When was the last update applied?
    • How many admin users exist right now?
    • How many plugins are inactive but installed?
    • Do you know where your backups live?

    If you can answer those without guessing, you’re in good shape.

    Next step: pick one plugin from the list, implement the “first hour” setup above, and put a recurring calendar block for updates. Security that isn’t scheduled is security that won’t happen.

    My Experience With This

    I’m Mobeen Abdullah. I run Revnix, and I’ve spent over a decade building cloud-native solutions and security strategies. I’ve also had to do the unglamorous part: cleaning up compromised sites, tracing how access was gained, and explaining to stressed-out teams why “we installed a security plugin” didn’t prevent a mess.

    One incident I still remember: a content site started throwing random redirects only on mobile. Desktop looked fine. The owner thought it was an ad network problem. It wasn’t.

    What actually happened was classic:

    • an outdated plugin provided the entry point
    • a malicious PHP file got dropped into a writable directory
    • the malware served conditional redirects (user-agent based), so the team didn’t see it during quick checks

    The fix wasn’t just “scan and delete.” We had to:

    1. Put the site in maintenance mode (stop the bleeding).
    2. Rotate passwords (WordPress admins, hosting panel, database, SFTP).
    3. Reinstall clean core files (don’t trust compromised ones).
    4. Remove the vulnerable plugin and replace it.
    5. Scan + diff key directories (wp-content/plugins, wp-content/uploads, mu-plugins).
    6. Add login controls + 2FA so the next attempt was harder.
    7. Set up a weekly update cadence—because the root cause was neglect, not lack of tools.

    That’s why I’m biased toward boring, repeatable security: fewer plugins, clear ownership, and a routine. Tools help, but habits win.

    If you want more comparisons and perspectives, here are a few decent roundups worth skimming (then make your own call):

  • Personalize Your Emails for Better Engagement in 2026

    Personalize Your Emails for Better Engagement in 2026

    Discover how to personalize your email marketing campaigns in 2026 for improved engagement and customer loyalty. Learn effective techniques and strategies.

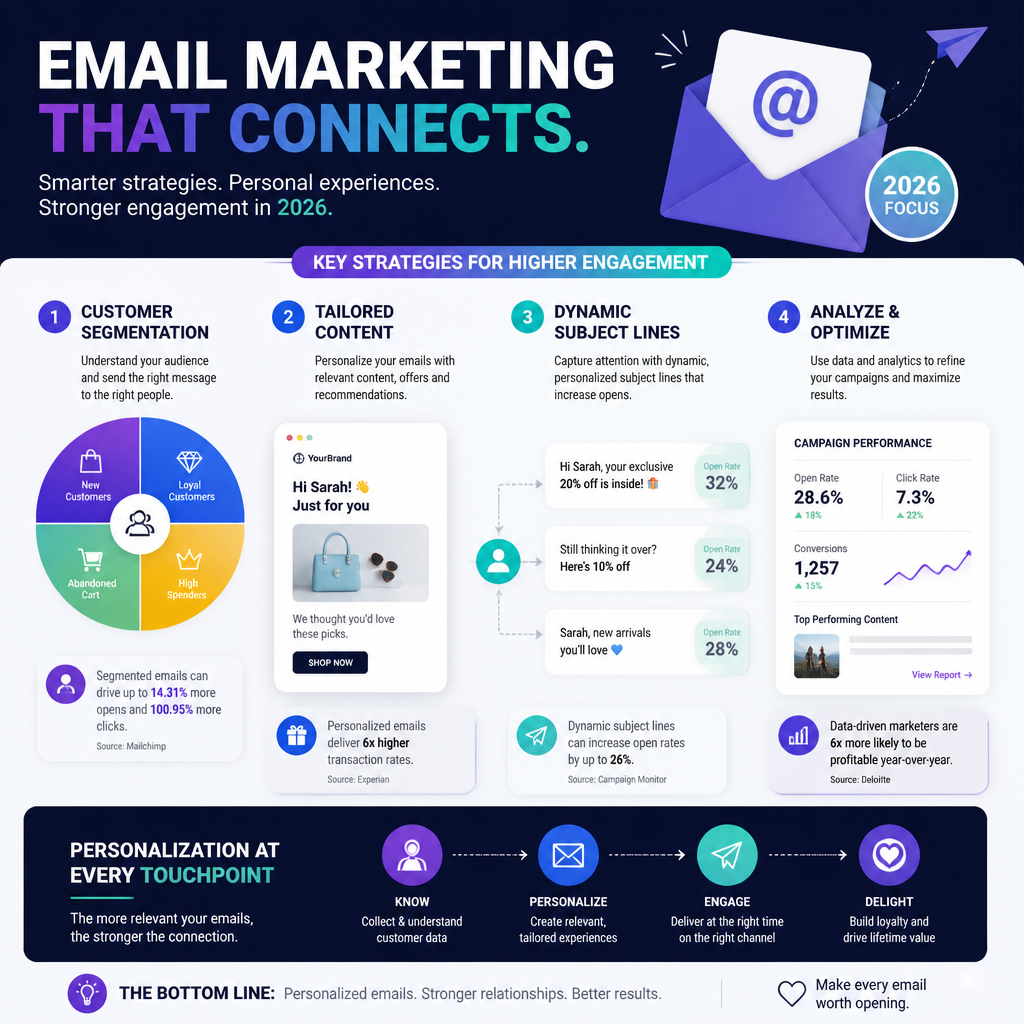
    Featured image for How to Personalize Your Emails for Better Engagement in 2026

    How to Personalize Your Emails for Better Engagement in 2026

    Email marketing is evolving rapidly, and personalization has become a cornerstone of effective campaigns. In 2026, marketers face the challenge of making their emails stand out in crowded inboxes.

    That said, “crowded inbox” isn’t an excuse to spray-and-pray. If your emails look and sound like everyone else’s, they’ll get treated like everyone else’s—skimmed, ignored, or unsubscribed.

    Personalization is key to achieving high engagement rates, and understanding how to implement it can significantly boost your email marketing effectiveness. The trick is making it feel helpful rather than creepy, and repeatable rather than fragile.

    How to personalize your emails for better engagement in 2026—segmentation and dynamic blocks example

    Why Personalization Matters

    Personalized email marketing strategies are proven to enhance engagement and drive conversions. According to a study, personalized emails have an open rate that is 26% higher than generic emails (Campaign Monitor).

    But the real reason personalization matters is simpler: it reduces “mental load.” People don’t want more content. They want the right content.

    It’s about relevance, not tricks

    If you only take one idea from this section, take this: personalization is just relevance you can scale.

    So yes, names can help. But I’ve seen the opposite too—Hey , because the first name field is blank, or Hey {FNAME} because the merge tag broke. Those are unforced errors, and they train subscribers to distrust your email.

    What actually moves the needle is matching the email to the subscriber’s intent:

    • A new lead wants clarity and proof (what is this, why should I care).
    • A first-time buyer wants guidance (how to use it, what to do next).
    • A repeat buyer wants speed (reorder, refills, upgrades).
    • A lapsed customer wants a reason to come back (newness, incentives, timing).

    Because those intents are different, the “same” newsletter sent to all four groups usually underperforms.

    A quick example I’ve watched play out

    A couple years back, I worked with a small eCommerce brand that sold two very different product categories: everyday essentials and giftable premium items. Their weekly email blasted the full catalog to everyone.

    We didn’t redesign anything at first. Instead, we split the list into three segments:

    1. Essentials-first buyers (80%+ of purchases in essentials)
    2. Gifts-first buyers
    3. Browsers (high clicks, low purchases)

    Then we changed only two things: the hero product and the opening paragraph. Essentials got “restock” language and practical bundles. Gifts got “occasion” framing and tighter curation. Browsers got bestsellers plus a simple quiz-style CTA.

    Even with the same sending schedule, engagement lifted fast because the content finally matched why people were there.

    Common mistakes that kill trust

    Personalization backfires when it’s sloppy or overly invasive.

    • Using sensitive data for “wow”: referencing exact browsing behavior in the subject line can feel gross, even if it’s technically accurate.
    • Over-segmenting too early: 18 micro-segments sounds smart until each one has 47 people and you can’t learn anything.
    • Personalizing the wrong layer: swapping product blocks while keeping generic copy often reads like a thin veneer.

    If you’re unsure, start “boring”: segment by lifecycle stage and purchase category. Those two alone can carry a lot of weight.

    How to Personalize Your Emails for Better Engagement

    This is the part where most teams jump straight to automation. I’d rather you earn it.

    Start with segmentation and messaging, then add dynamic content, then add triggers. Each layer should make the previous one easier—not more chaotic.

    Segment Your Audience Effectively

    Segmentation is about dividing your email list into smaller, more targeted groups. You can segment based on various factors such as demographics, purchase history, and engagement level.

    For instance, sending different messages to new subscribers compared to loyal customers can dramatically improve engagement rates.

    A real-world example comes from iContact, where small businesses outsmarted corporate giants by employing targeted email segments that addressed specific customer needs (iContact). They tailored their messaging, resulting in higher open rates and conversions.

    The segmentation ladder I actually use

    If you’re stuck, run this ladder from top to bottom. Stop when you’re getting clearer results.

    1. Lifecycle: subscriber → lead → first-time customer → repeat → VIP → lapsed
    2. Engagement: active (clicked recently) vs. inactive (no opens/clicks in X days)
    3. Category affinity: what they browse/buy most
    4. Price sensitivity: full-price buyers vs. discount-driven
    5. Channel source: paid social vs. organic vs. referral (messaging differs)

    Lifecycle segmentation is the cheapest win because your data is usually reliable (signup date, purchase count). Meanwhile, “interests” can be messier unless you track it well.

    Common segmentation mistakes

    • No backstop for tiny segments: always have a fallback group (e.g., “General: Active”) so you don’t strand people.
    • Ignoring deliverability: if you keep mailing inactive subscribers forever, inbox placement can slide. Segmenting engagement helps you throttle.
    • Not documenting rules: if the team can’t explain who’s in a segment, you’ll break it later.

    Use Dynamic Content

    Dynamic content enables you to customize the content of your emails based on the recipient’s data. This can include product recommendations, tailored offers, or relevant blog posts that match their interests.

    For example, if a customer frequently buys poetry books, you can highlight new arrivals in that genre in your emails. Implementing dynamic content can lead to significant increases in engagement as it makes the email feel personally crafted for the recipient.

    A practical dynamic content setup

    When I implement dynamic blocks, I keep it tight:

    • One “smart” block per email at first (hero OR product grid OR CTA)
    • Two variants max to start (Variant A / Variant B)
    • A default version that’s safe for everyone

    Why? Because dynamic content can quietly break. If you launch five conditional blocks at once, you won’t know which one caused the weird dip in clicks.

    Also, preview it like you mean it. I’ll usually create 6–10 test contacts that represent real states (VIP, lapsed, no-first-name, no-purchase) and run inbox previews before I trust the send.

    Tailor Subject Lines and Preheaders

    The subject line is the first thing your subscribers see, and a personalized subject line can significantly improve your open rates. Using data such as previous interactions or preferences can help you craft these.

    For instance, instead of a generic subject like “New Arrivals,” you could say, “[Name], Your Favorite Authors Have New Books Out!” This kind of attention can drastically change how your emails perform.

    My subject line rules (learned the hard way)

    • Personalize with context, not flattery: “Back in stock: the size you wanted” beats “Hey Sarah!” most days.
    • Write the preheader as sentence #2: don’t waste it on “View in browser.”
    • Avoid brittle merge tags unless you’ve validated the data (and you have a default).

    A small trick that helps: write 10 subject lines, then delete the five that sound like marketing. What’s left is usually closer to human.

    Optimize Send Frequency

    Finding the right time and frequency to send your emails is critical. Over-saturating your audience with emails can lead to unsubscribes, while too few can make your audience forget you.

    Use analytics to find the sweet spot. You might discover that your audience responds better to weekend emails rather than weekdays or that certain times yield higher open rates.

    Frequency isn’t one-size-fits-all

    Here’s what I do instead of guessing:

    1. Pick a baseline (say, 1–2 sends/week).
    2. Split by engagement: active subscribers can handle more; inactive should get less.
    3. Watch complaints and unsubscribes alongside opens/clicks.
    4. Throttle promotions: if you run heavy discounts, build “quiet weeks” on purpose.

    One thing people miss: frequency problems often come from content sameness, not volume. If every email is “20% off,” even one per week can feel like spam.

    Implement Behavioral Triggered Emails

    Behavioral triggers allow you to send emails based on specific actions a user takes, such as abandoning a cart or signing up for a newsletter.

    For example, if a customer adds items to their cart but doesn’t complete the purchase, sending a reminder email can prompt them back to your site. This technique can boost email ROI and is particularly effective for eCommerce businesses.

    A step-by-step trigger plan you can ship this month

    If you’re starting from scratch, ship these in this order:

    1. Welcome series (2–4 emails)
    2. Email 1: set expectations + best content/product
    3. Email 2: social proof + FAQs
    4. Email 3: personalization ask (preferences) or starter guide
    5. Browse abandon (1–2 emails)
    6. “Still looking?” with category-based recommendations
    7. Cart abandon (2–3 emails)
    8. Reminder → objections (shipping/returns) → urgency (light)
    9. Post-purchase (2–5 emails)
    10. How to use → care tips → cross-sell that makes sense
    11. Winback (2–3 emails)
    12. New arrivals → incentive (optional) → last call

    Keep the copy specific. “Complete your purchase” is generic; “Your cart’s ready—shipping is free over $50” is useful.

    Mistakes I see constantly in triggers

    • Sending a cart email to someone who already bought (bad event timing, slow sync)
    • Discounting too fast so people learn to abandon carts on purpose
    • Stacking triggers so a subscriber gets welcome + browse + promo on the same day

    If your tool allows it, add a simple rule: “max 1 automated email per 24 hours” unless it’s transactional.

    Analyze and Improve

    The beauty of email marketing lies in the metrics. Make it a habit to analyze your email performance regularly.

    Track metrics such as open rates, click-through rates, and conversions to understand what’s working and what’s not. Utilize this data to refine your strategies continually.

    For instance, if you notice a drop in engagement after a specific change, be prepared to adjust your tactics accordingly.

    What I measure (and what I ignore)

    I care about:

    • Clicks per delivered (not just CTR on opens)
    • Revenue per recipient for promos
    • Conversion rate from click (landing pages matter)
    • Unsubscribes + spam complaints by segment

    I’m careful with:

    • Open rate as a “win” metric. It’s still directional, but it’s not the whole story.

    And I always annotate the timeline. When results change, you want to know whether it was a subject line test, a list growth spike, a deliverability issue, or a new offer.

    Starting with Email Marketing

    For those new to email marketing, starting with a solid foundation is critical. Consider enrolling in an email marketing course that covers the basics of email marketing, including list building, content creation, and analytics.

    But before you buy anything, build one working loop: collect emails → send something valuable → learn from the data → repeat. Tools and templates don’t rescue a shaky loop.

    Your first 30 days (a real starter plan)

    If I were mentoring a beginner, here’s the month plan I’d hand them:

    Week 1: Get the boring stuff right
    – Set up a sending domain (or at least authenticate properly in your platform).
    – Create one clean list and one suppression list.
    – Write down your “from name” and stick with it.

    Week 2: Build your core emails
    – One newsletter template (simple, scannable).
    – A 2-email welcome series.
    – One promo email layout you can reuse.

    Week 3: Add one personalization lever
    – Collect a preference (category, use case, or role).
    – Segment based on that single preference.

    Week 4: Run one test
    – A/B test a subject line OR CTA.
    – Pick a winner, then document it.

    That’s enough to start compounding.

    Utilizing Email Marketing Tools

    With so many tools available, selecting the right one can enhance your email marketing efforts significantly.

    If you’re shopping around, I’d start by scanning the best email marketing tools of 2026 and then narrowing based on what you actually need: segmentation depth, automation builder, reporting, and how painful (or painless) integrations are.

    What I look for in a tool (so I don’t regret it later)

    • Event tracking that’s trustworthy (purchase, browse, cart, form submit)
    • Automation with guardrails (frequency caps, exclusions)
    • Decent QA (previews by segment/state)
    • Migration support if you’re moving from another platform

    Common mistake: teams buy the tool with the fanciest automation builder, then never fix the data feeding it. Personalization doesn’t work if “product viewed” fires randomly.

    Emphasizing Compliance and Best Practices

    As you delve into email marketing, maintaining compliance with regulations like GDPR and CAN-SPAM is crucial.

    Ensure that you’re obtaining consent from users before sending them emails and that you provide them with a clear option to unsubscribe.

    Respecting your subscribers’ choices fosters trust and long-term relationships.

    A practical compliance habit

    I’m not a lawyer, so I won’t pretend to give legal advice. Still, operationally, here’s what keeps you out of trouble most of the time:

    • Use double opt-in when list quality matters more than raw growth.
    • Store signup source + timestamp.
    • Keep your unsubscribe link visible, and process it fast.

    If you ever get hit with a deliverability problem, having clean consent records makes the support conversation a lot less painful.

    Career Insights in Email Marketing

    With the rise of personalized marketing strategies, email marketing jobs are becoming increasingly relevant.

    The demand is real, but the bar has changed. Companies don’t just want “someone who can send newsletters.” They want someone who can run lifecycle programs, debug tracking, and explain performance without hand-waving.

    Email Marketing Salary Trends

    Salaries in the email marketing field vary based on experience and location but are generally competitive. According to recent data, the average email marketing manager earns between $60,000 to $85,000 annually, with experienced professionals commanding higher rates.

    For those considering a career in this field, developing skills in analytics, automation, and personalization can set you apart.

    What tends to push you toward the top of that range

    In my experience hiring and working alongside email folks, the people who get paid more usually do at least two of these well:

    • Own revenue numbers (not just “engagement”)
    • Build automations that don’t spam customers
    • Work with data (events, UTM discipline, basic SQL or at least strong reporting)
    • Understand deliverability enough to prevent fires

    If you can walk into an interview and calmly explain why clicks fell—“we changed segmentation, deliverability dipped in Gmail, and the landing page slowed down”—you’re already ahead.

    Preparing for Email Marketing Jobs

    If you’re aiming for a role in email marketing, consider undertaking specific training or certifications.

    There are numerous online courses available that focus on the nuances of email marketing, providing valuable insights that potential employers look for.

    Additionally, hands-on experience through internships or freelance projects can enhance your employability.

    A portfolio project that actually impresses

    If you don’t have professional experience yet, build a small “fake brand” lifecycle program and document it:

    1. Define two customer personas.
    2. Write a 3-email welcome series for each.
    3. Mock up segmentation rules.
    4. Create one triggered flow (cart abandon or winback).
    5. Add a measurement plan (what you’d track and why).

    Don’t just show pretty designs. Show decisions.

    A quick anecdote (the kind that happens on real teams)

    I once watched a junior marketer lose confidence because a manager kept saying, “Just personalize more.” No specifics.

    We sat down, pulled up the account, and realized the “personalization” problem was basic: half the list had no purchase data because the checkout integration was failing. The fix wasn’t copywriting—it was debugging.

    That’s the job now. You’ll write emails, sure, but you’ll also spend time making sure the inputs are real.

    Conclusion

    Personalization in email marketing is no longer optional; it’s a necessity.

    But you don’t need to boil the ocean. If you only improve three things this quarter—segmentation by lifecycle, one dynamic block, and one trigger flow—you’ll usually feel it in engagement and revenue.

    A simple next-step checklist

    If you want a clean plan for the next 2–3 weeks, do this:

    1. Audit your data fields (first name, last purchase date, category, engagement).
    2. Create 3 core segments: new subscribers, active customers, lapsed.
    3. Write one email for each that answers a different “job to be done.”
    4. Add one automation (welcome series is the safest start).
    5. Measure clicks per delivered and unsubscribes by segment.

    Then iterate. Don’t keep changing everything at once, because you won’t learn what caused what.

    Common mistakes to avoid in 2026

    • Chasing personalization gimmicks while ignoring list hygiene
    • Letting promos dominate until every email feels transactional
    • Forgetting the landing page (personalized email + generic landing page is a leaky bucket)
    • Buying a new platform before you’ve fixed your strategy

    If you’re evaluating tooling, check out Email Marketing Platforms Comparison 2026 and cross-reference it with what you actually plan to build.

    Also, if you just want a shortlist to start from, browse Top Email Marketing Platforms 2026 and Top Email Marketing Platforms for 2026—then pick the one you’ll realistically use every week.

    Personalization pays off when it’s consistent. Ship something small, make it work, and keep tightening the loop.

  • Headless CMS and Next.js: Your 2026 Guide

    Headless CMS and Next.js: Your 2026 Guide

    Discover how to effectively integrate Headless CMS with Next.js in 2026, enhancing your web development projects.

    Featured image for Getting Started with Headless CMS and Next.js in 2026

    Getting Started with Headless CMS for Next.js

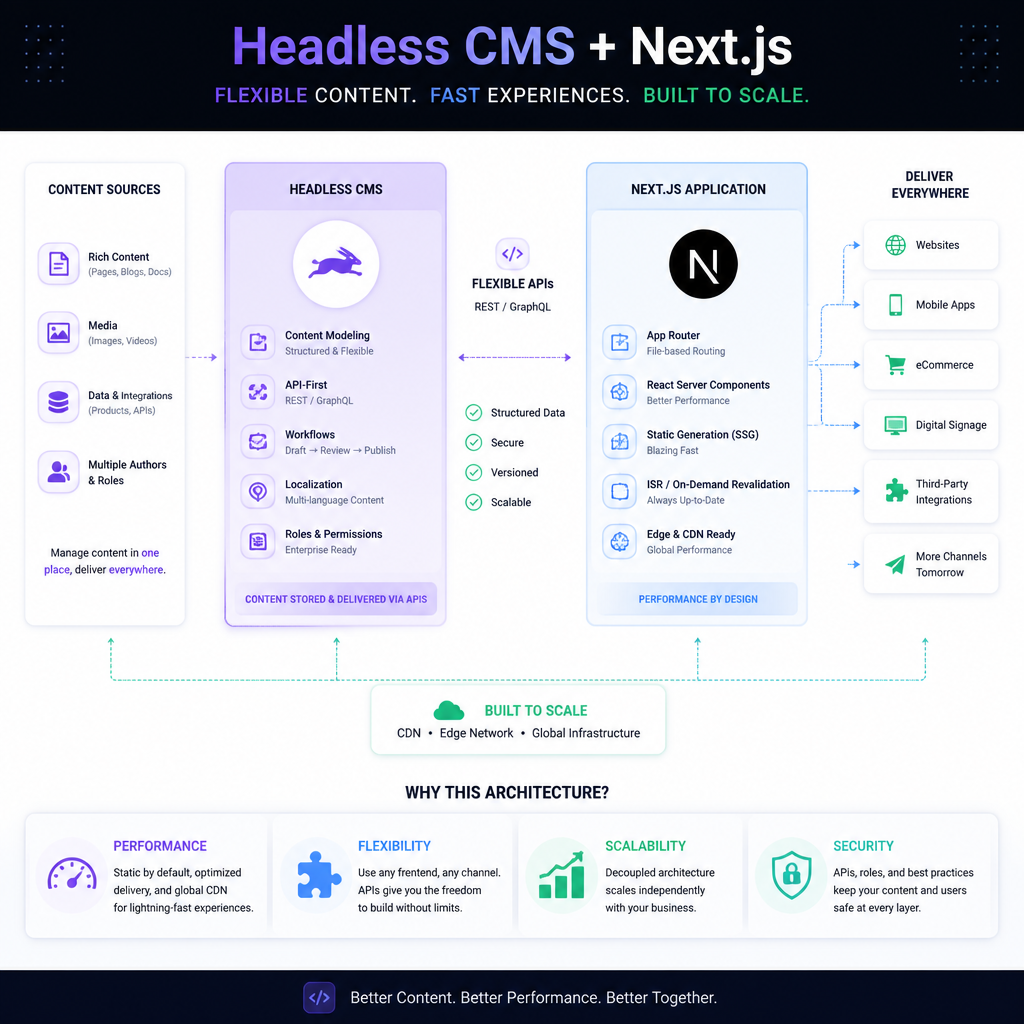
    A Headless CMS gives you an admin UI for editors and an API for developers—without forcing you into a specific front end. Next.js is a great match because it can render content a bunch of different ways depending on the page and traffic.

    Understanding Headless CMS

    A Headless CMS stores content and exposes it over an API (REST and/or GraphQL), while your Next.js app handles routing, layouts, and rendering.

    Here’s what actually matters in the 2026 day-to-day:

    • Flexibility: you can redesign the front end without rewriting content models. That’s not theoretical; it’s the difference between a 2-week refresh and a 2-month “replatform.”
    • Omnichannel delivery: the same “Article” can power the website, an in-app help center, and even an internal dashboard. You’re not duplicating copy across systems.
    • Separation of concerns: editors work in the CMS, devs work in Next.js. That separation reduces merge conflicts, but it also forces you to define content types clearly (which is a good pain).

    One important nuance: “headless” doesn’t automatically mean “faster.” You still have to choose SSR vs SSG vs ISR wisely, and you still need caching. Otherwise you just moved the bottleneck.

    Benefits of Using Headless CMS with Next.js

    1. Enhanced Performance: Next.js gives you SSR and SSG, so you can ship fast pages and keep SEO-friendly HTML. But you only win if you avoid doing live CMS fetches on every request for pages that don’t change hourly.
    2. Developer Experience: file-based routing, server components (where it fits), and a big ecosystem make integration pretty straightforward. That said, a sloppy content model will still make your front end miserable.
    3. Scalability: scaling in a headless world usually means (a) scaling API reads, (b) controlling cache invalidation, and (c) keeping editorial workflows sane. Next.js helps, but it won’t magically fix content chaos.

    Tradeoff I’ll call out: headless setups can become “distributed systems” surprisingly fast—CMS, web app, image CDN, search, preview environment, webhook handlers. You get power, but you also get more moving parts to monitor.

    Popular Headless CMS Options for Next.js

    Several CMS options are compatible with Next.js. These three come up constantly for good reasons:

    • Payload: open-source, TypeScript-native, and developer-first. It’s a strong choice when you want to own your data model and keep types tight.
    • Sanity: great real-time editing and collaboration, plus a flexible schema. Teams with lots of editorial iteration tend to like it.
    • Strapi: open-source with a plugin ecosystem and lots of community knowledge. It’s often the “default” pick for teams that want something familiar.

    My opinionated filter when choosing:

    • If your team cares about TypeScript end-to-end and you want to keep CMS logic close to your app, Payload is hard to beat.
    • If editors need live collaboration and structured content will evolve weekly, Sanity shines.
    • If you need something straightforward and you’re okay spending time on config and plugins, Strapi can work.

    Resources for Next.js Headless CMS Templates

    Templates can save you time, but they can also bake in odd decisions (auth assumptions, caching patterns, folder structure). So I treat them like scaffolding, not architecture.

    When you evaluate a template, look for:

    • Customization: can you change the content model without fighting the starter? If every field is hardcoded into a UI component, that starter will age badly.
    • Community and Support: active issues, recent commits, and real examples. A dead starter is technical debt with a README.
    • Documentation: not just “run npm install,” but details on preview, webhooks, and deployment.

    Recommended Templates:
    – Starter templates for Payload CMS can often be found on their official GitHub repository.
    – Next.js templates on platforms like Vercel or Template resources to quickly deploy your applications.

    One more practical tip: before you commit, run a “content change drill.” Add a field to the content type and see how many places in the front end you have to touch. If it’s more than you expected, your model or rendering strategy needs work.

    Using Payload CMS with Next.js

    Payload CMS is a solid choice with Next.js in 2026 because it doesn’t fight the way modern Next apps are built. If you like TypeScript, predictable local dev, and owning your schema, it’s a comfortable setup.

    Why Choose Payload?

    Payload is designed to integrate cleanly with Next.js, and a few details make it genuinely pleasant:

    • Comprehensive API: you can query content without inventing a custom backend layer. That’s fewer servers and fewer “why is this endpoint different?” conversations.
    • Typescript Support: typed collections reduce dumb mistakes—like shipping a component that assumes author.name exists when your model uses displayName.
    • Document-based Structure: it maps nicely to things like pages, posts, case studies, docs, and products.

    Where Payload can bite you: permissions and drafts. It’s powerful, but it means you have to be explicit about read access, preview behavior, and what “published” really means.

    Here’s the real-world pattern I’ve seen work: treat the CMS like a product. Version your schema changes, review access rules like you review code, and don’t let “just add a field” happen directly in production.

    Setting Up Payload CMS

    I’ll lay this out as a practical build checklist—the order matters because it prevents you from painting yourself into a corner.

    1. Install Payload:
      Run the command to set up a new Payload project directly in your Next.js app:
      bash
      npx create-payload-app

    2. Configuration:
      Configure your Payload CMS settings in the payload.config.ts file. This includes defining your collections, fields, and permissions.

    Start small. One collection. A couple fields. Get the full loop working (create → preview → publish → render) before you model your entire company.

    A sane first collection:
    – pages: title (text), slug (text), layout (blocks), publishedAt (date), status (draft/published)

    Then lock down access rules:
    – Public users: can read only published pages
    – Editors: can read/write drafts
    – Admins: can manage users and globals

    1. Fetch Data:
      Use Payload’s API to fetch content. For instance:
      javascript
      import { usePayload } from 'payload-hooks';
      const { docs } = usePayload('my-collection');

    Practical note: be careful with where you fetch.

    • For mostly-static marketing pages, prefer build-time/ISR fetches and cache aggressively.
    • For authenticated dashboards or frequently changing data, SSR (or server actions) can make sense.

    Don’t default to “fetch on every request” because it’s easy. Your CMS will become your bottleneck the first time a campaign spikes traffic.

    1. Deploy:
      Finally, deploy your application to a platform like Vercel, which provides an ideal environment for Next.js applications.

    Before you hit deploy, wire up:
    – environment variables for database + secrets
    – a preview environment (or branch deployments)
    – a webhook strategy for revalidation (so content updates actually show up)

    This is the part people skip, and then they wonder why editors are doing hard refreshes and Slack’ing screenshots.

    Payload CMS in Action

    I’ll give you two examples: one from the wild (linked), and one I’ve personally seen play out on teams.

    First, there’s a public case study: Michigan Business adopted Payload CMS for their content needs. The thing to notice in setups like that isn’t “they used Payload,” it’s why: faster iteration, clearer separation between content updates and code deploys, and less friction for the people who actually maintain the site day to day.

    For more in-depth information, refer to the source of the payload integration’s success story in Michigan here.

    Now the gritty example I see a lot: a team starts with a simple marketing site, then adds a resources hub, then adds gated PDFs, then adds a partner directory. At first, they hardcode a bunch of stuff because “it’s just a few pages.” Six months later, every change requires a developer, and the CMS is basically a blog no one trusts.

    Here’s how I’d run that migration to Payload + Next.js without breaking everything:

    1. Inventory content: list every page type (landing page, case study, blog post, docs page). Count them. Identify what actually changes weekly.
    2. Define a minimal content model: don’t model the universe. Model what you ship. If you need flexible layouts, use blocks—but keep the block set small.
    3. Build one vertical slice: create one page type end-to-end: CMS entry → API fetch → Next.js route → SEO tags → preview.
    4. Add preview early: if editors can’t preview drafts, they’ll either publish risky changes or stop using the CMS.
    5. Set up revalidation: publish should trigger an update. If you rely on “wait for the cache,” people will lose confidence.
    6. Backfill content: migrate content in batches, not a giant weekend cutover. You’ll catch model gaps faster.

    Common mistakes (I’ve made a couple of these myself):

    • Overusing “blocks”: blocks are great, but unlimited freedom turns into inconsistent pages and a messy front end. I cap block types and I document when to use each.
    • Forgetting access rules: someone will accidentally expose drafts if you don’t explicitly protect them.
    • Not planning images: if your media pipeline is an afterthought, you’ll end up serving huge images and tanking performance.
    • No rollback plan: content changes can break layout. Keep a way to revert quickly—versioning, backups, or at least a “duplicate page” workflow.

    If you want more reading around architecture decisions, I’ve seen good overviews like Why Payload CMS is the Best CMS for NextJS and broader comparisons such as Next.js CMS: Best Headless CMS Choices for 2026. I don’t treat any single post as gospel, but they’re useful for framing tradeoffs.

    Headless CMS with Next.js content flow diagram

    Conclusion

    Headless CMS + Next.js isn’t a trend in 2026—it’s the default shape for teams that want speed without handing the keys to a fragile theme layer.

    But here’s the honest part: you only get the payoff if you run it like a system, not a pile of tools. Your content model needs boundaries, your rendering strategy needs intent, and your editor workflow needs to match how your team actually works.

    A quick persona story I’ve watched play out: a product marketer wants to launch 12 new pages for a campaign next Tuesday. The dev team is already booked. In a coupled CMS, that request turns into “pick a template and pray.” In a good headless setup, the marketer duplicates a page, swaps blocks, updates copy, previews it, and hits publish—while the dev team stays focused on the product.

    That’s the win. Not “API-first,” not buzzwords. Just fewer bottlenecks.

    If you’re about to implement this, my recommended next step is boring on purpose:

    1. Pick one content type (like pages or posts).
    2. Ship it end-to-end with Payload + Next.js including preview and revalidation.
    3. Only then expand the schema.

    And if you’re still deciding on the front end side of headless, this perspective on the Best frontend for headless CMS is a decent jumping-off point.

    Build the smallest thing that proves the workflow—then scale it. That’s how you avoid rebuilding it again next year.

  • Headless CMS and Next.js: Your 2026 Guide

    Discover how to effectively integrate Headless CMS with Next.js in 2026, enhancing your web development projects.

    Featured image for Getting Started with Headless CMS and Next.js in 2026

    Getting Started with Headless CMS for Next.js

    A Headless CMS gives you an admin UI for editors and an API for developers—without forcing you into a specific front end. Next.js is a great match because it can render content a bunch of different ways depending on the page and traffic.

    Understanding Headless CMS

    A Headless CMS stores content and exposes it over an API (REST and/or GraphQL), while your Next.js app handles routing, layouts, and rendering.

    Here’s what actually matters in the 2026 day-to-day:

    • Flexibility: you can redesign the front end without rewriting content models. That’s not theoretical; it’s the difference between a 2-week refresh and a 2-month “replatform.”
    • Omnichannel delivery: the same “Article” can power the website, an in-app help center, and even an internal dashboard. You’re not duplicating copy across systems.
    • Separation of concerns: editors work in the CMS, devs work in Next.js. That separation reduces merge conflicts, but it also forces you to define content types clearly (which is a good pain).

    One important nuance: “headless” doesn’t automatically mean “faster.” You still have to choose SSR vs SSG vs ISR wisely, and you still need caching. Otherwise you just moved the bottleneck.

    Benefits of Using Headless CMS with Next.js

    1. Enhanced Performance: Next.js gives you SSR and SSG, so you can ship fast pages and keep SEO-friendly HTML. But you only win if you avoid doing live CMS fetches on every request for pages that don’t change hourly.
    2. Developer Experience: file-based routing, server components (where it fits), and a big ecosystem make integration pretty straightforward. That said, a sloppy content model will still make your front end miserable.
    3. Scalability: scaling in a headless world usually means (a) scaling API reads, (b) controlling cache invalidation, and (c) keeping editorial workflows sane. Next.js helps, but it won’t magically fix content chaos.

    Tradeoff I’ll call out: headless setups can become “distributed systems” surprisingly fast—CMS, web app, image CDN, search, preview environment, webhook handlers. You get power, but you also get more moving parts to monitor.

    Popular Headless CMS Options for Next.js

    Several CMS options are compatible with Next.js. These three come up constantly for good reasons:

    • Payload: open-source, TypeScript-native, and developer-first. It’s a strong choice when you want to own your data model and keep types tight.
    • Sanity: great real-time editing and collaboration, plus a flexible schema. Teams with lots of editorial iteration tend to like it.
    • Strapi: open-source with a plugin ecosystem and lots of community knowledge. It’s often the “default” pick for teams that want something familiar.

    My opinionated filter when choosing:

    • If your team cares about TypeScript end-to-end and you want to keep CMS logic close to your app, Payload is hard to beat.
    • If editors need live collaboration and structured content will evolve weekly, Sanity shines.
    • If you need something straightforward and you’re okay spending time on config and plugins, Strapi can work.

    Resources for Next.js Headless CMS Templates

    Templates can save you time, but they can also bake in odd decisions (auth assumptions, caching patterns, folder structure). So I treat them like scaffolding, not architecture.

    When you evaluate a template, look for:

    • Customization: can you change the content model without fighting the starter? If every field is hardcoded into a UI component, that starter will age badly.
    • Community and Support: active issues, recent commits, and real examples. A dead starter is technical debt with a README.
    • Documentation: not just “run npm install,” but details on preview, webhooks, and deployment.

    Recommended Templates:
    – Starter templates for Payload CMS can often be found on their official GitHub repository.
    – Next.js templates on platforms like Vercel or Template resources to quickly deploy your applications.

    One more practical tip: before you commit, run a “content change drill.” Add a field to the content type and see how many places in the front end you have to touch. If it’s more than you expected, your model or rendering strategy needs work.

    Using Payload CMS with Next.js

    Payload CMS is a solid choice with Next.js in 2026 because it doesn’t fight the way modern Next apps are built. If you like TypeScript, predictable local dev, and owning your schema, it’s a comfortable setup.

    Why Choose Payload?

    Payload is designed to integrate cleanly with Next.js, and a few details make it genuinely pleasant:

    • Comprehensive API: you can query content without inventing a custom backend layer. That’s fewer servers and fewer “why is this endpoint different?” conversations.
    • Typescript Support: typed collections reduce dumb mistakes—like shipping a component that assumes author.name exists when your model uses displayName.
    • Document-based Structure: it maps nicely to things like pages, posts, case studies, docs, and products.

    Where Payload can bite you: permissions and drafts. It’s powerful, but it means you have to be explicit about read access, preview behavior, and what “published” really means.

    Here’s the real-world pattern I’ve seen work: treat the CMS like a product. Version your schema changes, review access rules like you review code, and don’t let “just add a field” happen directly in production.

    Setting Up Payload CMS

    I’ll lay this out as a practical build checklist—the order matters because it prevents you from painting yourself into a corner.

    1. Install Payload:
      Run the command to set up a new Payload project directly in your Next.js app:
      bash
      npx create-payload-app

    2. Configuration:
      Configure your Payload CMS settings in the payload.config.ts file. This includes defining your collections, fields, and permissions.

    Start small. One collection. A couple fields. Get the full loop working (create → preview → publish → render) before you model your entire company.

    A sane first collection:
    – pages: title (text), slug (text), layout (blocks), publishedAt (date), status (draft/published)

    Then lock down access rules:
    – Public users: can read only published pages
    – Editors: can read/write drafts
    – Admins: can manage users and globals

    1. Fetch Data:
      Use Payload’s API to fetch content. For instance:
      javascript
      import { usePayload } from 'payload-hooks';
      const { docs } = usePayload('my-collection');

    Practical note: be careful with where you fetch.

    • For mostly-static marketing pages, prefer build-time/ISR fetches and cache aggressively.
    • For authenticated dashboards or frequently changing data, SSR (or server actions) can make sense.

    Don’t default to “fetch on every request” because it’s easy. Your CMS will become your bottleneck the first time a campaign spikes traffic.

    1. Deploy:
      Finally, deploy your application to a platform like Vercel, which provides an ideal environment for Next.js applications.

    Before you hit deploy, wire up:
    – environment variables for database + secrets
    – a preview environment (or branch deployments)
    – a webhook strategy for revalidation (so content updates actually show up)

    This is the part people skip, and then they wonder why editors are doing hard refreshes and Slack’ing screenshots.

    Payload CMS in Action

    I’ll give you two examples: one from the wild (linked), and one I’ve personally seen play out on teams.

    First, there’s a public case study: Michigan Business adopted Payload CMS for their content needs. The thing to notice in setups like that isn’t “they used Payload,” it’s why: faster iteration, clearer separation between content updates and code deploys, and less friction for the people who actually maintain the site day to day.

    For more in-depth information, refer to the source of the payload integration’s success story in Michigan here.

    Now the gritty example I see a lot: a team starts with a simple marketing site, then adds a resources hub, then adds gated PDFs, then adds a partner directory. At first, they hardcode a bunch of stuff because “it’s just a few pages.” Six months later, every change requires a developer, and the CMS is basically a blog no one trusts.

    Here’s how I’d run that migration to Payload + Next.js without breaking everything:

    1. Inventory content: list every page type (landing page, case study, blog post, docs page). Count them. Identify what actually changes weekly.
    2. Define a minimal content model: don’t model the universe. Model what you ship. If you need flexible layouts, use blocks—but keep the block set small.
    3. Build one vertical slice: create one page type end-to-end: CMS entry → API fetch → Next.js route → SEO tags → preview.
    4. Add preview early: if editors can’t preview drafts, they’ll either publish risky changes or stop using the CMS.
    5. Set up revalidation: publish should trigger an update. If you rely on “wait for the cache,” people will lose confidence.
    6. Backfill content: migrate content in batches, not a giant weekend cutover. You’ll catch model gaps faster.

    Common mistakes (I’ve made a couple of these myself):

    • Overusing “blocks”: blocks are great, but unlimited freedom turns into inconsistent pages and a messy front end. I cap block types and I document when to use each.
    • Forgetting access rules: someone will accidentally expose drafts if you don’t explicitly protect them.
    • Not planning images: if your media pipeline is an afterthought, you’ll end up serving huge images and tanking performance.
    • No rollback plan: content changes can break layout. Keep a way to revert quickly—versioning, backups, or at least a “duplicate page” workflow.

    If you want more reading around architecture decisions, I’ve seen good overviews like Why Payload CMS is the Best CMS for NextJS and broader comparisons such as Next.js CMS: Best Headless CMS Choices for 2026. I don’t treat any single post as gospel, but they’re useful for framing tradeoffs.

    Headless CMS with Next.js content flow diagram

    Conclusion

    Headless CMS + Next.js isn’t a trend in 2026—it’s the default shape for teams that want speed without handing the keys to a fragile theme layer.

    But here’s the honest part: you only get the payoff if you run it like a system, not a pile of tools. Your content model needs boundaries, your rendering strategy needs intent, and your editor workflow needs to match how your team actually works.

    A quick persona story I’ve watched play out: a product marketer wants to launch 12 new pages for a campaign next Tuesday. The dev team is already booked. In a coupled CMS, that request turns into “pick a template and pray.” In a good headless setup, the marketer duplicates a page, swaps blocks, updates copy, previews it, and hits publish—while the dev team stays focused on the product.

    That’s the win. Not “API-first,” not buzzwords. Just fewer bottlenecks.

    If you’re about to implement this, my recommended next step is boring on purpose:

    1. Pick one content type (like pages or posts).
    2. Ship it end-to-end with Payload + Next.js including preview and revalidation.
    3. Only then expand the schema.

    And if you’re still deciding on the front end side of headless, this perspective on the Best frontend for headless CMS is a decent jumping-off point.

    Build the smallest thing that proves the workflow—then scale it. That’s how you avoid rebuilding it again next year.

  • Benefits of Using WordPress as Your Main CMS

    Explore the advantages of using WordPress as your main CMS solution. Learn about its integration features, user management capabilities, and plugin functionalities. Discover why it’s a top choice for marketers, web developers, and business owners.

    Featured image for Benefits of Using WordPress as Your Main CMS Solution

    Benefits of Using WordPress as a CMS

    WordPress has established itself not just as a blogging platform but as a full-fledged CMS that supports various website types. Its flexibility, user-friendliness, and extensive ecosystem make it a top choice.

    I’m biased toward “boring and reliable” CMS setups: clean publishing flows, predictable permissions, and integrations that don’t require a custom app for every little thing. WordPress does that well—if you set it up with a little discipline.

    Versatile CMS capabilities

    WordPress is incredibly versatile. Organizations use it for everything from simple blogs to complex eCommerce sites. That range is largely due to themes and plugins that cover most common needs.

    A practical example: I’ve helped a small services business start with a five-page marketing site, then add lead magnets, a knowledge base, and eventually paid training. We didn’t swap platforms. We just added pieces in stages (forms + CRM sync first, then membership, then payments) and kept the editorial workflow stable the whole time.

    WooCommerce is the obvious eCommerce path, and it’s solid when you keep the stack lean. Membership plugins can enable subscription models without heavy coding. The tradeoff: you have to think like a site owner, not a plugin collector. Every added feature is also something you’ll maintain.

    User-friendly interface

    One of WordPress’s strongest advantages is its user-friendly interface. Marketers and business owners can create and manage content without extensive technical knowledge, and the dashboard is familiar enough that new hires don’t need a week of training.

    The real win I see in practice is speed. When the editor experience is straightforward, teams publish more consistently. Campaign landing pages don’t get stuck in “dev queue” for two weeks. That agility matters more than people admit—especially when you’re reacting to product updates, seasonal promos, or PR.

    Strong community support

    With millions of users worldwide, WordPress has deep community support. That turns into real-world benefits: troubleshooting forums, tutorials, meetups, documentation, and a huge talent pool.

    It also means there are established “known good” ways to do common tasks (caching, backups, migrations, security hardening). When something breaks at 4:45pm on a Friday, it’s nice not to be the first person on earth to hit that problem.

    Integration with other platforms

    WordPress excels at integrating with other platforms and tools—analytics, marketing automation, CRMs, payment gateways, and email providers.

    A solid starting point is mapping what data has to move where (forms → CRM, orders → accounting, events → email list) and then choosing integrations that are well-supported. If you want a scan of common directions teams are going, Top WordPress CMS Integrations for 2026 is a useful reference.

    One caution from experience: integrations are where “quick wins” become long-term liabilities. If you duct-tape five SaaS tools together with low-quality connectors, you’ll eventually have silent failures—missing leads, duplicate contacts, broken UTM attribution. I’ve seen it. The fix is boring: fewer moving parts, better logging, and a monthly check that key flows still work.

    WordPress User Management and Customization

    The flexibility of WordPress isn’t limited to content types and layouts. User management and admin customization are where WordPress can feel either wonderfully controlled… or like a shared password free-for-all. The difference is how intentional you are.

    Comprehensive user roles and permissions

    With WordPress, you can assign roles to users—administrator, editor, author, contributor, subscriber—so you’re not giving everyone the keys to the kingdom.

    Here’s the setup I use on most marketing teams (and it’s saved me pain more than once):

    1. Give marketing “Editor,” not “Admin.” Editors can publish and manage content without being able to install random plugins.
    2. Keep Admin accounts limited to the people who actually maintain the site (dev, ops, or a trusted agency).
    3. Use “Author” for specialists (SEO writers, contractors) who should publish their own posts but not touch site-wide settings.
    4. Create a process for access requests. A simple ticket or Slack message with “why + when it’s needed” prevents privilege creep.

    Common mistake I still see: a company hires an intern, gives them Admin “just for today,” and forgets. Months later, a theme gets edited directly in production, or a plugin is installed that breaks checkout. Not malicious—just preventable.

    Customizable admin panel

    The admin panel can be customized to match how your team works. Using plugins like the WordPress Admin Panel Customization Plugin, you can clean up menus, hide irrelevant settings, and reduce “where do I click?” confusion.

    A real example: I worked with a nonprofit where volunteers published weekly updates. We removed anything not related to posts, media, and a single custom “Events” section. Support requests dropped fast because the interface stopped feeling like a cockpit.

    My rule: customize for clarity, not for aesthetics. If you hide too much without documenting it, people get stuck and start making workarounds.

    White label solutions

    If you manage multiple client sites, a white-label WordPress plugin can rebrand the backend so it matches the client’s branding. Agencies love this.

    Tradeoff (and I’m opinionated here): white labeling shouldn’t be used to obscure what the client is actually running. I’ve inherited “white-labeled mystery sites” where basic maintenance was impossible because everything was renamed. Branding is fine. Hiding the plumbing isn’t.

    Understanding WordPress Plugins

    Plugins are the superpower and the trap. They expand WordPress functionality so you don’t have to build everything from scratch—but too many plugins (or the wrong ones) will slow the site, complicate updates, and increase the chance of conflicts.

    Essential plugins for functionality

    There are over 65,000 plugins available in the WordPress repository, covering everything from SEO to security to performance.

    When I’m choosing plugins, I follow a simple checklist:

    1. Define the outcome first. “We need better SEO” is vague; “we need editable titles/meta and XML sitemaps” is actionable.
    2. Pick plugins that do one job well. All-in-one bundles sound convenient until you need to swap one feature.
    3. Check maintenance signals. Recent updates, active installs, and support responsiveness matter.
    4. Test in staging. Always. Especially on WooCommerce sites.

    Security plugins can help mitigate common threats by adding layers like login throttling, file change detection, and basic hardening. E-commerce plugins enable payment systems while keeping data handling consistent.

    A mistake I’ve seen repeatedly: installing three plugins that all try to do caching, optimization, and minification. The site gets slower, not faster, because they fight each other. Start with one performance tool, measure, then adjust.

    Keeping up with market trends

    According to recent WordPress statistics, WordPress controls 62.8% of the CMS market. That scale is a big deal because it drives plugin innovation and long-term ecosystem support.

    But “new” isn’t automatically “better.” My approach is to schedule plugin review like routine maintenance:

    • Monthly: update plugins/themes, check critical flows (forms, checkout, search), scan error logs.
    • Quarterly: remove unused plugins, replace overlapping tools, confirm backups restore cleanly.
    • Before big campaigns: freeze major changes and only ship what you can roll back quickly.

    That cadence is how you keep the flexibility without waking up to a broken site the morning of a launch.

    Conclusion

    WordPress is a strong choice for businesses that want a CMS they can actually live in—publish fast, collaborate safely, and extend features as the business grows. The upside is real: integrations, roles/permissions, and a plugin ecosystem that can take you from “basic site” to “serious platform.”

    If you’re considering WordPress, your next step is simple: list the workflows you can’t afford to break (publishing approvals, lead capture, checkout, CRM sync), then evaluate WordPress themes/plugins based on those workflows—not on how pretty the demo looks.

  • Top Free WordPress Security Plugins in 2026

    Discover the best free WordPress security plugins in 2026 that protect your site from attacks and vulnerabilities.

    Featured image for The Best Free WordPress Security Plugins for 2026

    The Best Free WordPress Security Plugins for 2026

    Most WordPress security problems aren’t Hollywood hacking scenes. They’re boring:

    • A plugin update gets delayed “until after the campaign.”
    • Someone reuses a password from an old breach.
    • The login page gets brute-forced all night.
    • A compromised admin account installs a sketchy plugin, and now you’re hosting a spam farm.

    A good free security plugin won’t make you invincible, but it will reduce your attack surface, catch obvious issues early, and give you a fighting chance when something goes sideways.

    Here are the free tools I actually see used in the wild, plus what I’d watch out for.

    1. Wordfence Security

    Wordfence is the “default pick” for a lot of site owners for a reason. The free version gives you a web application firewall (WAF), a malware scanner, and brute-force protection. It’s also one of the few plugins that makes you look at your traffic like an adult—you can see what’s hitting /wp-login.php, which IPs are being noisy, and what’s getting blocked.

    Where Wordfence shines (free tier):

    • WAF rules that block common exploit patterns
    • Malware scanning and file change detection
    • Login security controls (rate limiting, lockouts)
    • Visibility: live traffic, blocked requests, attack patterns

    Common mistake I keep seeing: people install Wordfence, feel safer, and then ignore the alerts. If you’re going to run it, you need to tune notifications so you don’t end up with inbox fatigue.

    How I configure it on a typical small business site:

    1. Turn on brute-force protection and set lockouts (don’t go extreme; you can lock out legit users).
    2. Disable XML-RPC if you don’t need it (a lot of sites don’t).
    3. Run an initial full scan, then schedule scans during off-hours.
    4. Check the “Live Traffic” view once a week for a month. After that, monthly is fine unless you’re under active attack.

    If you run WooCommerce or membership sites, be careful with aggressive blocking. I’ve seen stores block payment gateway callbacks and break checkouts—usually because someone flipped on strict rules without testing.

    2. Sucuri Security

    Sucuri Security is a solid “audit and integrity” tool. In practice, I like it when I want a simple security activity trail and file integrity monitoring without making the dashboard feel like a SOC.

    What it’s good at:

    • Security activity auditing (who did what, when)
    • File integrity monitoring (unexpected file changes)
    • Post-hack actions (useful if you’re recovering)

    Tradeoff: the plugin alone isn’t a magic shield. People confuse “scanner alerts” with “protection.” The alerts are still valuable because they push you to fix the root cause: outdated plugins/themes, suspicious file changes, or admin activity you don’t recognize.

    Mistake I’ve seen: site owners assume Sucuri will stop a brute-force attack by itself. You still need login protection (from Sucuri or another plugin) and decent hosting-level controls.

    3. iThemes Security

    iThemes Security packs a lot into one plugin: enforcing strong passwords, limiting login attempts, 2FA options, and general hardening.

    What it’s good for:

    • “Set it and forget it” hardening options
    • Strong password enforcement (huge, honestly)
    • Limiting login attempts and tightening admin behavior

    Where people trip: turning on every feature at once. I’ve watched teams enable aggressive file change detection + database tweaks + admin URL changes, and then forget what they changed. The next dev comes in, things don’t match documentation, and now you’ve got a mystery box.

    My approach: enable it in layers.

    • Start with password policy + login rate limiting
    • Add 2FA for admins and editors
    • Only then consider deeper hardening features

    4. All In One WP Security & Firewall

    This one is popular because it’s organized like a checklist—basic, intermediate, advanced—so non-security folks don’t feel lost.

    What it’s good at:

    • Login lockdown and brute-force protection
    • Basic firewall rules
    • IP blacklisting / whitelisting
    • A UI that encourages gradual improvement

    The tradeoff: “advanced” settings can cause real breakage if you don’t understand them. I’ve seen a site block legitimate RSS access and third-party integrations because someone toggled a rule without knowing what endpoint it affected.

    If you’re not sure, move one step at a time, test your contact forms, test checkout, test search, and check that your caching/CDN still behaves.

    5. MalCare Security

    MalCare’s big promise is simple: scan, detect, and help you clean up without burning a weekend. Even on the free side, it’s focused on malware detection and monitoring.

    Where it helps:

    • Malware scanning and alerts
    • Quick visibility into whether you have a real infection vs. “something feels off”

    Reality check: no scanner catches everything perfectly. You still need backups and an update routine. But a tool that spots infections early can be the difference between a 30-minute fix and a full “Google flagged my domain” nightmare.

    Importance of Free Security Plugins

    Free plugins aren’t “toy versions.” They usually cover the 80/20: stop the dumb automated stuff, warn you about risky changes, and give you controls that WordPress doesn’t ship with by default.

    But here’s the part people don’t like hearing: security plugins don’t replace basic hygiene.

    • Update WordPress core.
    • Update plugins/themes.
    • Remove what you don’t use.
    • Use real passwords and 2FA.
    • Keep clean backups.

    In 2026, it is reported that 13,000 WordPress sites are hacked daily due to outdated plugins and weak passwords, showcasing the critical need for proactive security measures (TechTide Solutions). If that number is even close to reality, it matches what I’ve seen firsthand: most compromises aren’t “zero-day genius.” They’re old vulnerabilities plus easy credentials.

    A practical “first hour” setup (what I’d do on a fresh install):

    1. Install one security plugin (don’t stack three WAFs).
    2. Turn on login protection (rate limiting + lockouts).
    3. Enable 2FA for admins.
    4. Run a full scan.
    5. Delete unused plugins/themes.
    6. Set a weekly update slot on your calendar.

    If you do just that, you’re already ahead of a lot of sites that get popped.

    Exploring WordPress SSO Solutions for Enhanced Security

    SSO isn’t about convenience. It’s about control.

    When you move logins to a central identity provider (Google Workspace, Microsoft Entra ID/Azure AD, Okta, etc.), you get a few things WordPress alone struggles with:

    • consistent 2FA enforcement
    • quick offboarding (disable one account, access dies everywhere)
    • fewer reused passwords floating around

    Yes, it makes login smoother. But the security win is that WordPress stops being the primary password vault for your team.

    MiniOrange SSO

    MiniOrange SSO is one of the more common WordPress SSO plugins because it supports multiple identity providers and different protocols depending on what you’re using (SAML, OAuth/OIDC).

    It can integrate with Google, Facebook, and Microsoft, which covers the reality for most small orgs: people already have those accounts.

    Benefits of SSO in WordPress Security

    1. Reduced Password Fatigue: Users are less likely to use weak or reused passwords since they only need to remember one.
    2. Streamlined Login Process: SSO allows for quicker access, improving user experience.
    3. Centralized User Management: Admins can manage user access more efficiently, monitoring who has access to what.

    I’ll add a fourth, because it’s the one that saves your skin during incidents:

    1. Faster containment: if you suspect an account is compromised, you kill the identity provider session and rotate credentials in one place.

    A real SSO scenario (where it helped)

    A team I worked with had a WordPress site with ~20 authors and editors. Turnover was normal—contractors, guest writers, marketing interns. The site didn’t get hacked through some exotic exploit. Someone left the company and their WordPress user never got removed. Months later, that same credential set worked (password reuse is undefeated), and suddenly new “admin” users appeared.

    Nothing fancy. Just neglected access.

    After switching to SSO tied to their Google Workspace:

    • offboarding became “disable Google account”
    • 2FA was enforced centrally
    • WordPress stopped storing the primary password people cared about

    That change didn’t solve every security problem, but it shut down a whole class of them.

    Step-by-step: how I roll out SSO safely

    SSO can absolutely lock you out if you rush it. Here’s the rollout order I trust:

    1. Create a break-glass admin account
    2. A separate WordPress admin with a long random password.
    3. Store it in a password manager.
    4. Do not use it day-to-day.

    5. Pick one identity provider

    6. If you’re already on Google Workspace or Microsoft, start there.
    7. Don’t add multiple IdPs “just in case” unless you have a real reason.

    8. Enable SSO for a pilot group

    9. Start with yourself and one other admin.
    10. Confirm you can log in, log out, and log back in.

    11. Map roles carefully

    12. Make sure an “employee” in the IdP doesn’t become an “administrator” in WordPress by default.
    13. Least privilege wins.

    14. Enforce 2FA at the identity provider

    15. This is the whole point. If you don’t enforce MFA/2FA, you’ve just moved passwords around.

    16. Roll out to editors/authors

    17. Communicate what’s changing.
    18. Expect questions like “why can’t I use my old login?”

    19. Disable WordPress password login (optionally)

    20. Only after you’ve proven SSO works.
    21. Keep the break-glass admin as your fallback.

    Common SSO mistakes (I’ve seen all of these)

    • No break-glass admin → one misconfig, and you’re locked out.
    • Role mapping too generous → users get admin when they shouldn’t.
    • Not enforcing 2FA in the IdP → you gain convenience, not security.
    • Ignoring service accounts → integrations still need access; plan them.

    As a CEO, I’ve dealt with countless security issues, and one of my biggest lessons learned is that managing user access is just as crucial as protecting the website itself. Implementing an SSO solution can drastically reduce potential entry points for attackers.

    Conclusion: Your Security Strategy Matters

    The uncomfortable truth: security plugins are only as good as your habits.

    If you install a plugin and never update anything again, you’ll still get hit. If you lock down logins but keep five abandoned plugins active, you’re still exposed. If your team shares one admin account, you’ve basically opted out of accountability.

    With over 11,334 new vulnerabilities disclosed in the WordPress ecosystem last year (TechTide Solutions), you don’t need to be paranoid—you need to be consistent.

    Here’s the security strategy I push because it holds up under real-world mess:

    • Pick one main security plugin (Wordfence or iThemes or All In One, etc.). Stacking overlapping tools tends to create conflicts and alert fatigue.
    • Harden logins (rate limits + 2FA for privileged roles).
    • Patch like it’s your job (weekly schedule; emergency updates when a critical bug drops).
    • Backups you’ve actually tested (a backup that can’t be restored is a feel-good file).
    • Access control that matches your org (remove users, enforce least privilege, consider SSO once your team grows).

    One more thing that doesn’t get said enough: measure the boring stuff.

    • When was the last update applied?
    • How many admin users exist right now?
    • How many plugins are inactive but installed?
    • Do you know where your backups live?

    If you can answer those without guessing, you’re in good shape.

    Next step: pick one plugin from the list, implement the “first hour” setup above, and put a recurring calendar block for updates. Security that isn’t scheduled is security that won’t happen.

    My Experience With This

    I’m Mobeen Abdullah. I run Revnix, and I’ve spent over a decade building cloud-native solutions and security strategies. I’ve also had to do the unglamorous part: cleaning up compromised sites, tracing how access was gained, and explaining to stressed-out teams why “we installed a security plugin” didn’t prevent a mess.

    One incident I still remember: a content site started throwing random redirects only on mobile. Desktop looked fine. The owner thought it was an ad network problem. It wasn’t.

    What actually happened was classic:

    • an outdated plugin provided the entry point
    • a malicious PHP file got dropped into a writable directory
    • the malware served conditional redirects (user-agent based), so the team didn’t see it during quick checks

    The fix wasn’t just “scan and delete.” We had to:

    1. Put the site in maintenance mode (stop the bleeding).
    2. Rotate passwords (WordPress admins, hosting panel, database, SFTP).
    3. Reinstall clean core files (don’t trust compromised ones).
    4. Remove the vulnerable plugin and replace it.
    5. Scan + diff key directories (wp-content/plugins, wp-content/uploads, mu-plugins).
    6. Add login controls + 2FA so the next attempt was harder.
    7. Set up a weekly update cadence—because the root cause was neglect, not lack of tools.

    That’s why I’m biased toward boring, repeatable security: fewer plugins, clear ownership, and a routine. Tools help, but habits win.

    If you want more comparisons and perspectives, here are a few decent roundups worth skimming (then make your own call):

  • Best SEO Tools for WordPress in 2026

    Explore the best SEO tools for WordPress in 2026 to enhance search engine optimization and improve your site’s visibility. Discover plugins, strategies, and tips!

    Featured image for Best SEO Tools for WordPress in 2026: A Complete Guide

    Search Engine Optimization for WordPress

    Search engine optimization in WordPress isn’t a single switch you flip. It’s a system: your theme, your hosting, your content, your internal links, and (yes) a plugin or two to keep the basics consistent.

    When someone asks me, “How can a WordPress site be optimized for search engines?” I usually answer with a slightly annoying question: Optimized for what—crawling, ranking, or converting? Because I’ve seen plenty of WordPress sites that rank “okay” but convert terribly, and sites that convert great but never get discovered.

    Here’s the practical breakdown I use when I’m auditing a WordPress site.

    Basic SEO principles (the non-negotiables)

    • Keyword research (but make it realistic): Don’t just pull a list from a tool and sprinkle it around. Pick one primary query per page that matches the actual purpose of the page. Then add supporting topics you can cover without turning the post into a bloated mess.
    • Content quality that earns the click: A page can rank and still fail if the title promises one thing and the content delivers another. In 2026, “thin but optimized” content dies slowly—usually after a core update.
    • Technical SEO that doesn’t fight WordPress: WordPress can be clean, but it can also become a tangle of duplicate URLs, heavy scripts, and pages that shouldn’t be indexed. Your job is to reduce noise.

    A quick real example from my side: I worked on a WordPress blog where the team published 4–5 posts a week for months, yet organic traffic was flat. The issue wasn’t “Google hates us.” It was internal competition—five posts targeting the same keyword cluster, weak internal linking, and category/tag pages indexed by accident. We consolidated three posts into one, redirected the old URLs, noindexed tag archives, and rebuilt internal links. Traffic didn’t jump overnight, but in ~6 weeks the consolidated post started climbing while the duplicates faded (which is exactly what you want).

    How to do SEO optimization on WordPress (step-by-step)

    This is the workflow I’d use if I were setting up a WordPress site from scratch—or cleaning up a site that’s been “plugin’d to death.”

    1. Pick one SEO plugin and commit
    2. Most sites do better with one strong SEO plugin than two competing ones.
    3. If you’re still deciding, skim a curated comparison like Yoast SEO alternatives and feature sets, then choose based on your needs (single author blog vs. editorial team vs. WooCommerce).
    4. Common mistake: installing an SEO plugin, then also installing a separate schema plugin, then a separate sitemap plugin, then a separate redirection plugin… and suddenly you’ve got overlapping output and weird page behavior.

    5. Set your indexing rules (this is where sites accidentally shoot themselves)

    6. Decide what should be indexed: posts, pages, product pages.
    7. Decide what usually shouldn’t: tag archives (often), author archives (often), internal search pages (almost always).
    8. Common mistake: letting WordPress generate a thousand thin archive pages and then wondering why crawl budget feels wasted.

    9. Fix permalinks before you publish a lot

    10. Clean URLs age well. Changing them later is a redirect project.
    11. Use a readable structure. Avoid dates unless your content is truly time-sensitive.

    12. Connect Google Search Console and actually read it weekly

    13. Search Console isn’t just “nice to have.” It’s where you’ll see indexing issues, query patterns, and pages that are getting impressions but not clicks.
    14. What I look for: pages with high impressions and low CTR (rewrite titles/meta), pages with rising impressions (build internal links to them), and “Crawled – currently not indexed” patterns (often thin/duplicate).

    15. Create and submit your sitemap

    16. Most SEO plugins generate this automatically.
    17. Check that it contains the pages you want indexed and doesn’t include junk.

    18. Build internal linking like you mean it

    19. If a page matters, it should receive internal links from related posts.
    20. I’ll often add 5–10 internal links to a priority page across older posts over a week—small change, measurable impact.

    Image note (use this in your post):

    Best SEO tools for WordPress in 2026 plugin settings screenshot

    If you don’t have a screenshot yet, grab one from your own WordPress dashboard (SEO plugin settings + sitemap screen). It’s more useful than stock imagery.

    Best SEO Plugins for WordPress in 2026

    If you want my blunt opinion: SEO plugins are for consistency and control, not magic. They help you produce clean metadata, manage indexing, generate sitemaps, and avoid common technical mistakes. They don’t replace good structure or good content.

    Here are the plugins I still see performing well in 2026—mostly because they’re maintained, flexible, and not trying to do everything.

    1) Yoast SEO

    Yoast is the “default” for a reason. It’s stable, it covers the fundamentals, and it’s hard to totally mess up.

    • Where it shines: editorial guidance (titles, meta descriptions), canonical controls, basic schema handling.
    • Tradeoff: the content scoring can be taken too literally. I’ve seen writers ruin flow just to get a green light.

    Common mistake I see with Yoast: people “optimize” a page by stuffing the focus keyword into every heading because the plugin nags them. Rankings don’t improve, but readability tanks.

    2) Rank Math

    Rank Math earned its popularity by giving you a lot of control without making you feel like you need a computer science degree.

    • Where it shines: built-in audits, more granular schema options, feature depth.
    • Tradeoff: more options means more ways to misconfigure things if you click blindly.

    3) All in One SEO Pack

    AIOSEO is a solid all-rounder. I’ve inherited client sites using it and rarely had to rip it out.

    • Where it shines: straightforward on-page controls, sitemaps, social previews.
    • Tradeoff: depending on your setup, you may still want a separate performance strategy (because SEO plugins don’t solve speed).

    4) SEOPress

    SEOPress is a good fit if you want something flexible and less “naggy” than some alternatives.

    • Where it shines: centralized control, clean UI, Google Analytics integration options.
    • Tradeoff: you still need to know what you’re doing—less hand-holding.

    If you want a deeper plugin-by-plugin review, I’d cross-check a dedicated roundup like Best SEO Tool for WordPress 2026 and compare that against your actual needs (site size, team workflow, ecommerce vs. content).

    The setup I’d ship (a practical mini playbook)

    If you told me “I need this live next week,” here’s what I’d do:

    1. Install one SEO plugin (Yoast or Rank Math—pick one).
    2. Noindex tag archives unless they’re intentionally curated.
    3. Ensure categories are meaningful (not 30 near-duplicates).
    4. Enable XML sitemap, submit to Search Console.
    5. Set canonical URLs correctly (especially if you have tracking parameters).
    6. Add a redirection plan (even if it’s just using the SEO plugin’s built-in redirect manager, or a lightweight redirect tool).
    7. Write title/meta templates that don’t generate junk (avoid: “Home – SiteName” everywhere).

    Real story: I once audited a WordPress site where the developer had three different plugins outputting schema. The result was conflicting structured data, weird rich result eligibility, and pages that looked “fine” until you ran them through testing tools. We removed two plugins, simplified schema, and the site’s snippets stabilized. Not glamorous, but it stopped the bleed.

    Effective SEO Strategies Without Plugins

    You can absolutely do strong SEO on WordPress without leaning on plugins—especially if you’re comfortable getting your hands a bit dirty. In some cases (lean sites, performance-first builds), fewer plugins is the whole point.

    Here’s what I’d focus on.

    Optimize WordPress settings (the boring wins)

    Permalinks
    – Set readable URLs early.
    – Avoid changing URL structures later unless you’re ready to map redirects.

    Visibility and indexing hygiene
    – Double-check you’re not blocking crawling accidentally (yes, the “Discourage search engines” checkbox still gets people).
    – Keep your navigation clean. If users can’t find pages, search engines usually struggle too.

    Internal linking (manual, but powerful)
    – When you publish a new post, immediately add 3–5 internal links from older relevant posts pointing to it.
    – Also link out from the new post to 3–5 related pages on your site.

    Common mistake: people only add internal links within the new post. Helpful—but the real leverage often comes from older posts that already have authority and traffic.

    Use Core Web Vitals as your guardrails

    Core Web Vitals aren’t some abstract “Google thing.” They correlate strongly with whether your site feels fast or annoying.

    Run a check with Google PageSpeed Insights and take the recommendations seriously—but don’t follow them like scripture.

    What I typically fix first on WordPress:

    1. Heavy images: convert to WebP/AVIF, resize to actual display dimensions.
    2. Too many fonts/weights: cut down. Two weights is often enough.
    3. Bloated page builder layouts: simplify sections; avoid stacking sliders, animations, and background videos.
    4. Caching: ensure page caching is actually enabled and working (you’d be shocked how often it isn’t).

    Persona anecdote: I worked with a small ecommerce brand whose product pages were taking 6–8 seconds to become usable on mobile. Their SEO “strategy” was publishing more blog posts. We didn’t publish a single new post for a month—we just compressed images, killed an unused popup script, reduced font loads, and fixed caching. Conversions improved first. Rankings followed later.

    Content optimization that doesn’t feel like homework

    Refresh content on purpose
    – Update posts that are slipping (Search Console will show declining clicks).
    – Add missing sections that address real questions.
    – Improve intros that don’t match the query intent.

    Use multimedia as clarification, not decoration
    – Add images that explain something (screenshots, comparison tables, short “how to” clips).
    – Use descriptive filenames and alt text.

    Common mistake: swapping a few words and changing the date. That’s not an update. A real update adds value: new steps, new screenshots, updated recommendations, removed dead advice.

    Conclusion

    In 2026, good WordPress SEO is mostly about doing the fundamentals relentlessly well: clean indexing, sensible site structure, fast pages, and content that matches intent. Plugins help—sometimes a lot—but they’re not the strategy. They’re the toolbelt.

    If you want a simple next step: pick one important page (a money page, a lead-gen page, or your best informational post) and run this mini checklist this week:

    1. Confirm it’s indexable and canonicalized correctly.
    2. Rewrite the title to match the query you actually want.
    3. Add 5 internal links to it from older relevant posts.
    4. Improve speed issues flagged in PageSpeed Insights that are clearly actionable (images, fonts, scripts).
    5. Re-submit the URL in Search Console and watch impressions/clicks over the next few weeks.

    And if you’re building out your “site basics” toolkit beyond SEO, keep going with these:
    – Best WordPress Security Plugins for 2026
    – Top Content Writing Tools for 2026
    – Top WordPress CMS Integrations for 2026

    Do the boring cleanup, pick a few pages to win, and stop installing plugins as a substitute for decisions.

  • Best WordPress Security Plugins for 2026

    Explore the best WordPress security plugins for 2026, including free options and features of top choices like Wordfence and more.

    Featured image for Best WordPress Security Plugins to Use in 2026

    Best WordPress Security Plugins to Use in 2026

    WordPress security plugins matter because most WordPress compromises aren’t movie-hacker stuff—they’re automated. Bots try credential stuffing, spray common plugin exploits, and probe for misconfigurations 24/7. The right plugin won’t replace updates and good hosting, but it will stop a lot of the low-effort damage before it lands.

    A quick stance (because mixing tools blindly is how you create conflicts):

    • If you want the strongest “all-in-one” baseline, start with Wordfence.
    • If you want a cloud firewall in front of your server, look at Sucuri.
    • If you’ve ever had to clean malware in a hurry, MalCare is built for that moment.

    Wordfence Security

    Wordfence continues to dominate as one of the most popular security plugins with over 4 million active installs. It features a robust web application firewall (WAF) that blocks malicious traffic before it reaches your site. The malware scanner compares your site files with originals and detects anomalies. Despite the extensive capabilities of the free version, premium options offer real-time threat intelligence and blocking capabilities.

    Key Features:
    – Comprehensive firewall protection.
    – Real-time threat defense feed (available in premium).
    – Malware scanning and repairing capabilities.
    – Two-factor authentication for enhanced security.
    – Detailed logging for incoming traffic monitoring.

    Where Wordfence shines in real life: when you need answers fast. The traffic log is the difference between “something’s wrong” and “oh, it’s 30k hits from a sketchy ASN hammering /wp-login.php.”

    A common mistake I keep seeing: people install Wordfence, turn on every option, then wonder why their checkout or API endpoints get rate-limited. Start with the defaults, then tighten:

    1. Enable the firewall in “optimized” mode (so it loads early).
    2. Turn on 2FA for admin accounts first.
    3. Add rate limiting gradually—watch your logs for false positives.
    4. Set alerts to weekly summaries plus immediate alerts for admin creation and plugin installs.

    Many small business owners find the free version effective when paired with strong password practices and regular updates of themes and plugins. Users on forums often recommend combining Wordfence with a service like Cloudflare for layered protection against attacks (source). I’m biased toward layered protection too—Wordfence catches app-layer mess, while an edge service soaks up noisy traffic.

    Sucuri Security

    A well-regarded name in the industry, Sucuri provides a cloud-based firewall and is known for its in-depth malware scanning capabilities. While its premium version requires a subscription, Sucuri’s free plugin offers basic security features, including security activity auditing and file integrity monitoring.

    Key Features:
    – Cloud-based firewall (WAF) that enhances performance.
    – Malware detection and removal service (premium).
    – Security hardening suggestions.

    The real advantage of Sucuri’s model is placement: a cloud WAF can block bad requests before they hit your origin server. That’s not just “security”—it’s stability. If you’ve ever watched your CPU peg at 100% during a login flood, you know why that matters.

    Tradeoff: a cloud WAF is another moving part. You’ll be touching DNS, caching rules, and sometimes fighting with cookie-based caching (especially with WooCommerce or membership plugins). Worth it, but plan an hour to test the site end-to-end after enabling it.

    MalCare

    MalCare is another excellent option, especially for those who prioritize quick malware removal. Its unique selling point is its ability to remove malware directly from your dashboard without needing to access your site via FTP.

    Key Features:
    – One-click malware removal.
    – Deep scanning for vulnerabilities.
    – Security hardening tools to safeguard your site.

    I like MalCare most for cleanup and recovery. When a site’s already infected, you don’t want a tool that only tells you “yep, you’re hacked.” You want a button that gets you back online.

    A practical workflow I’ve used on a compromised site:

    1. Put the site in maintenance mode (or at least protect wp-admin).
    2. Run MalCare’s scan, then remove malware.
    3. Immediately rotate all admin passwords and reset all sessions.
    4. Update WordPress core, themes, and plugins—then rescan.
    5. Replace any nulled themes/plugins (they’re repeat offenders).

    Common mistake: cleaning the site but keeping the same credentials. That’s how you get reinfected the next day and blame the tool.

    Top Free WordPress Security Plugins for 2026

    Free plugins can absolutely move the needle—if you’re realistic about what “free” means. You’ll usually get solid hardening and monitoring, but not always real-time protection, premium threat feeds, or hands-on cleanup.

    If I’m securing a small brochure site, a local nonprofit, or an early-stage blog on a tight budget, I’ll typically pick one of these categories (not all at once):

    • Login + hardening (reduce the easy wins)
    • SSO (reduce password risk for teams)
    • Audit + monitoring (know what changed)

    MiniOrange SAML SSO

    This plugin enhances your site’s security through Single Sign-On (SSO), allowing users to log in using existing credentials securely. It minimizes the risk associated with passwords, tackling common vulnerabilities directly.

    Key Features:
    – SSO integration for secure access.
    – Reduction in password-related breaches.

    Where MiniOrange SSO is a legit upgrade: teams. If you have editors, contractors, SEO folks, and an occasional dev hopping in, WordPress password sprawl gets ugly fast.

    A real example: I’ve seen a marketing team using shared admin credentials because “it’s easier.” One person leaves, nobody rotates the password, and six months later the login gets abused. SSO doesn’t fix every problem, but it kills that specific class of bad habit.

    Basic setup checklist (how I’d roll it out without breaking everyone’s day):

    1. Decide your identity provider first (Google Workspace, Azure AD/Entra, Okta, etc.).
    2. Configure SAML in the provider and in the plugin.
    3. Map roles carefully (Editor vs Admin). Start conservative.
    4. Test with one pilot user account.
    5. Only then, enforce SSO for the broader team.

    Common mistakes:
    – Leaving a password-based admin account as a permanent backdoor “just in case.” (Make an emergency admin, sure—but lock it down with 2FA, a long random password, and no daily use.)
    – Auto-provisioning users into Admin because it’s convenient.

    iThemes Security

    Formerly known as Better WP Security, iThemes Security offers a suite of features focusing primarily on hardening your site. Its free version includes essential tools like login lockdown, file change detection, and database backups.

    Key Features:
    – Login attempt limits to mitigate brute-force attacks.
    – Two-factor authentication options.

    iThemes is useful when you want a “turn on the basics” plugin without spending a whole afternoon tuning firewall rules. On smaller sites, the login lockdown alone can cut down noise dramatically.

    A quick “sane defaults” setup I’ve used:

    1. Enable brute-force protection (set a reasonable lockout window).
    2. Turn on file change detection—then whitelist expected changes if you deploy often.
    3. Enable 2FA for admins.
    4. Hide/limit XML-RPC if you don’t need it (but confirm you’re not breaking Jetpack or a mobile app workflow).

    Watch out for this one: file change alerts can become useless if you’re constantly updating plugins without a cadence. If you update daily, batch updates to a weekly window so your alerts mean something.

    Understanding WordPress SSO and Its Security Benefits

    What is WordPress SSO?

    Single Sign-On (SSO) technology allows users to log in to multiple applications or websites using a single set of credentials. This greatly simplifies user experience while enhancing security by reducing the number of passwords users have to manage.

    But here’s the more practical framing: SSO moves authentication out of WordPress (where you probably don’t manage it professionally) into an identity provider that does—with stronger policies, better logging, conditional access, and cleaner offboarding.

    Security Benefits of Using WordPress SSO

    Implementing SSO can drastically diminish the likelihood of password-related breaches. By ensuring that users do not have to remember multiple passwords, you significantly decrease the potential for credential abuse. This also streamlines the login process, making it less cumbersome for users while enhancing site security overall.

    The benefits that actually matter in day-to-day operations:

    • Centralized offboarding: when someone leaves, disabling their Google/Azure/Okta account can cut access instantly—no scavenger hunt through wp-admin.
    • Enforced MFA: you can require multi-factor at the identity provider level, not “if users feel like it.”
    • Fewer shared secrets: less password reuse, fewer sticky notes, fewer “set it to Summer2026!” disasters.
    • Better audit trails: identity providers tend to have clearer sign-in logs than WordPress alone.

    A step-by-step rollout that won’t torch your access:

    1. Inventory users in WordPress: who needs access, what role, and why.
    2. Pick an IdP you already pay for (Google Workspace and Microsoft are the usual suspects).
    3. Pilot SSO with 1–2 admins and one editor.
    4. Set an emergency access plan: one break-glass admin account, stored securely, with 2FA.
    5. Enforce MFA in your IdP policies.
    6. Communicate the change to your team (what button to click, what to do if locked out).

    Common SSO mistakes I’ve watched teams make:

    • Locking themselves out by enforcing SSO before testing role mapping. Always pilot first.
    • Ignoring plugin conflicts with membership/checkout flows. If you run WooCommerce or a membership plugin, test login/logout, password reset, and account pages.
    • Treating SSO as “done.” You still need updates, least-privilege roles, and monitoring. SSO reduces one big risk bucket; it doesn’t patch vulnerable code.

    In conclusion, securing your WordPress site in 2026 requires careful consideration of the plugins you choose. By integrating a robust security plugin like Wordfence, Sucuri, or MalCare, along with utilizing free options and understanding the benefits of technologies like SSO, you can significantly reduce your vulnerability to attacks. Remember, regular updates and best security practices are as vital as the tools you implement. Explore your options and ensure your website stands strong against potential threats. For further insights, check out our guide on top WordPress CMS integrations for 2026!

  • Top 5 Emerging AI Technologies for Everyday Life

    Discover the top 5 emerging AI technologies that are transforming everyday life. Learn how AI applications are shaping our world.

    Featured image for Top 5 Emerging AI Technologies for Everyday Life

    Featured image for Top 5 Emerging AI Technologies for Everyday Life

    Understanding AI Technologies

    AI technologies have evolved significantly, but the useful part isn’t just “better models.” It’s the surrounding ecosystem: apps that actually plug into calendars, docs, inboxes, help desks, and analytics tools without you needing to duct-tape everything together.

    Here’s the framing I use when I’m evaluating anything branded as “AI”:

    • What job is it doing? (Drafting, searching, summarizing, planning, classifying, deciding.)
    • Where does it get its data? (Your files? The open web? A curated knowledge base?)
    • How does it fail? (Confident wrong answers, missing context, privacy leaks, weird automation loops.)

    If you can answer those three, you’ll make better choices than 90% of the market.

    Generative AI (content that starts somewhere)

    Generative AI is the most visible category because it produces stuff you can see: text, images, audio, even snippets of video. The practical win is speed—getting from “blank page” to a decent first draft in minutes.

    A real everyday example: I’ve watched marketing teams go from two-hour brainstorming meetings to a 15-minute workflow:

    1. Dump the product notes (features, audience, constraints) into the tool.
    2. Generate 10 headline angles.
    3. Pick 2–3, then ask for variants by tone (direct, playful, technical).
    4. Have a human do the final pass for accuracy and brand voice.

    That workflow is why companies are utilizing generative AI in creative industries to streamline content creation—because it removes the slowest step: the beginning. And it’s not niche anymore. In 2026, 68% of businesses reported using generative AI for creating marketing materials, which matches what I’m seeing in the field: the “first draft” use case has basically gone mainstream.

    Tradeoff (and it’s a big one): generative AI will happily produce plausible nonsense. The common mistake is treating it like a source of truth. I’ve seen teams publish a “stat” that was never real because someone forgot to verify a claim before it went into a deck.

    My rule: use it for structure, drafts, variations, and synthesis—then verify anything factual like you would with an intern who’s fast but overconfident.

    Agentic AI (AI that does tasks, not just answers)

    Agentic AI is where things get more interesting—and a little riskier. These systems don’t just respond to prompts; they can take actions: schedule meetings, send messages, update a ticket, pull a report, or chain together multiple steps.

    In theory, it’s your “digital operator.” In practice, it’s only as good as:

    • the permissions you give it,
    • the tools it can access,
    • and the guardrails you set.

    This isn’t hypothetical. The 2026 report by NVIDIA points out that enterprise AI adoption is maturing, and more corporations are using autonomous agents to drive efficiency and reduce operational costs. I buy that—not because it sounds nice, but because agents map directly to expensive labor: triage, coordination, follow-ups, and routine analysis.

    A concrete scenario I’ve implemented (in various forms): support triage + routing.

    • Agent reads an incoming request.
    • Classifies urgency and topic.
    • Checks for missing info (account ID, screenshots, error logs).
    • Creates a ticket with the right tags.
    • Routes to the correct queue and suggests a first response.

    The human still approves the final outbound message (because brand + liability), but the agent clears the messy intake work.

    Common mistake: people skip the “boring” part—permissions and audit trails. If an agent can email customers, you need logs, approvals, and limits. Otherwise you’re one hallucinated reply away from a compliance nightmare.

    How AI works (enough to be dangerous)

    You don’t need to become a machine learning engineer to use AI well, but you do need a working mental model.

    At its core, AI relies on algorithms trained on large datasets to learn patterns and make predictions. Machine learning (a subset of AI) improves performance over time as it sees more examples.

    The everyday impact is straightforward:

    • Prediction: “This customer is likely to churn.”
    • Classification: “This email looks like a billing issue.”
    • Recommendation: “Here are three replies that fit the tone.”
    • Generation: “Here’s a draft plan based on your notes.”

    If you’re using AI at work, the highest leverage habit I can recommend is this: keep a feedback loop. Track where it’s wrong. Save examples. Tighten prompts. Adjust your source data. Most teams never do this, then complain the tool is “random.” It’s not random—you just aren’t managing it.

    Google AI and innovations (everyday assistants)

    Google has been a frontrunner in AI development with products like Google Assistant, which shows the practical value of voice recognition and natural language processing. The killer feature isn’t novelty—it’s friction reduction. Talking is often faster than tapping, especially when your hands are full or your attention is split.

    As of 2026, Google AI is expanding capabilities toward more personalized interactions. That personalization is where assistants become genuinely useful for everyday life—reminders that understand context, suggestions based on routines, and help that’s less “command-based” and more conversational.

    What I like (and also what I’m cautious about):

    • Like: voice as an interface is incredibly forgiving. You can be messy, and it still works.
    • Cautious: personalization implies data. Always check what’s being stored, synced, and used for training or ad targeting.

    One small habit that pays off: if you’re using an assistant for daily planning, create a consistent pattern like “add to list,” “set reminder,” “schedule,” and “summarize my day.” Consistency reduces misfires.

    AI Chat and Interaction

    AI chatbots are the most “everyday” feeling slice of AI because they sit right where humans already are: websites, apps, help centers, internal company portals, and sometimes your phone.

    But here’s the honest truth from someone who’s watched chatbot rollouts go well and go terribly: a chatbot is only as good as the context you give it and the exit ramps you design. Without those, it becomes a fancy way to frustrate users.

    What’s changing with newer chat systems is the interaction style. It’s less like filling out a form, more like working with a junior teammate—ask a question, clarify, iterate.

    Perplexity AI

    Perplexity AI is a good example of chat that aims for accurate, contextual responses rather than purely “creative” output. It uses advanced natural language processing to handle complex queries, and the best use case is when you need a quick, usable answer without digging through ten tabs.

    A real workflow I’ve used (and recommended) for research-heavy tasks:

    1. Ask a precise question, not a topic. Example: “What are the tradeoffs between agentic AI and rule-based automation for support triage?”
    2. Request constraints: “Keep it to 7 bullets, include failure modes.”
    3. Interrogate the answer: “What assumptions are you making?” “What would change this recommendation?”
    4. Cross-check critical claims before you rely on them in a decision.

    That last step matters. People treat chat like a search engine, then forget that chat can sound sure even when it’s wrong.

    On the business side, tools like this are favored because they scale: they can handle many inquiries simultaneously, which reduces wait times. And that shows up in metrics. Studies show that implementing AI chat solutions can increase customer engagement by 30%, which lines up with what I’ve seen when the bot is actually helpful and doesn’t trap people in a loop.

    Common mistake I keep seeing: companies deploy a chat widget, connect it to nothing, and expect miracles. If the bot can’t access order status, account info, policies, or product docs (or at least a clean FAQ), it just apologizes politely while doing nothing.

    Everyone AI Chat

    Everyone AI Chat is interesting because it leans into accessibility and a more human-like interaction style. That sounds fluffy until you’ve watched real users struggle.

    Here’s a scenario I’ve seen repeatedly: a nonprofit rolls out a portal for clients. The clients aren’t “tech people.” They’re busy, stressed, and on old phones. A traditional UI fails them—too many menus, too much reading, too many steps.

    A chat-first interface can reduce that burden:

    • User says what they need in plain language.
    • The system asks one clarifying question at a time.
    • It guides them to the right form, the right doc, the right next action.

    That “one question at a time” approach is underrated. It’s the difference between someone completing a task and giving up.

    Step-by-step: how I’d evaluate an AI chat tool for everyday use (personal or business):

    1. Test basic clarity: Does it ask good follow-ups, or does it guess?
    2. Test edge cases: slang, typos, mixed languages, messy requests.
    3. Test refusal behavior: What happens when it doesn’t know? Does it escalate or hallucinate?
    4. Test handoff: Can a human step in fast? Are transcripts preserved?
    5. Test privacy defaults: Is the data retained? Can you disable training? (If you can’t find this quickly, that’s a red flag.)

    My bias: I’ll take a slightly “dumber” chat tool with clean handoffs and good privacy controls over a genius bot that locks users into an opaque system.

    The next wave: chat that acts

    The real shift, which you’ll see more of through 2026, is chat moving from “answering” to “doing.” That’s where it overlaps with agentic AI.

    Examples that are already showing up:

    • “Reschedule my meeting and notify attendees.”
    • “Summarize this thread and draft a reply.”
    • “File an expense from this receipt photo.”

    This is where mistakes get expensive. If the bot can take actions, you need confirmations (“Here’s what I’m about to do—OK?”), limits, and logs. Otherwise it’s not productivity—it’s chaos with a nice UI.

    Conclusion

    Emerging AI technologies are making everyday life faster and, sometimes, simpler—but only if you use them deliberately. Generative AI can knock out first drafts and variations. Agentic AI can take repetitive tasks off your plate. Voice assistants reduce friction when typing is a pain. And AI chat tools are becoming the front door for information and support.

    Here’s the part people skip: you still need a workflow. AI doesn’t replace decision-making; it changes where you spend attention.

    A real example from my own week: I had to prep for a cross-functional meeting with product, support, and sales. Everyone had strong opinions, and the doc trail was a mess.

    This was the process that saved me:

    1. I dumped the last two meeting notes and the support ticket themes into a generative AI tool.
    2. I asked for a one-page brief: top issues, customer impact, and proposed next steps.
    3. I had the tool generate two versions—one technical, one plain-English.
    4. I manually verified the key claims against the original notes (because if you misquote support data, you lose trust fast).
    5. I used a chat tool to pressure-test the plan: “What objections will sales raise?” “What risks are we ignoring?”

    Net result: I walked into the meeting with a clean narrative and fewer surprises. Not because AI was “smart,” but because it helped me compress messy inputs into something I could reason about.

    Common mistakes to avoid (I’ve seen all of these in the wild):

    • Using AI as a source instead of a draft partner. If it’s a fact, verify it.
    • Automating too early. People jump to agentic workflows before they’ve even nailed the manual process.
    • No guardrails. If a tool can send messages, change records, or trigger actions, add approvals and audit logs.
    • Ignoring data hygiene. Bad docs in, bad answers out. Clean your knowledge base and naming conventions.

    If you want a practical next step: pick one daily pain point—writing, scheduling, customer replies, research—and pilot one AI workflow for two weeks. Track time saved and failure cases. Keep what’s repeatable, kill what’s flaky. That’s how you actually “leverage” AI without getting burned.