Blog

  • Best WordPress Security Services: 2026 Reviews

    Explore the best WordPress security services of 2026, comparing features, prices, and effectiveness to secure your website. Learn more!

    Featured image for Best WordPress Security Services: 2026 Reviews & Comparisons

    Featured image for Best WordPress Security Services: 2026 Reviews & Comparisons

    Best WordPress Security Services: 2026 Reviews & Comparisons

    When it comes to securing your WordPress site, the options available can be overwhelming. Picking the “best” tool isn’t about brand names—it’s about coverage. You need to stop automated junk (bot logins, scans, injection attempts), catch real compromises fast, and recover cleanly when something slips through.

    I usually evaluate a WordPress security service on five things:

    • Prevention: WAF, brute-force protection, hardening, patching help.
    • Detection: malware scanning that actually finds obfuscated payloads and backdoors.
    • Response: cleanup, restore, and guidance that doesn’t waste your time.
    • Noise level: false positives can break checkout, admin, REST API, or caching.
    • Operational fit: works with your host/CDN, doesn’t tank performance, and is maintainable.

    One quick reality check: a plugin-only setup can be fine for small sites, but a WAF in front of the site changes the game because it blocks a lot of traffic before WordPress even touches it. That’s why you’ll see services like Sucuri show up in “serious” stacks more often.

    1. Sucuri Security

    Overview: Sucuri is a well-established name in the web security field. This comprehensive platform provides robust security features including a web application firewall (WAF), malware scanning, and cleanup services.

    If you’ve never used a WAF before, here’s the practical difference: it can block a pile of bad requests at the edge, so your origin server doesn’t waste CPU running WordPress just to say “no.” On busy sites, that alone can prevent a minor attack from turning into downtime.

    Features:

    • Firewall Protection: Sucuri’s WAF blocks malware and prevents attacks before they reach your server, significantly reducing the risk of breaches.
    • Malware Cleanup: In the unfortunate event of a malware attack, Sucuri offers professional cleanup services to restore your site quickly.
    • Performance Monitoring: This service also monitors your website’s performance, ensuring that security measures do not impact load times negatively.

    A setup note people miss: if you enable the WAF but don’t force all traffic through it (DNS/proxy correctly + locking down origin access where possible), attackers can still hit your server IP directly. So you think you’re protected… but you aren’t.

    Pricing: Sucuri's plans start from around $199.99 annually, making it a cost-effective solution for many small and medium-sized businesses.

    Why Choose Sucuri? I like Sucuri when the site has real business value and you want a team that can help you dig out of a compromise without guessing. Also, the “less guesswork” part matters when you’re dealing with blacklist warnings and customer trust. You can read more about Sucuri's offerings at Sucuri Security.

    Common mistakes I see with Sucuri:

    • Turning on the WAF and assuming you’re done—while leaving XML-RPC, wp-login, and old endpoints wide open.
    • Not checking for plugin conflicts after enabling rules (especially on custom APIs).
    • Forgetting to set up alerting, then discovering issues days later.

    2. Wordfence Security

    Overview: Wordfence offers a popular free plugin as well as premium options that include advanced features. It provides real-time security monitoring and a firewall designed specifically for WordPress.

    Wordfence is the “default answer” for a lot of WordPress folks because it’s approachable, and the visibility is good. The live traffic view is also a great teaching tool—you can literally watch bots hammer endpoints in real time.

    Features:

    • Malware Scan: Regular scans for malware, backdoors, and vulnerabilities with real-time alerts.
    • Login Security Features: The service includes two-factor authentication and CAPTCHA to protect against brute force attacks.
    • Live Traffic Monitoring: It displays real-time traffic and hack attempts on your site, allowing you to respond quickly.

    Here’s where I’m opinionated: Wordfence is strong for site-level controls (logins, scanning, monitoring). But it’s still running inside WordPress. So if the server is under heavy load, or the site is already compromised at a deeper level, the plugin can become less effective—or you can lose access entirely.

    Pricing: Wordfence’s premium plans start at $99 per year for a single site, which is competitive compared to other services.

    Why Choose Wordfence? If you’re technical enough to tune settings and pay attention to alerts, Wordfence can carry a lot of weight, especially on smaller sites. It’s also a solid stepping stone: start with free, upgrade when the risk or revenue climbs. More information can be found on Wordfence Security.

    My Wordfence “do this first” checklist:

    1. Turn on 2FA for every admin account.
    2. Enable brute-force protection and set sane lockout thresholds.
    3. Configure scan sensitivity (too aggressive can melt cheap hosting).
    4. Set alerts to a monitored inbox (not the site’s own domain if possible).

    3. iThemes Security

    Overview: iThemes Security offers a comprehensive suite of security features designed to protect your WordPress site from the most common threats.

    iThemes has always leaned into “make hardening easier.” That’s valuable because the best security tool is the one you’ll actually keep configured correctly for six months.

    Features:

    • Strong Password Enforcement: It enforces strong passwords for all users to minimize the risk of unauthorized access.
    • File Change Detection: Alerts you to any changes made to your website files, helping you identify potential breaches quickly.
    • User Activity Logging: Keeps track of user activity, further adding a layer of security to your site.

    That file change detection piece is underrated. A lot of compromises don’t scream “malware” at first—they quietly add a new PHP file in an uploads folder, or they modify a theme file by a couple of lines. Getting an alert quickly can save you days.

    Pricing: Starting at around $80 per year, it offers great value for those seeking an effective security solution.

    Why Choose iThemes Security? If you’re running a small business site and you want guardrails without living in security logs, iThemes is a practical pick. More details are available at iThemes Security.

    Where people trip up:

    • Enforcing strong passwords but leaving old admin accounts active.
    • Turning on lots of hardening toggles without testing checkout, forms, and mobile menus.

    4. Jetpack Security

    Overview: While Jetpack is often marketed as an all-in-one plugin for WordPress, its security features are robust and worth mentioning.

    Jetpack is a bit polarizing, but I’ll give it this: on sites where the team already uses Jetpack and wants a simple path to backups + scanning, it’s convenient. Convenience isn’t a dirty word if it keeps you consistent.

    Features:

    • Real-Time Backups: Continually backs up your site, allowing for quick restoration after an incident.
    • Spam Filtering: Effectively filters spam comments and malicious login attempts.
    • Security Scanning: Scans your website for vulnerabilities.

    Backups matter more than most owners think. Not because you’ll definitely get hacked, but because “oops” happens—bad updates, broken themes, accidental deletions. A good backup system is both security and sanity.

    Pricing: Jetpack’s security plans start at $99 annually.

    Why Choose Jetpack? If you want backups and scanning in one place, and you don’t want to stitch together five tools, Jetpack can be a reasonable middle ground. For more on Jetpack, check out Jetpack Security.

    Jetpack gotchas:

    • Owners assume backups mean “safe” and stop updating plugins (that’s how you end up restoring the same vulnerability repeatedly).
    • People don’t test restores. A backup you can’t restore under pressure is just a subscription.

    5. All In One WP Security & Firewall

    Overview: This free plugin provides a comprehensive security solution, focusing on enhancing the security of WordPress sites.

    I’ve used this on early-stage sites where budget is tight and the goal is “stop the dumb stuff.” It does a lot for free, and for some projects that’s the right move.

    Features:

    • User Account Security: Restrict login attempts and implement captcha.
    • File Integrity Monitoring: Monitors the integrity of your WordPress core files to detect unauthorized changes.

    Pricing: This plugin is entirely free, making it an attractive option for budget-conscious site owners.

    Why Choose All In One WP Security? If you’re starting from zero, this can lift your baseline security fast without paying for a premium stack. Learn more at All In One WP Security.

    What I’d watch carefully:

    • Some settings can interfere with caching/minification plugins.
    • “Free” still costs time—if you never review alerts or logs, you’re basically installing it for placebo.

    Understanding WordPress Security Services Vulnerabilities

    If you don’t understand the vulnerabilities you’re trying to cover, you’ll buy the wrong tool and feel oddly safe. Security services vary a lot: some focus on malware cleanup, some on firewalls, some on login protection. Meanwhile, attackers don’t care what you purchased.

    According to research, over 11,334 new vulnerabilities were identified in the WordPress ecosystem in 2025 (Swif). I believe it, because the plugin ecosystem is enormous, and even “good” developers ship bugs under deadline pressure.

    Key vulnerabilities to be aware of include:

    • Outdated Plugins and Themes: Regular updates are essential; failure to do so can expose your site to attacks.
    • Weak Passwords: Many breaches occur due to easily guessable passwords or reused credentials.
    • SQL Injection Attacks: Attackers can exploit unsecured databases if safety measures aren't in place.
    • Cross-Site Scripting (XSS): Malicious scripts can be injected into webpages viewed by other users.

    Here’s the part most articles skip: it’s rarely one issue. It’s usually a chain.

    A real chain I’ve seen (more than once):

    1. A site runs an outdated form plugin.
    2. The plugin has an XSS or file upload weakness.
    3. Attacker drops a webshell into /wp-content/uploads/ with a harmless name.
    4. The shell downloads a second-stage payload that injects spam links sitewide.
    5. Google flags the domain, traffic tanks, and the owner finally notices.

    And then the cleanup goes badly because people delete the obvious malicious file, but miss the hidden persistence.

    Where security services help—and where they don’t

    A security service is strongest when it either blocks the request before WordPress executes it (WAF), or it detects and removes the compromise fast (scanning + cleanup). But there are gaps you should plan for:

    • Plugin supply chain risk: if a plugin update is compromised, you can still get hit. You need staging and change control.
    • Stolen admin sessions: if an attacker steals a cookie/token, brute-force protection won’t matter.
    • Bad hosting isolation: on cheap shared hosting, you can do everything “right” and still inherit neighbor problems.

    That’s why I treat security services as one layer, not the layer.

    Step-by-step: how I map vulnerabilities to controls

    If you want a practical way to choose a service, do this quick mapping exercise. It takes 20 minutes and saves you hours of wandering.

    1. List what matters: admin accounts, customer data, WooCommerce orders, email list, content, uptime.
    2. List your public entry points: wp-login, XML-RPC (if enabled), contact forms, checkout, REST API endpoints.
    3. Count plugins and themes: anything unmaintained is a liability. If it hasn’t been updated in a long time, replace it.
    4. Decide your “blast radius” tolerance: can you handle 1 hour down? 1 day? zero?
    5. Pick controls to match:
      • Brute force → 2FA + rate limiting + bot protection.
      • Vulnerable plugins → patching discipline + scanning + WAF rules.
      • Injection attempts → WAF + input validation (dev-side) + least privilege DB.
      • Account takeover → 2FA + minimal admins + audit logs.

    Then you pick the product that covers the biggest risks for your site, not the internet’s favorite plugin.

    Common mistakes that create vulnerabilities

    These show up constantly in post-breach cleanups:

    • “We’ll update later.” Later becomes never, then a bot finds you.
    • Too many plugins doing the same job. Every plugin is more code and more risk.
    • Leaving old admins active. Former contractors, old agency logins, test accounts—easy wins for attackers.
    • Assuming backups are security. Backups are recovery. You still need prevention.

    Security Monitoring Practices

    Effective security monitoring is essential in not only preventing attacks but also in preparing for rapid response should a breach occur. Here are best practices to include:

    • Regular Backups: Ensure your site is backed up regularly, ideally with an offsite solution to easily recover from attacks.
    • Audit Logs: Keep logs of all changes made to the site to track any unauthorized access or changes.
    • Automated Scanning: Schedule scans frequently to check for malware or vulnerabilities.

    Let me make this operational, because “monitor continuously” is vague when you’re busy.

    A monitoring routine that actually works (without living in dashboards):

    1. Daily (automated):

      • Security alerts to email + optionally Slack.
      • Uptime monitoring (a simple external ping) so you know when the site is down.
    2. Weekly (15 minutes):

      • Review blocked login attempts and top targeted URLs.
      • Check for new users with admin role.
      • Confirm backups ran and you can see restore points.
    3. Monthly (30–60 minutes):

      • Update plugins/themes/core (ideally after testing on staging).
      • Review audit logs for weird patterns (logins from new countries, repeated 404 probes).
      • Remove unused plugins and delete abandoned themes.
    4. Quarterly (1–2 hours):

      • Test a restore to staging. Time it.
      • Rotate passwords for critical accounts.
      • Re-check DNS/WAF settings and make sure origin isn’t exposed.

    One quick mini-story: I once dealt with a site that “had monitoring,” but alerts went to an inbox on the same domain. The attacker compromised mail forwarding rules, so the owner never saw alerts. We fixed the site, but the lesson stuck: send security alerts somewhere independent.

    To summarize, securing your WordPress website in 2026 requires a proactive approach. The security landscape is constantly evolving, and staying informed about the latest tools and practices is essential for success. As Mobeen Abdullah, I've witnessed how effective security measures can ensure business continuity and trust online.

    My Experience With This

    I’ve been in the tech industry for several years and have seen firsthand the devastating impact of security breaches on businesses of all sizes. In my experience, investing in quality WordPress security services is non-negotiable. Not only do these services protect your site, but they also safeguard your reputation and relationship with your users. I've personally utilized several of the services discussed here and appreciate their unique strengths and weaknesses.

    Now the real version, not the motivational poster.

    The ugliest WordPress incidents I’ve handled weren’t “Hollywood hacks.” They were quiet compromises that sat for weeks: a hidden admin user, a backdoor in an old theme file, or a spam injector that only showed up for Googlebot. The site looked fine to the owner, so they kept running ads to it while the domain reputation slowly got torched.

    A real-world example of how this plays out

    One small e-commerce site (not huge—think a few dozen orders a day) called in because checkout started redirecting randomly. Not every time, just enough to cause chargebacks and angry emails.

    What we found, step by step:

    1. Baseline checks: We compared recent plugin/theme updates with when the issue started. No clean correlation.
    2. Log review: A spike in POST requests to a form endpoint showed up, then weird admin-ajax calls.
    3. File integrity scan: A “normal-looking” PHP file appeared inside uploads. That’s almost always wrong.
    4. Persistence hunt: We found a second backdoor in a mu-plugin. That’s the one that would’ve reinfected the site after a naive cleanup.
    5. Response: We cleaned, rotated credentials, forced logouts, and invalidated sessions.
    6. Hardening: 2FA for admins, removed unused plugins, blocked direct access to suspicious paths, and put a WAF in front.

    The owner’s biggest surprise? They already had a security plugin installed. It just wasn’t configured well, alerts weren’t monitored, and nobody had tested restores.

    How I decide what a site needs

    I’m biased toward “boring and reliable” security—fewer moving parts, fewer plugins, clear ownership. So I usually land here:

    • Content site / brochure site: strong login protection + scanning + backups. A free plugin can be fine if updates are disciplined.
    • Business site that captures leads: scanning + hardening + a plan for incident response. WAF starts to make sense.
    • WooCommerce / membership / anything with payments: WAF + paid scanning + tested restores + strict admin control. No exceptions.

    The most common mistakes I see (and what I do instead)

    • Mistake: Treating “installed” as “secured.”

      • Fix: I schedule alerts, test rules, and make sure someone owns the inbox.
    • Mistake: Letting agencies keep admin access forever.

      • Fix: Temporary accounts, least privilege, and a monthly user review.
    • Mistake: Updating live without a rollback plan.

      • Fix: Staging, backups, and a 10-minute restore drill once a quarter.

    If you’re reading this because you’ve already had one scare, don’t just “add another plugin.” Pick a service, configure it properly, and set a routine you can keep.

    FAQ

    What are the best WordPress security practices for 2026?
    The best practices include keeping all plugins and themes updated, using strong passwords, employing two-factor authentication, and regularly backing up your site.

    If you want a tighter checklist (the one I’d hand to a busy owner):

    1. Turn on 2FA for all admins (today, not “soon”).
    2. Delete unused plugins/themes—deactivated isn’t the same as gone.
    3. Put a WAF in front of the site if revenue depends on uptime.
    4. Backups offsite + tested restores (test at least quarterly).
    5. Limit admin accounts and review users monthly.
    6. Update on a schedule (weekly or biweekly), and use staging if the site is complex.

    A lot of people obsess over “hiding wp-admin.” I’d rather you do the boring fundamentals above, because they actually reduce risk.

    How often should I monitor my WordPress site for security threats?
    It's advisable to monitor your site continuously. Automated scanning tools can help to proactively identify and mitigate threats before they escalate.

    Continuous doesn’t mean “stare at graphs.” It means:

    • Alerts must be enabled and delivered somewhere you’ll see them.
    • Uptime monitoring should notify you within a couple minutes.
    • A human should review logs and users at least weekly.

    If you only check security when something feels off, you’re already late.

    Can I rely solely on a security plugin for protection?
    While security plugins are essential, they should be part of a broader security strategy that includes regular updates and good password hygiene.

    I’ll be blunt: plugin-only security is better than nothing, but it has limits.

    • A plugin can’t reliably block traffic before it hits your server.
    • If the site is under heavy load, scans and dashboards can become unusable.
    • If your host is sloppy, you inherit risk you didn’t create.

    So yes, start with a plugin if that’s where you are. But if the site earns money, move toward layered security: WAF + monitoring + backups + disciplined updates. That combo is what keeps you out of panic mode.

  • Understanding Traditional vs Headless WordPress

    Gain a foundational understanding of Traditional vs Headless WordPress, exploring core differences, hosting options, and costs.

    Featured image for Understanding Traditional vs Headless WordPress for Beginners

    Featured image for Understanding Traditional vs Headless WordPress for Beginners

    Understanding Headless WordPress: A Comprehensive Guide

    Headless WordPress means WordPress stops being “the website” and starts being “the content database + admin.” The site visitors see is built somewhere else.

    That one change—decoupling the front-end from the back-end—drives most of the benefits and most of the headaches. So, if you’re a beginner, don’t frame this as “old vs new.” Frame it as “simple all-in-one vs flexible but more complex.”

    Here’s the plain-English comparison I use with clients:

    • Traditional WordPress: WordPress stores content and renders pages using themes (PHP) and plugins.
    • Headless WordPress: WordPress stores content, while a separate front-end (React/Next.js, Vue/Nuxt, etc.) renders pages by calling APIs.

    If you want to move quickly, ship a marketing site, and iterate without a dev on speed dial, traditional is usually the right call. But if you’re building something that behaves like an application (logged-in dashboards, heavy personalization, omnichannel content), headless can start to make sense.

    What Is Headless WordPress Architecture?

    In headless WordPress architecture, you still write and manage content in WordPress. The difference is how that content reaches users.

    Instead of WordPress generating HTML on every page request (via PHP templates), your front-end app pulls content from WordPress using an API—typically the REST API or GraphQL (often via WPGraphQL). Then it renders the UI using whatever you chose: Next.js, Gatsby, Nuxt, or even a native mobile app.

    A practical way to picture it:

    1. Editor publishes a post in WordPress.
    2. WordPress stores it in MySQL like usual.
    3. The front-end requests /wp-json/... (REST) or a GraphQL query.
    4. The front-end renders the page, sometimes ahead of time (static generation), sometimes on request (server-side rendering), sometimes in the browser.

    Because you can use JavaScript frameworks and static site generation, a headless setup can feel dramatically faster than a traditional theme—especially under load. That said, it’s not magic. You’re trading runtime PHP rendering for build steps, caching strategy, and API performance.

    The claim that headless can load in a fraction of the time isn’t pulled out of thin air, but it depends on how you implement it. A well-cached traditional WordPress site can be extremely fast too. Still, the architectural advantage of decoupling is real, and it’s why people keep exploring it (Headless CMS vs WordPress: Which Is Better in 2026?).

    Where headless usually shines:

    • Highly interactive UI: filters, search, dashboards, client portals.
    • Multiple front-ends: website + app + kiosk + in-store screens.
    • Strict performance goals: especially if you’re serving globally and want edge caching.

    Where it often disappoints beginners:

    • Preview workflows: “Why doesn’t preview look like the live page?” (Because WordPress isn’t rendering it.)
    • Plugin assumptions: lots of plugins assume they control the front-end.
    • More DevOps: builds, deploy hooks, environment variables, caching layers.

    Benefits of Headless WordPress

    The biggest benefit is freedom. You can design the front-end without fighting theme limitations, shortcode spaghetti, or page builder markup bloat.

    But freedom isn’t the same as simplicity. So here are the benefits I’ve seen actually matter in real projects:

    1) Omnichannel publishing

    You create content once, then reuse it everywhere. That’s the real “headless superpower.” A product description can show up on the website, in a mobile app, and in an email template—without copying and pasting.

    2) Front-end performance options

    Because the front-end is separate, you can do static generation for marketing pages, edge caching for popular content, and fine-grained control over bundle size. Traditional WordPress can be fast, but you often fight your theme and plugins to get there.

    3) Cleaner separation of concerns

    Editors work in WordPress. Developers work in a front-end repo. That separation can reduce accidental breakage (like an editor dropping a widget that tanks your Core Web Vitals).

    That said, you’ll want to plan the workflow, because otherwise it turns into two disconnected worlds.

    Here’s a step-by-step breakdown I’ve used to keep headless projects sane:

    1. Define content models first. Pages, posts, product, FAQ, landing page sections—whatever you need.
    2. Lock down custom fields. Use ACF or a block strategy, but pick one approach and stick to it.
    3. Choose your API approach. REST is fine for many sites; GraphQL is nice when queries get complex.
    4. Build preview early. If preview isn’t solved, editors will hate the system.
    5. Set caching rules intentionally. Cache API responses, cache rendered pages, and define purge rules.

    Common mistakes I see:

    • Teams build the front-end first, then “figure out the content” later. That’s backwards and expensive.
    • They assume SEO is automatic. It isn’t—you have to implement metadata, canonical tags, sitemaps, structured data, and 301s intentionally.
    • They keep too much logic in WordPress because it’s familiar, then wonder why headless feels messy.

    Headless WordPress Hosting Options

    Hosting is where headless stops being an idea and becomes a monthly bill.

    In a traditional setup, you pay for one hosting environment. It runs WordPress, serves the theme, handles caching (maybe), and you’re done.

    In a headless setup, you usually have two things to host:

    • WordPress back-end: where editors log in and content lives.
    • Front-end app: where users hit pages.

    Many developers put the front-end on platforms like Vercel or Netlify because they’re built for modern deploy workflows and fast delivery. Meanwhile, WordPress can live on managed WordPress hosting, a VPS, or a container platform.

    Here’s the tradeoff I’ve run into:

    • Vercel/Netlify: great DX (developer experience), CI/CD is smooth, global delivery is strong. But costs can jump with build frequency, image optimization, bandwidth, or team seats.
    • Traditional WordPress hosts (Bluehost/SiteGround, etc.): easier for beginners, often cheaper at small scale, and support teams understand WordPress. But you might not get the same app-level performance patterns.

    Also, don’t ignore how content updates trigger deploys. If you statically generate pages, a new post might require a rebuild. That’s fine—until marketing publishes 15 updates during a product launch and your build queue starts stacking up.

    A simple approach that works well for beginners testing headless:

    1. Host WordPress on a managed host you trust.
    2. Deploy a Next.js front-end to Vercel.
    3. Use incremental static regeneration (or a similar pattern) so not every content tweak rebuilds the entire site.
    4. Add a webhook from WordPress to trigger targeted rebuilds.

    If you want a broader view of hosting options (traditional and beyond), this roundup is a decent starting point: 13 Best WordPress Hosting Plans in 2026.

    Examples of Headless CMS in Use

    Headless isn’t just a developer hobby. Big orgs use it because they have multiple channels, multiple teams, and high content volume.

    You’ll see headless patterns in companies like Nike and The New York Times, because they need content to appear in many experiences without rebuilding everything each time. Even when they aren’t using WordPress specifically, the same decoupled thinking applies.

    For headless WordPress-adjacent inspiration, it’s worth looking at brands that operate at “everything is content” scale. Two public examples that show the range of what’s possible:

    • The Walt Disney Company (huge content ecosystem, lots of properties, lots of publishing needs)
    • NASA (massive audience spikes, performance constraints, and broad content distribution)

    Now, a reality check: you don’t need NASA architecture for your local service business site. I’ve seen people copy “enterprise” patterns, then drown in complexity. So, use big brands as proof headless can work—not as a blueprint.

    A mini story from the trenches: I once inherited a project where a team went headless because “React is modern,” but the site was basically five pages and a blog. They spent weeks rebuilding what WordPress themes already did, and then got stuck on preview + redirects during launch. We rolled it back to traditional WordPress, shipped in two days, and their conversion rate went up because we finally focused on content and speed instead of architecture.

    Traditional vs Headless WordPress Costs

    Costs aren’t just “hosting + dev.” The real budget is build + maintain + change over time.

    Traditional WordPress is cheap to start because the basics are free and the path is paved. You can buy a theme, install a few plugins, and go live in a weekend. But as your requirements grow, you can get death-by-a-thousand-add-ons: performance plugins, SEO plugins, form plugins, security plugins, page builder licenses, and then a developer to keep it all from stepping on itself.

    Headless usually flips the curve: higher upfront cost, sometimes lower long-term friction—if your product genuinely benefits from it.

    What you pay for in traditional WordPress

    Typical cost buckets I see in real projects:

    • Hosting: low to moderate monthly cost.
    • Theme/page builder: one-time or yearly licenses.
    • Plugins: security, backups, SEO, forms, caching, translations, etc.
    • Developer time (eventually): fixing conflicts, improving speed, dealing with odd edge cases.

    The hidden cost is plugin sprawl. It’s not even the money—it’s the operational risk. Updates break things. Two plugins fight over caching headers. A “simple” pop-up plugin injects render-blocking scripts site-wide.

    A common mistake: beginners buy a cheap shared host, add 25 plugins, then blame WordPress when the site gets slow. In reality, they’ve built a Jenga tower.

    What you pay for in headless WordPress

    Headless costs more upfront because you’re building a custom front-end application. Even if WordPress stays familiar on the back-end, you’re paying for engineering hours.

    Depending on complexity, initial development often lands between $20,000 to $80,000 (When to Go Headless WordPress: 2026 Honest Decision Guide). I’ve seen it go higher when teams add:

    • design systems
    • localization
    • personalized content
    • advanced search
    • complex deployment environments

    But the bigger ongoing costs tend to be:

    • Two hosting bills: WordPress + front-end platform.
    • CI/CD and builds: more deploys, more tooling.
    • Monitoring and caching: you need visibility into API latency and front-end performance.
    • Developer support: when something breaks, it’s rarely “click one setting.”

    A realistic cost breakdown (example)

    Here’s a simplified example I’ve used when scoping a mid-sized business site (not enterprise, but not tiny):

    Scenario: A content-heavy site with landing pages, a blog, 5–10 custom content types, and a few interactive tools.

    Traditional WordPress approach (roughly):

    1. Theme + child theme customization: 20–40 hours
    2. Core plugins + configuration: 10–20 hours
    3. Performance pass (caching, image pipeline): 5–15 hours
    4. QA + launch: 10–20 hours

    This can be affordable and fast, but you’re constrained by theme architecture and plugin behavior.

    Headless approach (roughly):

    1. Content modeling + editorial workflow: 15–30 hours
    2. API layer decisions (REST/GraphQL), auth rules: 10–25 hours
    3. Front-end build (Next.js pages, templates, components): 80–200 hours
    4. Preview system: 15–40 hours (people underestimate this constantly)
    5. SEO implementation: 10–30 hours
    6. Caching + rebuild strategy + webhooks: 10–30 hours
    7. QA + launch + redirects: 20–40 hours

    Headless can absolutely be worth it. But you only get ROI when that flexibility prevents future rework.

    How to decide without guessing

    If you’re on the fence, I use a quick checklist:

    • If editors need drag-and-drop pages weekly: traditional is usually calmer.
    • If you need content in multiple apps: headless starts to shine.
    • If your site is basically a brochure: headless is probably overkill.
    • If your front-end team already ships React apps: headless can fit naturally.

    One more mistake to avoid: choosing headless because you want “better security.” You can reduce exposure by not serving WordPress publicly, sure. But you’ve also added APIs, tokens, and a separate surface area. Security improves when you design it, not when you change buzzwords.

    Conclusion

    Traditional WordPress is the right default for beginners because it’s cohesive, well-documented, and forgiving. You can get a site live, learn the fundamentals, and iterate without turning every change into a development task.

    Headless WordPress is worth considering when the website stops being “pages” and starts being “a product.” If you need a custom front-end, want content reused across multiple channels, or you’re hitting real performance and scalability limits, then decoupling can unlock options that themes just don’t handle gracefully.

    Here’s the decision path I recommend (and yes, I’ve watched it save budgets):

    Step-by-step: pick your approach

    1. Write down what you’re building. A blog? Marketing site? Store? App dashboard?
    2. List your must-haves for the next 12 months. Not “someday,” but the stuff you’ll actually ship.
    3. Count who will maintain it. One non-technical owner? A marketing team? A dev team?
    4. Decide how often the layout changes. Weekly landing pages scream traditional. A stable design system often fits headless.
    5. Budget for change, not launch. Launch is the easy part. Year-two maintenance is where architecture choices hurt.

    A real-world “beginner” scenario I’ve seen

    A founder came to me with a simple goal: a fast site with a blog and a few landing pages, plus an email capture flow. They’d heard headless was “the future,” so they started a Next.js build.

    Two weeks later, they were blocked on basics: preview wasn’t working, SEO titles weren’t consistent, and every content tweak needed a redeploy. The site wasn’t even live yet.

    We switched them to traditional WordPress with a lightweight theme and strict plugin rules (only what we could justify). They launched in a few days, then revisited headless months later when they actually had a product dashboard and real traffic patterns to optimize.

    That’s the pattern I trust: start traditional unless your requirements demand headless. You can always migrate later when the pain is real and measurable.

    If you’re unsure, do this next: sketch your site features, then circle the ones that feel “app-like” (personalization, heavy interactivity, omnichannel content). If that circle is tiny, ship traditional and move on. If it’s most of the page, headless is worth a serious look—and a serious plan.

  • Top Malware Removal Tools for WordPress 2026

    Explore the best malware removal tools for WordPress in 2026, including free options and essential plugins.

    Featured image for Top Malware Removal Tools for WordPress in 2026

    Featured image for Top Malware Removal Tools for WordPress in 2026

    Top Malware Removal Tools for WordPress in 2026

    When it comes to safeguarding a WordPress site from malware, choosing the right tools is essential. The landscape of malware threats keeps shifting, so the “best” tool depends on what you’re dealing with—an active infection, a prevention setup, or a dev workflow where you want vulnerability visibility.

    I’m opinionated about this: for most site owners, the best tool is the one you’ll actually keep running, keep updated, and understand well enough to react fast. Fancy dashboards don’t help if the cleanup process is confusing or the alerts are noisy.

    That said, here are the top malware removal tools for WordPress in 2026, plus the real-world reasons you’d pick each.

    1. Wordfence: The Leading Choice

    Wordfence is still the default recommendation for a lot of WordPress folks because it covers the basics well: scanning, firewalling, login protection, and visibility into what’s changing on the site.

    Where Wordfence shines is day-to-day defense. You install it, tune a few settings, and you get immediate value—especially if you manage multiple small to mid-sized sites and need a consistent baseline.

    In 2025, Wordfence reported that over 325,000 WordPress sites were infected with malware each day, which is a big, ugly reminder that “it won’t happen to me” is not a strategy. The plugin’s ability to block over 99% of automated attacks is also why I like it for brute-force and bot noise.

    My practical take: Wordfence is great when you want a single plugin to cover the common stuff. But you still need decent hosting, timely updates, and a plan for what happens when the site is already compromised.

    2. MalCare: Intelligent Malware Removal

    Another top contender, MalCare, stands out because it leans hard into fast, guided cleanup. If you’ve ever tried to manually remove malware from a WordPress install (and then discovered a second backdoor 24 hours later), you’ll understand why that matters.

    Unlike a lot of scanners that basically say “good luck,” MalCare pushes you toward removal workflows that don’t require you to be a security engineer. That’s useful when the person responsible is a marketer, a founder, or a busy dev who just needs the site clean now.

    An added advantage is its fast scanning speed; in many cases, it can clean an infected site in under 60 seconds. That speed isn’t just convenience—downtime can wreck SEO, break checkout flows, and tank conversion rates.

    Tradeoff: fast cleanup tools are only as good as your follow-up. If you clean the malware but don’t fix the original entry point (nulled plugin, outdated theme, leaked admin password), you’re going to get reinfected.

    3. Sucuri: A Comprehensive Security Suite

    Sucuri is the “I want a security company in the loop” option. It has a free scanner, but the bigger value is the premium service: firewall, monitoring, and a cleanup process that’s closer to managed response than a DIY plugin.

    If you run a business site where reputation matters—local services, SaaS marketing, ecommerce—Sucuri’s firewall is often the difference between “attack traffic hits me” and “attack traffic dies at the edge.”

    In a recent study, it was found that 60-80% of modern malware threats are missed by traditional security measures. That’s exactly why I like putting a cloud-based firewall in front of sites that can’t afford surprises.

    My caution here: don’t treat a firewall as magic. You still need updates, least-privilege access, and clean admin habits, because attackers love stealing credentials and walking in like they own the place.

    4. CleanTalk: User-Friendly and Effective

    For people who want something simple, CleanTalk keeps things straightforward. It’s commonly thought of as anti-spam first, but it also helps with blocking malicious behavior and reducing the garbage traffic that often comes with brute-force attempts and scripted abuse.

    This matters because noisy sites are hard to secure. If your logs are full of junk, you miss the one request that actually matters. So while CleanTalk isn’t the “deep forensic cleanup” tool on this list, it can lower the overall pressure on your site.

    I’ve seen it work well on community sites and blogs where comment spam and form abuse are constant. Less noise, fewer weird injections, fewer “why is my CPU pegged?” moments.

    5. iThemes Security: Holistic Protection

    iThemes Security focuses on hardening—locking doors, improving visibility, and reducing dumb risks. It’s not only about malware removal; it’s about stopping the easy wins attackers love.

    It includes brute force protection, file change detection, and security logs. Those features don’t sound exciting, but they’re the stuff that actually helps you answer: “What changed, when did it change, and who triggered it?”

    I like iThemes when a site has multiple admins or editors and you need accountability. Meanwhile, if you’re already running another firewall or scanner, make sure features don’t overlap in a way that creates conflicts (double rate-limiting can get weird fast).

    6. WPScan: Evaluating Vulnerabilities

    Finally, WPScan is a developer’s friend. It’s less “click to clean” and more “show me what’s risky in this stack.” It’s especially useful in maintenance workflows, pre-launch checks, and agency environments.

    WPScan’s vulnerability database and scanning approach helps you identify weak points—old plugins, exposed versions, and known issues that you can fix before they turn into a real incident.

    My rule: vulnerability scanning doesn’t replace malware scanning. It complements it. I’ve seen “clean” sites that were one outdated plugin away from being owned, and I’ve also seen “secure” configs that still got infected because credentials were reused.

    Understanding WordPress Malware and Security Risks

    If you want to fight malware, you need a realistic mental model of how WordPress sites get hit. Most infections aren’t movie-style hacking. They’re automation, sloppy credentials, or neglected updates.

    Also, the initial compromise often isn’t the end. Attackers aim for persistence—backdoors, admin users you didn’t create, scheduled tasks that reinfect, or injected code that only triggers for certain user agents.

    Recent statistics indicate a 42% increase in identified vulnerabilities over the past year alone. That’s why “I updated last month” can still be dangerously out of date—especially if you run a stack with 20+ plugins.

    Common Vulnerabilities and Entry Points

    WordPress sites can fall prey to various vulnerabilities, including:

    • Outdated Plugins and Themes: Many hacks originate from plugins or themes that have not been updated. Attackers scan the internet for known vulnerable versions, so once an exploit is public, it’s basically a race.
    • Weak Passwords: A significant number of hacks start with bad passwords or reused credentials. So even if the code is perfect, a leaked password from some other service can sink you.
    • Configuration Gaps: Default settings can leave sites exposed. For example, overly permissive file permissions or too many admin accounts tend to come back to bite.

    One mistake I see constantly: people “secure WordPress” but skip the hosting layer. If your server is outdated, or your file ownership is wrong, or you’re letting anyone write to plugin directories, malware removal becomes a loop.

    The Evolution of Malware Threats

    The landscape for WordPress malware is evolving quickly. Attackers are now using AI-generated code and more evasive techniques—stuff that blends in, hides in must-use plugins, or piggybacks on legitimate files.

    For instance, a recent study found that AI-generated malware can mimic legitimate code so well that it often goes undetected by standard security plugins. In practice, that means signature-only scanning is less reliable than it used to be.

    So what works? Layering. You want scanning, a firewall (plugin or edge), strong auth, plus basic hygiene like updates and backups. It’s not glamorous, but it’s what holds up.

    Statistics and Trends for 2026

    As we progress into 2026, a few trends show up repeatedly:

    • Increased Attack Frequency: Attacks are more frequent and more targeted, so “set it and forget it” security doesn’t hold.
    • Rising Malware Complexity: Malware is more complex—backdoors, delayed execution, conditional redirects, and reinfection mechanisms.
    • Growing Importance of Security Plugins: Given the rise in threats, reliable security plugins are now essential for every WordPress website.

    Because of those trends, I recommend integrating regular security audits into your maintenance routine. A performance-focused audit can still reveal security red flags (weird PHP execution, strange cron jobs, unexpected outbound requests), and the process in this guide on uncovering hidden performance issues maps nicely to real security triage.

    My Experience With This

    I’m Mobeen Abdullah, and as the founder of Revnix, I spend a lot of time in the intersection of cloud-native platforms and security. That’s a fancy way of saying I’ve seen what happens when a WordPress site gets infected on a Friday night and nobody has a clean rollback.

    Here’s a real pattern I’ve dealt with more than once: a site owner notices a ranking drop first, not malware. Search Console starts throwing “This site may be hacked” warnings, paid ads get disapproved, and revenue gets weirdly soft. When we look, the homepage is fine—until you visit from a mobile user-agent, or you land on a long-tail blog URL. Then you get redirected to a spam domain. That’s not random. Attackers do it on purpose because it delays detection.

    When I’m cleaning a hacked WordPress site, I follow a boring checklist. Boring is good.

    How I actually approach a cleanup

    1. Put the site in a safe state. I’ll temporarily restrict access (maintenance mode, basic auth, or a WAF “under attack” style mode) so the infection doesn’t keep spreading while I’m working.

    2. Take a snapshot backup anyway. Even if the site is infected, I archive the current state. That’s how I compare files later and figure out what changed. It’s also how I prove what happened if a client asks.

    3. Scan with at least two angles. I’ll use a plugin scanner (Wordfence/MalCare style) and then I’ll sanity-check the filesystem and database. Why? Because I’ve seen clean scans miss a malicious mu-plugin, and I’ve seen database injections hide in options tables.

    4. Remove the malware—and the persistence. Cleaning visible payloads is easy. The hard part is finding the reinfection path: rogue admin users, injected cron events, backdoored plugins, or writable directories that shouldn’t be writable.

    5. Patch the entry point. If the infection came from an outdated plugin, you update or replace it. If it came from stolen credentials, you rotate passwords, force logout sessions, and tighten roles.

    6. Harden and monitor. This is where tools like Sucuri firewall, Wordfence rules, iThemes hardening, and WPScan checks become the ongoing guardrails instead of a one-time cleanup.

    Common mistakes I see (and why they hurt)

    • Only deleting “suspicious” files. Attackers love naming files like normal WordPress files. If you delete one wp-vcd.php but miss the injected code in functions.php, you’ll be back here tomorrow.

    • Restoring a backup without fixing the vulnerability. A restore is not a fix. If the vulnerable plugin stays, the attacker just walks back in.

    • Keeping too many admins. Every extra admin is another set of credentials that can leak. Reduce it. Then document who owns what.

    • Ignoring hosting-level signals. If your host is logging outbound spam, or your CPU spikes at odd hours, don’t shrug. Those are often the first breadcrumbs.

    A quick persona story (because this is common)

    One client—a small ecommerce shop—installed a “free premium theme” from a random site. It worked great for two weeks. Then checkout started failing intermittently, and their customers got redirected to a sketchy pharmacy page on mobile.

    We cleaned it, but the real fix was replacing the theme, rotating every credential (WP admin, hosting panel, database, SFTP), and putting a firewall in front. After that, we added a monthly WPScan-style vulnerability review and a weekly file change report. The site stayed stable because the process stayed boring.

    If you take one thing from my experience: malware removal isn’t a plugin you install once. It’s a loop—detect, clean, patch, harden, monitor. The tools make the loop faster, but you still have to run it.

    Conclusion

    As we move through 2026, the security of WordPress sites remains a daily operational concern, not a once-a-year project. Effective malware removal tools, paired with proactive habits, will reduce the risk from increasingly evasive malware.

    If you want to keep the site fast while staying secure, start tightening your maintenance routine. For performance and stability work that pairs nicely with security, read maximizing efficiency with WordPress and fold those checks into your monthly schedule.

    Also, if you’re exploring architecture changes, headless WordPress can reduce some attack surface and improve performance—although it introduces its own complexity. Either way, pick your tools, set a cadence, and don’t wait for the next infection to take security seriously.

  • Top Headless CMS for Next.js Projects in 2026

    Discover the best headless CMS choices for Next.js projects in 2026. Compare features, pricing, and integrations to find your ideal CMS.

    Featured image for Top Headless CMS Choices for Next.js Projects in 2026

    Featured image for Top Headless CMS Choices for Next.js Projects in 2026

    Top Headless CMS Choices for Next.js Projects in 2026

    Understanding Headless CMS and Their Importance for Next.js

    A headless CMS separates the back end (content management) from the front end (presentation). In practice, that means your editors work in a content studio (web UI), and your Next.js app pulls content over an API (REST/GraphQL or a query language like GROQ). The CMS doesn’t “render pages” — Next.js does.

    That separation is the whole point, but it’s also where teams get tripped up.

    What this looks like in a real Next.js build

    Here’s the clean, boring flow I aim for on most projects:

    1. Model content intentionally (not “whatever fields feel right today”).

      • Define types like Page, BlogPost, Author, Category, Product.
      • Decide which fields are required, which are optional, and what can be reused.
    2. Fetch content server-side in the right place.

      • For SSG/ISR, you fetch at build time or revalidate on an interval.
      • For SSR, you fetch on request (and you need to care about latency and caching).
    3. Render through components that match the content model.

      • A “hero” component shouldn’t accept 12 random props because your CMS is messy.
      • Your CMS should produce structured data that maps cleanly to your design system.
    4. Preview is a first-class feature, not an afterthought.

      • Editors need to see draft content rendered through the real Next.js templates.
      • Developers need preview routes that don’t require tribal knowledge.
    5. Publishing triggers revalidation/build reliably.

      • If you’re using ISR, publishing should invalidate the right pages.
      • If you’re doing full static builds, publishing should kick a deployment.

    When teams skip steps 1 and 4, they pay for it later. Not in dramatic ways — in death-by-a-thousand-cuts ways.

    A real example: the “everything is a Rich Text field” mistake

    A while back I inherited a Next.js marketing site where the CMS model was basically:

    • title (string)
    • body (rich text)
    • seo (optional)

    That sounds flexible… until you try to build anything more complex than a blog post. The marketing team wanted landing pages with comparison tables, testimonial sliders, and feature grids.

    So what happened?

    • Developers started parsing rich text blocks and adding secret “markers” like [[FEATURE_GRID]] inside the body.
    • Editors started copy/pasting those markers without understanding them.
    • Preview never matched production because the parsing logic differed between environments.
    • Every new layout request turned into custom one-off code.

    A headless CMS should reduce coupling, but sloppy content modeling increases it. You end up coupling the site to editorial quirks instead of to a stable schema.

    Why Next.js makes headless CMS more valuable (and more annoying)

    Next.js gives you a lot of rendering modes. That’s good. It also means your CMS choice needs to play nicely with:

    • SSR when content must be fresh on every request (think dashboards, pricing experiments, logged-in experiences).
    • SSG when content changes less often and you want max speed (docs, marketing pages).
    • ISR when you want “mostly static” but still publish without rebuilding the universe.
    • Preview when drafts matter (they always do, once you have editors).

    A headless CMS is especially helpful here because it doesn’t fight your rendering decisions. It just supplies structured content.

    Step-by-step: how I evaluate headless CMS fit for Next.js

    If you’re a dev lead or technical PM, here’s the checklist I actually use before committing:

    1. Can we model content without hacks?

      • Reusable blocks? Relationships? Validation? Versioning?
    2. How does preview work, exactly?

      • Does it support draft content securely?
      • Can editors preview a specific route (including dynamic routes)?
    3. What’s the API ergonomics?

      • Query language pleasant or painful?
      • Filtering, pagination, localization — does it feel clean?
    4. Auth and roles

      • Can marketing publish without engineering permissions?
      • Can contractors get limited access?
    5. Operational reality

      • If self-hosted: who patches it, monitors it, backs it up?
      • If SaaS: what happens when the API slows down or billing changes?

    Common mistakes I see (and how to avoid them)

    • Mistake: choosing a CMS purely for the editor UI.
      Great UI doesn’t save you from a weak content model or painful preview integration. I’ve watched teams pick a CMS because “marketing likes it,” then spend months building custom tooling around it.

    • Mistake: treating content types like page templates.
      You want structured content with composable blocks, not 40 “page types” that hardcode layout decisions.

    • Mistake: ignoring caching and revalidation.
      If you do SSR and your CMS API is slow, your site becomes slow. If you do ISR and never wire revalidation, content won’t update when it should.

    • Mistake: not planning for localization early.
      Retrofitting i18n into a messy schema is brutal. If there’s even a 20% chance you’ll go multilingual, model for it now.

    That’s why headless CMS matters for Next.js: it’s not just “where content lives.” It’s a dependency that affects delivery speed, editor happiness, and how many weird edge cases you’ll be debugging later.

    Top Headless CMS Choices for Next.js Projects in 2026

    When I’m picking a headless CMS for a Next.js build, I’m looking at four things first: (1) content modeling, (2) preview, (3) API + performance, and (4) operational burden. Everything else is secondary.

    1. Sanity

    Sanity is still one of the most flexible choices when you need structured content that doesn’t box you in. I like it most when the site has lots of “content that isn’t just pages” — complex relationships, reusable modules, and editorial workflows where people collaborate in real time.

    • Key Features:

      • Real-time editing and collaboration tools.
      • Powerful API for easy integration.
      • Rich text editing with customizable schemas.
    • Use Case: Perfect for content-heavy applications requiring precision and flexibility.

    Sanity’s ecosystem around Next.js is mature, and the official integration via next-sanity reduces the “glue code” you’d otherwise write. If you want an overview of how it fits into a Next.js stack, this breakdown is a decent starting point: More details can be found here.

    Tradeoff I’ve hit in the real world: Sanity’s flexibility can encourage teams to over-engineer schemas. Keep your first version small, add validation rules early, and don’t let “we can model anything” turn into “we modeled everything three different ways.”

    2. Payload CMS

    Payload is what I reach for when the team is TypeScript-heavy and wants the CMS to feel like part of the codebase, not a separate universe. Its code-first configuration is the selling point: you define collections and fields programmatically, which can be a huge relief if you’ve been burned by clickops schema builders.

    • Key Features:

      • Full control over the backend with customizable APIs (REST, GraphQL).
      • Live previews to enhance the editing experience.
      • Built directly into the Next.js environment, simplifying deployment processes.
    • Use Case: Ideal for developer-led projects that require extensive customization and scalability.

    Tradeoff: you’re accepting more engineering ownership. That’s fine if you have the team for it. If your company treats infra work like a tax nobody pays, a SaaS CMS might be the healthier choice.

    3. Strapi

    Strapi is still the go-to open-source option when you want control, self-hosting, and a big ecosystem. It’s rarely my “fastest to ship” pick, but it’s often my “we won’t regret this later” pick when data ownership and extensibility matter.

    • Key Features:

      • Flexible API generation (REST and GraphQL).
      • Extensive plugin ecosystem for additional features.
      • Community-driven support and documentation.
    • Use Case: Great for startups and developers looking for an easy-to-use system without recurring costs associated with SaaS solutions.

    If you’re integrating Strapi with Next.js in 2026 specifically (app router patterns, previews, auth boundaries), this guide covers a lot of the practical stuff teams trip over: Learn more.

    Tradeoff: self-hosted means you own upgrades, security patches, backups, and performance tuning. People underestimate that. If you don’t have a real owner for “keep the CMS alive,” you’ll feel it later.

    4. Contentful

    Contentful is still a common enterprise choice because it’s stable, well-supported, and built for larger organizations with governance needs. When I’m working with teams that have multiple brands, multiple locales, and strict publishing workflows, it’s often on the shortlist.

    • Key Features:

      • Strong capabilities for localization and internationalization.
      • Detailed content governance tools for editorial teams.
      • Reliable performance suited for high-traffic sites.
    • Use Case: Best suited for enterprises that need a robust solution with strict governance protocols and complex workflows.

    Tradeoff: you’re paying for maturity and guardrails. That’s not a bad thing — just don’t pick it for a tiny site where you’ll never use the governance features.

    5. Prismic

    Prismic earns its spot when marketing teams want visual editing and developers still want control over how content turns into pages. Slice-based modeling can be a sweet spot: editors assemble pages from approved “slices,” and devs maintain the slice components.

    • Key Features:

      • Visual editor for marketing-focused teams.
      • Document versioning and integration with popular frameworks.
      • Efficient content modeling and slicing strategies.
    • Use Case: Perfect for marketing teams that require a blend of developer support and content flexibility.

    Tradeoff: slice sprawl is real. If you create a new slice for every slightly different layout, you’ll end up with 60 slices that nobody wants to touch. Establish design constraints early.

    Evaluating Open Source Headless CMS for Next.js Development

    When you’re looking at open-source options like Strapi and Payload, the pitch is obvious: no per-seat SaaS pricing and full control. The hidden cost is also obvious (once you’ve lived it): you become the platform team.

    Here’s how I evaluate open-source CMS choices specifically for Next.js work:

    1. Community Support

      • Is the community active this year, not just historically?
      • Are plugins maintained, or are you going to fork everything?
    2. Customization

      • Can you extend auth, add fields, and build custom endpoints without fighting the framework?
      • How painful is it to keep customizations across upgrades?
    3. Performance

      • Test realistic content sizes, not toy datasets.
      • If you’re doing SSR in Next.js, measure API latency early. Don’t guess.
    4. Security

      • How are roles handled?
      • What’s the story for upgrades, dependency scanning, and patch cadence?

    One more thing I’ll add from experience: if you self-host, write down your “day 2” plan before you ship day 1. Who gets paged when the CMS falls over? Where do backups live? What’s your upgrade window? If nobody owns those answers, you don’t actually have a plan.

    In the end, the right headless CMS for your Next.js projects in 2026 depends on your team shape more than your tech taste. If you need maximum flexibility and structured content, I lean Sanity. If you want code-first control and TypeScript alignment, Payload is compelling. If you need open-source with a big ecosystem, Strapi is a safe bet. If governance and scale are the priority, Contentful is hard to argue with. If marketing needs visual building blocks without giving up developer control, Prismic fits.

    And if you’re exploring newer “visual + code” approaches, tools like Nextly are worth a look — especially when you want a builder feel without abandoning a real Next.js codebase.

    Next step: pick two CMSs, model one real page (not a demo page), wire preview, and time-box it to a day. The one that feels boring and predictable at the end of that day is usually your winner.

    FAQ:

    • What is a headless CMS?
      A headless CMS is a content management system that allows users to manage content without being tied to a specific front-end presentation layer. It communicates via APIs, providing flexibility for developers to use various frontend technologies like Next.js.

    • Why should I use a headless CMS with Next.js?
      Combining a headless CMS with Next.js offers developers a lot of flexibility in building fast, modern web applications while allowing content editors to manage their content easily.

    • What factors should I consider when choosing a headless CMS?
      Consider scalability, ease of integration with Next.js, customization abilities, and whether you prefer a cloud-based or self-hosted solution.

    • Can a headless CMS improve my site's performance?
      Yes, because headless CMS supports static site generation and server-side rendering, which can significantly improve load times and overall performance of your website.

    • Are there free headless CMS options available?
      Yes, platforms like Strapi and Payload offer open-source solutions that allow you to host your CMS without associated monthly fees, although you may incur costs for hosting and maintenance.

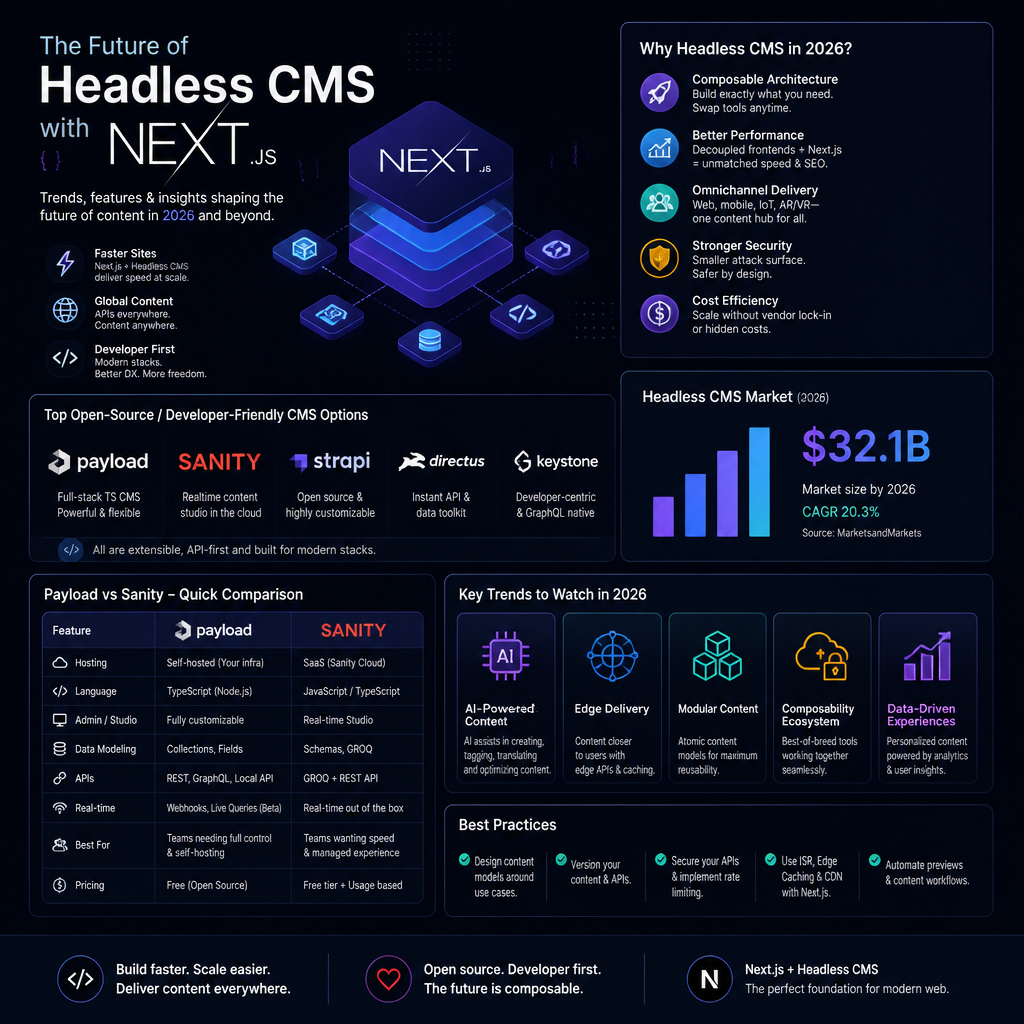
  • Headless CMS Next.js Insights for 2026

    Discover the future of headless CMS with Next.js in 2026. Explore the best platforms and best practices for developers and business decision-makers.

    Featured image for The Future of Headless CMS with Next.js: Insights for 2026

    Featured image for The Future of Headless CMS with Next.js: Insights for 2026

    Open Source Headless CMS for Next.js

    Open source headless CMS for Next.js is appealing for a simple reason: you can get escape velocity without signing your architecture away. You own the data model, you can run it locally, and if pricing or product direction changes, you’re not stuck rewriting your content layer under pressure.

    That said, open source isn’t “free.” You pay in ops, upgrades, and the occasional Saturday debugging an auth callback. The win is control.

    Two platforms that come up constantly in real Next.js builds are Payload and Strapi.

    Payload CMS

    Payload CMS is the open-source headless CMS I reach for when the team is code-heavy and wants the CMS to feel like part of the app—not a separate universe. It’s TypeScript-friendly, it’s deeply customizable, and it behaves well in a Next.js/Node ecosystem.

    A detail that matters more than people think: Payload encourages a code-first workflow. That makes it easier to do the stuff you’ll inevitably need later—custom access rules, hooks, versioning workflows, and content relationships that aren’t just “title + rich text.”

    According to a recent Techsy article, Payload is rated as the top choice for Next.js developers due to its seamless integration and powerful API capabilities. As of 2026, Payload allows for both local API development and cloud hosting options, making it incredibly versatile for various use cases.

    Here’s a step-by-step approach I’ve used to keep a Payload + Next.js project sane:

    1. Model content around pages, not fields. Start with the routes your Next.js app needs (e.g., /blog/[slug], /docs/[...path]) and build collections to match. If you start with “fields marketing asked for,” you’ll end up with a content model that doesn’t map cleanly to rendering.
    2. Add a “status” field early (draft/review/published) and treat it as a first-class filter in queries. People always bolt this on later, and it hurts.
    3. Plan preview from day one. Preview is where headless projects go to die. Decide how drafts should be fetched, who can see them, and how tokens/cookies will work across environments.
    4. Separate “authoring images” from “delivery images.” Editors upload huge images. Your Next.js layer needs responsive versions, caching headers, and predictable URLs. Decide whether Payload handles transformations or whether you offload to an image CDN.

    A real example: I helped on a Next.js product marketing site where the team initially treated Payload like “WordPress but headless.” Every page became a single giant document with dozens of optional fields. Two months later, every new landing page request required a dev to add yet another conditional block.

    We fixed it by shifting to modular blocks (hero, testimonial grid, pricing table, FAQ), locking down each block’s schema, and giving editors building blocks instead of a free-for-all. Net result: fewer regressions, faster content launches, and the marketing team stopped DM’ing engineers at 5pm on Fridays.

    Common mistakes I see with Payload specifically:

    • Over-customizing the admin UI immediately. Teams spend week one making the admin “pretty,” then discover they never implemented proper access control.
    • Not pinning versions and migration strategy. You need a predictable upgrade cadence. If you don’t plan it, you’ll end up upgrading during an incident.
    • Ignoring seed data. Without realistic seed content, your Next.js UI looks fine in Storybook but collapses when real editors enter real-world content.

    Strapi

    Strapi is usually the open-source pick when a team wants open source benefits but needs a more “CMS-like” editorial experience out of the box. It’s approachable for content managers, and it doesn’t demand that everyone on the team thinks in TypeScript types.

    It also hits the baseline integration needs: Strapi supports REST and GraphQL APIs, providing flexibility in how data can be consumed.

    Where Strapi tends to fit best in Next.js projects:

    • Multi-language sites where editors need a familiar interface.
    • Teams with a mix of skills—some dev-heavy, some content-heavy.
    • Projects where you want the CMS to feel like a product your company “runs,” not a library you “embed.”

    A practical Next.js integration path I’ve used:

    1. Pick REST or GraphQL and commit. You can support both, but you’ll double your testing and docs burden.
    2. Define a small set of API clients (one per content area), not one mega-client.
    3. Add caching at the edge or in Next.js fetch where it actually helps. Don’t cache everything blindly; cache “slow to change” content like navigation and footer, and handle “fast to change” content (like breaking announcements) with shorter TTLs or on-demand revalidation.

    Common Strapi mistakes:

    • Permissions misconfigurations. People open up public roles too broadly during development and forget to lock them down.
    • Treating content types like database tables. Editors don’t think in joins. If they can’t find content quickly, they’ll create duplicates.

    Future trends in open source CMS

    Looking at trends for 2026, the demand for next.js CMS open source solutions is expected to rise. The driver isn’t ideology—it’s procurement and risk management. Companies are tired of vendor lock-in and pricing shifts that turn a “reasonable CMS bill” into a line item that gets scrutinized every quarter.

    Also, Next.js teams increasingly want their CMS to be:

    • Composable (plugs into auth, search, analytics without fighting you)
    • Preview-friendly (draft content that renders in real UI)
    • Deployable anywhere (local, VM, container, managed)

    As highlighted by community discussions on platforms like Reddit, many developers are transitioning to open-source systems to capitalize on community-driven updates and improvements.

    The tradeoff I’ll say out loud: open source is awesome until your org can’t staff it. If you don’t have someone who can own upgrades, backups, and security patching, SaaS can be the cheaper option—even if the sticker price looks higher.

    Best Headless CMS for Next.js in 2026

    Best headless CMS for Next.js in 2026 doesn’t mean “best on a grid.” It means best for your constraints: editorial workflow, preview needs, performance targets, governance, and how much platform work you’re willing to own.

    When teams ask me for a recommendation, I ask three questions first:

    1. Do you need real-time collaboration and a content studio that editors love?
    2. Do you need enterprise governance (roles, environments, approvals, audit trails)?
    3. Are you optimizing for developer speed (ship features weekly) or organizational safety (ship carefully, with guardrails)?

    With that lens, here are the platforms that show up as leaders.

    Sanity CMS

    Sanity is the CMS I’ve seen win when teams care about a strong editing experience and developers want a content layer that’s flexible without being chaotic.

    It’s particularly recognized for its real-time collaboration features and a powerful query language that allows for intricate data models. As stated in the Sanity Next.js guide, this CMS is ideal for teams looking to build applications that require both speed and flexibility. Its emphasis on developer experience makes it a go-to for many Next.js projects.

    A concrete way Sanity tends to play out in Next.js builds:

    • You model content with enough structure that it’s queryable, but you’re not stuck with rigid “page templates.”
    • You build a preview setup so editors can see drafts in the actual Next.js front end.
    • You lean on Sanity’s strengths for structured content: complex relationships, references, and custom editorial tooling.

    Persona anecdote: I worked with a small product team (2 devs, 1 designer, 2 marketers) shipping a docs + blog + product pages setup. They started with a simpler CMS, but docs became a mess—duplicate pages, inconsistent metadata, and no one trusted the “published” state.

    We moved them to Sanity, but the real fix wasn’t the migration itself. The fix was designing the schema around how they work:

    • Docs pages had required fields (title, slug, sidebar section, last reviewed date).
    • Blog posts had a separate workflow (author, canonical URL rules, related products).
    • Product pages had structured sections with validation (no empty CTAs, no missing OG image).

    Once validations were in place, the “random broken pages” basically stopped. How I know: before the switch, we’d patch content-caused UI issues every sprint. Afterward, it was closer to once a month.

    Common mistakes with Sanity:

    • Overusing free-form rich text when the content should be structured. Your future self will hate you when you need to render “feature tables” consistently.
    • Not defining canonical patterns for slugs and references. Editors will invent their own taxonomy if you don’t give them one.
    • Skipping a query review. GROQ is powerful; it’s also easy to write overly broad queries that pull half your dataset for a page.

    Contentful

    Contentful stays relevant in 2026 because big orgs often want someone else to own the platform layer. You’re buying predictable uptime, enterprise controls, and a lot of “boring but necessary” features.

    While primarily a SaaS solution, Contentful remains a viable option for enterprises needing comprehensive content management and governance features. It excels in environments where multiple teams need to collaborate efficiently. Its RESTful APIs integrate seamlessly with Next.js applications, providing a smooth user experience across various content types.

    Where Contentful tends to be the right answer:

    • Multiple teams publishing across brands/regions.
    • A need for stricter permissions, environments, and approvals.
    • Less appetite for self-hosting and maintaining a CMS.

    The tradeoff: you’ll often spend more time designing your content model up front, and migrations can be more formal. In exchange, you get guardrails that matter when 50 people can publish.

    Prismic

    Prismic is a strong choice when you want editors moving fast and you like the “slices” mental model.

    Another contender is Prismic, which is favored for its user-friendly interface and features like the Slice Machine that enables reusable components. Teams requiring a rapid development cycle often prefer Prismic as it allows for quick iterations without sacrificing content quality. Prismic’s blog notes that its visual editing tools make it easier for non-technical users to manage content without developer intervention.

    A practical way I’ve seen Prismic succeed with Next.js:

    1. Define 10–20 slices that cover 90% of marketing needs (hero, logo wall, pricing, CTA band, FAQ, comparison table).
    2. For anything outside that set, don’t immediately add a new slice. First ask: is this a one-off campaign that can be handled by a variant of an existing slice?
    3. Add content guidelines inside the slice fields (character limits, image ratios, “don’t use all caps” notes). Editors actually read them when it’s in the UI.

    Common mistake: teams create slices for every single page, turning slices into “page templates with extra steps.” You want a limited set of reusable blocks, not a museum of one-offs.

    Headless CMS Best Practices with Next.js

    Headless CMS best practices with Next.js are mostly about avoiding self-inflicted pain: build times, preview confusion, accidental content leaks, and slow pages because you’re fetching too much.

    Efficient data fetching

    Next.js gives you multiple rendering modes, and the “right” one is usually mixed.

    Utilizing Next.js's mixed rendering capabilities—Static Site Generation (SSG), Server-Side Rendering (SSR), and Incremental Static Regeneration (ISR)—allows developers to optimize how they fetch and serve content. For instance, using ISR can keep content fresh without needing full site rebuilds, which is essential for content-heavy applications. Developers integrating Payload CMS can leverage this effectively to automate static page revalidation (DEV Community).

    What I do in practice:

    • SSG/ISR for marketing and docs where performance matters and content changes are predictable.
    • SSR for highly personalized pages (dashboards, account pages), or where auth is involved.
    • Client-side fetching sparingly, mostly for interactive widgets where SEO isn’t the point.

    A step-by-step pattern for content-heavy sites:

    1. Use ISR for most content pages.
    2. Set revalidation based on business reality (e.g., docs revalidate every hour, marketing pages every 5 minutes during campaign weeks, otherwise every few hours).
    3. Add on-demand revalidation for “publish now” moments. Editors hate waiting for a timer.
    4. Cache global data (navigation, footer, site settings). Don’t refetch it 200 times per build.

    Common mistakes:

    • Rebuilding the whole site on every publish. This is the classic headless anti-pattern. It works until it doesn’t.
    • Overfetching in page queries. If you only need title/slug/excerpt for a listing page, don’t pull full rich text and assets.

    Content modeling

    Proper content modeling is crucial for a headless CMS. Taking advantage of these platforms’ schema-driven content modeling capabilities can significantly streamline the development of complex applications.

    My stance: content modeling is a product decision, not just a CMS setup task. If you get it wrong, you’ll feel it in every release.

    A concrete workflow that tends to work:

    • Start with three tiers of content: global settings, page-level documents, reusable modules.
    • Decide what must be structured (pricing, specs, CTAs, FAQs) vs what can be rich text.
    • Add validation rules early: required metadata, max lengths, allowed formats.

    A mistake I’ve seen more than once: someone puts SEO fields (title/description/OG image) on some content types but not others. Six months later you’re debugging why certain pages share the wrong OG image on social.

    Optimization for SEO

    SEO remains a cornerstone of web visibility, and headless setups can either help or hurt depending on how disciplined you are.

    This includes ensuring that all content is indexed correctly and leveraging Next.js features for generating sitemaps, metadata, and other SEO-friendly elements. The chosen CMS should support easy management of SEO attributes directly in the content editor.

    What I’d do for a 2026 Next.js + headless build:

    • Ensure every indexable page has: canonical URL, OG title/description/image, robots directives when needed.
    • Store SEO fields in the CMS, but enforce guardrails (lengths, required OG image for key templates).
    • Make redirects a first-class feature (editors will change slugs). Don’t rely on engineers to hardcode redirects for content updates.

    Common mistake: teams ship headless without a redirect workflow. Then a marketer renames a slug, and you quietly bleed SEO until someone notices in analytics.

    Performance monitoring

    Finally, monitor performance metrics continually. It’s the only way to know if your CMS choices are helping or hurting.

    Utilizing tools like Google Lighthouse or custom analytics dashboards can help track how the headless CMS impacts page load times and user engagement.

    My practical checklist:

    • Run Lighthouse in CI for a few key pages (home, top landing page, top blog post). Watch it over time.
    • Track build times and revalidation times. If your builds creep from 4 minutes to 25, something’s off.
    • Watch your largest content payloads (giant rich text blobs, unoptimized images, huge navigation trees).

    A small war story: on a docs site, performance tanked after “just adding a sidebar.” Turns out the sidebar query pulled the full document for every page in the tree—including markdown bodies and image arrays. Fix was simple: query only IDs, titles, and slugs for navigation. But without monitoring, it looked like “Next.js got slow.” It didn’t. We did.

    In conclusion, the future of headless CMS with Next.js looks promising as developers and organizations seek more flexibility and control over their content delivery systems. The choice of the right CMS can greatly affect project outcomes, making it essential to evaluate based on your specific requirements and objectives. As we move into 2026, platforms like Payload, Sanity, and Strapi are paving the way, offering innovative features that cater to both developers and marketers alike.

  • Top Email Marketing Services for 2026

    Explore the best email marketing services to watch in 2026, including trends, tools, and automation strategies for success.

    Featured image for Top Email Marketing Services to Watch in 2026

    Featured image for Top Email Marketing Services to Watch in 2026

    Understanding the Email Marketing Landscape in 2026

    Email marketing in 2026 is getting squeezed from both sides: people expect personalization like it’s table stakes, and mailbox providers are less tolerant of noisy, generic sending. At the same time, the tools are better than ever—AI-assisted writing, predictive segmentation, smarter send-time optimization, deeper ecommerce events, and automation builders that don’t require a developer.

    But here’s the uncomfortable truth I’ve seen while QA’ing campaigns: most email programs don’t fail because the tool is “missing features.” They fail because the data is messy, the logic is vague, and nobody is watching the post-send reality (bounces, complaints, unsubscribes, deliverability drift, and broken dynamic blocks).

    In 2026, the winners are the teams who treat email like a product:

    • They instrument it (events, UTMs, revenue attribution)
    • They test it (rendering, segmentation logic, edge cases)
    • They iterate weekly (not quarterly)
    • They keep lists clean and permissions clear

    If you do that, the platform matters—but it matters less than you think. If you don’t do that, the platform matters more than you want.

    The importance of personalization

    Personalization is key, but not in the cheesy “Hi {first_name}” way.

    What works in 2026 is behavioral relevance:

    • Someone viewed a product twice but didn’t add to cart
    • Someone bought, then browsed accessories
    • Someone hasn’t opened in 60 days but still visits the site
    • Someone’s on a renewal cycle (subscriptions, memberships)

    According to a recent report, brands that implement personalized email marketing strategies experience up to 26% higher open rates and improved customer retention. That aligns with what I’ve seen in practice: when we narrowed segments from “All subscribers” to “Clicked in last 30 days + browsed category X,” open rate and click rate didn’t just inch up—they jumped enough that it changed paid spend decisions.

    A real example (small ecommerce):

    I helped QA an email program for a small apparel shop that was blasting the same promo to everyone twice a week. We split the list into three buckets:

    1. Warm: opened or clicked in last 30 days
    2. Lukewarm: last engagement 31–90 days
    3. Cold: no engagement 90+ days

    Then we changed only two things:

    • Warm got the normal promos
    • Lukewarm got “best sellers + social proof” with a lighter discount
    • Cold got a re-permission campaign (and we stopped mailing them if they didn’t respond)

    Result: overall list size shrank a bit, but revenue per recipient went up, and deliverability stabilized. That tradeoff—mail fewer people, make more money—still makes some teams nervous, but it’s often the right move.

    Common personalization mistake I keep seeing:

    Teams “personalize” with too many segments before they’ve validated tracking. If your events are wrong (double-fired add-to-cart, missing purchase events, incorrect currency), your personalization becomes confident nonsense. I’d rather ship three trustworthy segments than fifteen fragile ones.

    Why automation is a game changer

    Automation is the difference between email being a recurring task and being a system that sells while you sleep (yes, it’s a cliché—still true).

    In 2026, automated flows typically outperform campaigns because:

    • They’re timed to user intent (welcome, browse, cart, post-purchase)
    • They run continuously
    • They can be improved in small increments

    My baseline automation stack (what I implement first):

    1. Welcome series (2–4 emails)
      • Email 1: brand promise + what to expect
      • Email 2: best sellers / top content
      • Email 3: objection handling (shipping, returns, sizing, case studies)
      • Optional Email 4: offer (if you use one)
    2. Abandoned cart (2–3 emails)
      • Reminder, then urgency, then alternative/help
    3. Post-purchase (3–5 emails)
      • Order education, usage tips, cross-sell, review request
    4. Winback (2–3 emails)
      • Personalized re-entry based on category interest

    If a business has none of these, switching tools won’t save them. Building these will.

    Automation mistake that burns teams:

    They turn on every default flow in the platform. Suddenly customers receive overlapping messages—welcome offer + cart reminder + “we miss you” in the same week. You can feel the unsubscribe rate rising.

    My rule: map the customer journey on one page first, then implement flows in priority order.


    Best Email Marketing Services to Watch in 2026

    These tools are worth watching in 2026 because they’re either (a) strong generalists with reliable automation and integrations, or (b) specialized for ecommerce behavior and revenue reporting.

    One important stance before we get into the list: pick the platform that matches your complexity.

    • If you’re a creator, local business, or early-stage startup: you probably need “simple, clean, cheap, reliable.”
    • If you’re ecommerce at scale: you need deep event data, segmentation, and revenue attribution.
    • If you’re B2B with sales involvement: you’ll care about CRM alignment, lead scoring, lifecycle stages.

    1) Mailchimp

    Mailchimp is still a go-to for small businesses because it’s approachable. It’s often the first platform a team can use without a dedicated email person.

    Where it shines in 2026:

    • Fast setup, decent templates
    • Solid basics: segmentation, automation, reporting
    • Wide integration ecosystem (especially for smaller tools)

    Where it can bite you:

    • As your segmentation and automation needs grow, you may feel boxed in
    • Reporting can become “good enough” rather than deeply diagnostic

    Who I’d put on Mailchimp:

    • Local service businesses
    • Small shops with low SKU counts
    • Teams that need to ship newsletters and a welcome series quickly

    Quick implementation checklist (what I’d do in week one):

    1. Authenticate domain (SPF/DKIM)
    2. Create one audience (avoid splitting unless you have a reason)
    3. Build a 3-email welcome series
    4. Create a simple preference center (newsletter vs promos)
    5. Set naming conventions for campaigns (so reporting isn’t chaos)

    2) Klaviyo

    If you’re ecommerce and you’re serious about lifecycle marketing, Klaviyo remains the heavyweight.

    Why it’s a 2026 tool to watch:

    • Deep ecommerce data model (browse, cart, purchase, product affinity)
    • Strong segmentation and flow building
    • Analytics that actually answers “did this make money?”

    Tradeoff: it’s not the cheapest, and it rewards teams who are disciplined about events and catalog hygiene.

    A mistake I’ve seen (and fixed):

    A brand migrated to Klaviyo and imported every historical subscriber without cleaning. Engagement tanked, then deliverability followed. We had to:

    • Suppress unengaged users
    • Warm up sending on engaged segments first
    • Rebuild flows with tighter triggers

    Klaviyo didn’t cause the issue—it exposed it.

    3) ActiveCampaign

    ActiveCampaign is the tool I reach for when email automation and CRM-like lifecycle tracking matter, but the business isn’t ready for a full enterprise setup.

    What it does well:

    • Complex automation logic without feeling like you need an engineer
    • CRM features that can support sales + marketing alignment
    • Good fit for B2B, agencies, and service businesses with pipelines

    Tradeoff: you can build a spaghetti monster of automations if you don’t enforce rules.

    My QA-style rule for ActiveCampaign automations:

    • Every automation needs an owner
    • Every automation needs an “exit condition”
    • Every tag added should be removable (or it becomes permanent junk)

    4) Omnisend

    Omnisend is strong for ecommerce brands who want email + SMS without stitching together a bunch of tools.

    Why it’s relevant in 2026:

    • Omni-channel flows (email + SMS)
    • Ecommerce-friendly templates and automations
    • Quick time-to-value for stores that want prebuilt journeys

    Tradeoff: If you want extremely custom data models or unique attribution logic, you might outgrow it.

    Practical use case:

    • Email: cart abandonment reminder
    • SMS: last-chance nudge (only to customers who opted in)

    The combined approach can work really well—as long as you respect frequency. Nothing kills trust like a midnight SMS because someone looked at socks.

    5) Brevo

    Brevo (formerly Sendinblue) keeps pushing into the “affordable marketing suite” category: email, SMS, sometimes chat, and automation for SMBs.

    Why it’s on my 2026 watch list:

    • Solid value for small-to-mid businesses
    • Automation and personalization without enterprise pricing
    • Useful if you want more than just newsletters

    Tradeoff: like many all-in-one-ish tools, it may not be “best in class” at one specific thing—but it can be good enough across several.

    Bonus shortlist: tools I’d also keep an eye on

    Depending on your business model, these come up a lot in real evaluations:

    • HubSpot (more on it below): great for lifecycle + CRM-centric teams
    • MailerLite: underrated for clean, simple email programs
    • ConvertKit (creator-led businesses): strong for newsletters + automations

    Email Automation Services: Why You Need Them

    If you’re still sending only one-off campaigns in 2026, you’re leaving money on the table and you’re probably annoying your list.

    Automation services let you:

    • Respond to behavior (not guesses)
    • Reduce manual sending
    • Create consistent experiences
    • Learn faster (because flows run continuously)

    But “automation” isn’t automatically good. I’ve watched teams set up a dozen flows, pat themselves on the back, then never check if the logic is correct. That’s how you end up emailing a customer “Still thinking it over?” two days after they purchased.

    Key features to look for

    Here’s what I actually look at when I’m evaluating a platform (or QA’ing an implementation).

    1) A sane automation builder

    You want:

    • Clear triggers (“Placed order”, “Visited page”, “Tag added”)
    • Wait steps that behave predictably
    • Branching logic you can read six months later

    If the builder makes you squint, you’ll ship bugs.

    2) Advanced analytics that answer real questions

    Don’t settle for vanity metrics.

    I want to see:

    • Revenue attribution (where relevant)
    • Per-flow performance over time
    • Deliverability indicators (bounce/complaints)
    • Segment comparisons

    3) Integration capabilities that don’t break

    At minimum:

    • Ecommerce: Shopify/WooCommerce/etc.
    • CRM (if you have sales)
    • Forms/landing pages
    • Web analytics (UTMs, event tracking)

    A platform can be amazing, but if your integration randomly drops events, you’ll end up “debugging vibes.”

    4) Deliverability controls

    You don’t need to be a deliverability nerd, but the platform should support:

    • Domain authentication
    • Suppression lists
    • Easy unsubscribe handling
    • Preference centers (ideally)

    A step-by-step automation rollout (what I’d do in 30 days)

    This is the plan I’ve used with small teams that want results without chaos.

    Week 1: Foundations

    1. Authenticate sending domain (SPF/DKIM)
    2. Decide on naming conventions (lists, segments, campaigns, flows)
    3. Define your core events (subscribe, view, add-to-cart, purchase)
    4. Create a baseline segment: “Engaged 30 days”

    Week 2: Welcome flow

    1. Build 3-email welcome series
    2. Add a simple split test to Email 1 (subject line only)
    3. QA it like a product:
      • Subscribe via every form
      • Confirm timing
      • Check mobile rendering
      • Verify links and UTMs

    Week 3: Abandoned cart flow

    1. Trigger: started checkout or added to cart
    2. Exclusion: purchased since starting cart
    3. Copy: helpful first, promotional second
    4. Add product blocks carefully (test missing images, out-of-stock)

    Week 4: Post-purchase + winback

    1. Post-purchase education (reduce returns, increase satisfaction)
    2. Review request (timed to product delivery)
    3. Winback for 60–90 day inactivity

    Then you pause and measure before building “nice to have” flows.

    Examples of automation services to consider

    HubSpot

    HubSpot is the dependable choice when email is part of a broader growth system: CRM, lifecycle stages, sales handoffs, lead scoring, and reporting that a whole team can share.

    When I recommend it:

    • B2B with a real pipeline
    • Teams that are sick of duct-taping five tools together

    Tradeoff: you’ll pay for the convenience, and you should commit to keeping your CRM clean—or it becomes an expensive junk drawer.

    MailerLite

    MailerLite is a cost-effective option for small businesses that want automation without the steep learning curve.

    When it’s a great fit:

    • Simple funnels
    • Newsletters + a few core flows

    Tradeoff: if you need deep ecommerce analytics, you may want a more specialized platform.


    My Experience With Email Marketing Tools

    I’m MARIA, and my angle is different from most “tool review” writeups because I live in the failure modes.

    I’ve tested email programs where:

    • The same campaign sent twice because the scheduler was misunderstood
    • Dynamic blocks displayed blank because a product feed field name changed
    • Segments included internal employees (yep—your team got the VIP discount)
    • UTM parameters were missing, so “email drove zero revenue” (it didn’t)
    • An automation loop re-added users to the same flow every time they clicked

    One of the most painful bugs I’ve seen: a “winback” automation triggered for customers who just bought because the “last purchase date” property wasn’t mapped correctly after a store migration. The brand sent a “We miss you—here’s 15% off” email to recent buyers. Some used it. Revenue looked fine. Profit didn’t.

    Here’s what I learned the hard way: tool choice matters less than your operational discipline.

    So when someone asks me, “Which email marketing service is best?” I ask three questions first:

    1. What’s your business model? (ecom vs B2B vs creator)
    2. Where does your customer data live? (Shopify, CRM, spreadsheets, all of the above)
    3. Who will own the flows weekly? (if the answer is “no one,” pick simpler)

    If you’re a solo marketer and you pick an enterprise-grade platform, you’ll drown. If you’re doing $500k/month ecommerce and you pick a lightweight newsletter tool, you’ll plateau.

    The QA checklist I run before I trust a tool in production:

    • Confirm domain authentication is set
    • Test every form entry path (site popup, footer, checkout opt-in)
    • Verify segmentation with known test contacts
    • Check rendering in Gmail + iOS Mail at minimum
    • Click every link, confirm UTMs
    • Run a small send to engaged users first

    It’s not glamorous. It prevents disasters.


    Conclusion

    Email marketing in 2026 rewards the marketers who treat email like a system: clean data, deliberate segmentation, and automation that matches real customer behavior. The tools—Mailchimp, Klaviyo, ActiveCampaign, Omnisend, and Brevo—are all worth watching, but they shine in different situations.

    If you want my biased-but-practical take: start with the simplest platform that supports (1) reliable automations, (2) decent reporting, and (3) the integrations you actually use. Then build the core flows before you obsess over fancy stuff.

    Your next step: pick one lifecycle moment (welcome, cart, post-purchase, or winback) and build a flow you can improve every week. If you want a deeper platform comparison to narrow your shortlist, use this guide: Best Email Marketing Platforms 2026 Review.

    Top Email Marketing Services to Watch in 2026 dashboard comparison

    Top Email Marketing Services to Watch in 2026 dashboard comparison

  • Best Email Marketing Platforms 2026 Review

    Discover the best email marketing services for businesses in 2026. Compare features, pricing, and user experiences to find the perfect fit for your needs.

    Featured image for In-Depth Review: Best Email Marketing Platforms for Businesses

    Featured image for In-Depth Review: Best Email Marketing Platforms for Businesses

    Top Email Marketing Platforms Reviewed

    Most email marketing services look similar on the pricing page. The differences show up a few weeks later—when you’re trying to segment properly, troubleshoot an automation, or explain to your boss why “revenue from email” doesn’t match Shopify.

    When I evaluate platforms, I’m not just checking feature boxes. I’m asking questions that come from living in the messy middle:

    • Can I trust the data? If a segment says 12,340 contacts, can I reproduce that number tomorrow?
    • How testable are automations? Can I run a safe test without spamming real customers or contaminating analytics?
    • What breaks first as I scale? Is it cost, deliverability, editor performance, or integration reliability?
    • What’s the operational tax? The hours you’ll spend on workarounds, tagging hygiene, and “why didn’t this send?” investigations.

    Below is a practical comparison of the most recommended platforms right now.

    Best Email Marketing Platform

    1) ActiveCampaign

    • Features: Advanced automation, CRM integration, and in-depth reporting tools make ActiveCampaign ideal for teams that want customer relationship management alongside email marketing.
    • Pricing: Plans start around $15/month for basic features, scaling up with additional functionalities.

    Where it shines (in real life):

    ActiveCampaign is the tool I reach for when the business is doing more than broadcasting. If you’re nurturing leads, scoring behaviors, routing handoffs to sales, or running multi-step journeys (email + tags + CRM tasks), it’s hard to beat.

    A lot of platforms claim automation. ActiveCampaign’s automation builder is one of the few that feels like it was designed by someone who’s actually had to maintain automations over time. The logic is visible. Conditions are readable. And when you inherit someone else’s spaghetti automation (you will), you can usually untangle it.

    The tradeoffs:

    • It’s easy to overbuild. Give a marketer 25 triggers and they’ll build a Rube Goldberg machine.
    • CRM features can become a second job if your team isn’t disciplined about pipeline hygiene.
    • If you’re purely eCommerce and don’t need CRM workflows, you might be paying for complexity you won’t use.

    QA note (yes, it matters):

    If you run ActiveCampaign, set up a repeatable testing routine. I typically create:

    • A dedicated test contact set (internal emails + dummy data fields)
    • A naming convention for automations (date + purpose + owner)
    • A “kill switch” tag like DO_NOT_SEND that’s excluded in every send path

    That last one has saved me from at least two “oops” moments when someone changed a trigger and re-enrolled half a list.

    2) Mailchimp

    • Features: A long-standing player in the email marketing arena, Mailchimp offers easy-to-use templates and a robust set of marketing tools, although it has faced criticism for pricing changes.
    • Pricing: Offers a free plan up to 500 contacts, with paid plans starting at $13/month.

    Where it shines:

    Mailchimp is still a strong “first serious tool” for a lot of businesses. The editor is approachable, templates are plentiful, and you can get a decent campaign out the door fast. If you’re a solo operator who needs to send clean newsletters and basic sequences, it can be enough.

    The tradeoffs (and why people leave):

    Pricing and plan limitations can feel like a trap once your list grows or you need more advanced segmentation. I’ve watched teams start on Mailchimp, run happily for a year, then hit the wall when they want:

    • Deeper automation branching
    • More granular audience management
    • More predictable costs at scale

    Also, if your team has multiple stakeholders (marketing, sales, support), you’ll care a lot about permissions and workflow. That’s where “simple” tools sometimes start to creak.

    A mistake I’ve seen:

    People treat “Audiences” like folders and create multiple audiences for the same brand. Then they pay for duplicate contacts and can’t reliably suppress sends. If you use Mailchimp, be intentional: keep duplication under control, document your structure, and decide early whether you’re audience-based or tag-based.

    3) Klaviyo

    • Features: Best suited for eCommerce businesses, Klaviyo provides powerful data integration with Shopify and other platforms to optimize marketing efforts through tailored experiences.
    • Pricing: Free tier available for up to 250 contacts, then priced based on the number of subscribers.

    Where it shines:

    If you sell online and email is revenue-critical, Klaviyo is the grown-up choice. The reason is simple: the eCommerce event data is first-class.

    You’re not just emailing “people.” You’re emailing:

    • Viewed product X twice
    • Added to cart but didn’t purchase
    • Purchased category Y three times
    • High AOV customers who haven’t returned in 60 days

    That’s where segmentation stops being a marketing buzzword and starts being money.

    My experience with Klaviyo (a real before/after):

    I worked with a small eCommerce brand that resisted moving beyond basic campaigns. They were sending the same promo to everyone because it was “easier.”

    We moved them into Klaviyo and did three things first:

    1. Built a clean welcome series with two branches (discount seekers vs product researchers)
    2. Added an abandoned cart flow that didn’t discount immediately (we tested it)
    3. Created a segment for repeat buyers and stopped blasting them with beginner offers

    The immediate win wasn’t just higher open rates—it was fewer annoyed replies and less unsub churn after promos. That’s the part people forget. More relevance reduces list fatigue.

    The tradeoffs:

    • Klaviyo can get expensive as you grow. If your list is bloated with low-intent subscribers, you’ll feel it.
    • You need decent data hygiene. If your Shopify catalog, tags, or events are messy, your targeting will be messy too.
    • It rewards marketers who like testing and iteration. If your org never tests, you won’t get the full value.

    4) Brevo (formerly Sendinblue)

    • Features: Known for its SMS marketing capabilities along with email, Brevo offers a comprehensive suite for businesses looking to combine various marketing efforts.
    • Pricing: Free plan offers 300 emails per day, with premium options based on email volume.

    Where it shines:

    Brevo’s volume-based approach can be a breath of fresh air if you don’t want subscriber-count pricing to dictate everything. And if SMS is part of your mix, having it under one roof simplifies operations.

    This is also one of the better options for businesses that send transactional-ish messages (within policy limits) and want marketing + messaging together.

    The tradeoffs:

    • If you’re an automation power-user, you may find the workflow depth less satisfying than ActiveCampaign.
    • Email designers who want pixel-perfect control can find the editor limiting depending on templates.

    Practical tip:

    If you plan to do both email and SMS, set expectations internally: SMS is not “email but shorter.” The cadence, compliance rules, and customer tolerance are different. I’ve seen brands torch goodwill by sending SMS at the same frequency as email.

    5) MailerLite

    • Features: Great for beginners, it offers a drag-and-drop interface that simplifies campaign creation while including essential automation features.
    • Pricing: Free for up to 1,000 subscribers with a limit on monthly emails.

    Where it shines:

    MailerLite is the platform I recommend when you want the least friction between “I have an offer” and “I sent a decent campaign.” The editor is straightforward, the learning curve is kind, and you can build basic automations without feeling like you need a certification.

    The tradeoffs:

    • You may outgrow it if your segmentation and lifecycle marketing get serious.
    • Complex reporting needs can push you toward more advanced tools.

    A real-world fit:

    Creators, coaches, small local services, and early-stage SaaS newsletters often do great here—especially if they’re disciplined about list quality and don’t try to recreate an enterprise marketing stack.


    Quick picks by business type

    If you just want the blunt shortlist:

    • B2B lead gen + sales handoff: ActiveCampaign
    • eCommerce (Shopify-first): Klaviyo
    • Multi-channel (email + SMS) on a budget: Brevo
    • Newsletter + simple automations: MailerLite
    • General-purpose starter tool: Mailchimp

    That’s not “the truth.” It’s the pattern I’ve seen across teams where time and attention are limited.

    What actually matters when choosing

    Feature lists don’t tell you what day-to-day ownership feels like. These criteria do.

    Deliverability isn’t a feature

    Deliverability is the quiet make-or-break. Most vendors will say they have “high deliverability,” but your results depend on how you behave:

    • List quality (cold lists will hurt you)
    • Sending patterns (spikes are suspicious)
    • Content (spammy patterns still matter)
    • Authentication (SPF/DKIM/DMARC)

    I’ve watched teams blame the platform when the real issue was basic hygiene: old imported lists, no suppression strategy, and weekly “HUGE SALE!!!” subject lines.

    My stance:

    • If you can’t explain where your subscribers came from, don’t import them.
    • If you haven’t mailed a segment in 180 days, treat it as a re-permission project, not a “let’s blast them.”

    Automation you can debug

    Automations are where platforms separate.

    A good automation system lets you answer:

    • Who entered this flow?
    • Why did they enter?
    • Where did they drop off?
    • What email did they receive?
    • What condition blocked them?

    If you can’t answer those questions quickly, your automations will turn into folklore: “I think it works?” That’s not good enough when email is tied to revenue.

    QA habit that pays off:

    Every time you build a new flow, write down (in a shared doc):

    • Entry criteria
    • Exit criteria
    • Suppression rules
    • Any “gotchas” (timezone delays, purchase event timing, coupon constraints)

    That documentation saves real hours later, especially when staff changes.

    Segmentation that stays sane

    Segmentation sounds fun until you have 300 tags and nobody knows which ones matter.

    I’m biased toward:

    • Fewer tags, clearer meaning (behavioral when possible)
    • One source of truth for lifecycle stages (lead, first-time buyer, repeat buyer, churn risk)
    • Periodic pruning (retire tags and segments you no longer use)

    I’ve inherited accounts where segmentation was essentially archaeology. The marketing team was afraid to delete anything, so everything stayed—forever. That’s how you end up sending the wrong message to the right person.

    Understanding the Costs of Email Marketing Services

    Cost is where platform choice gets emotional, fast. And it should—email looks cheap until you factor in growth, add-ons, and the internal time you spend wrangling it.

    Determining the cost of email marketing services can vary widely based on the platform and features required. Here are some essential insights into pricing in 2026:

    • Monthly Subscriptions: Many platforms charge monthly fees based on the number of subscribers. On average, costs range from $15 to $500 monthly, depending on the services included. For instance, some services, like ActiveCampaign, can range from $15 to $150 based on added functionalities.
    • Premium Features: Services that offer advanced automation or premium templates may charge extra. Expect to pay around $500 to $1,400 monthly if you choose to engage with specialized agencies to handle your email marketing.

    That investment can yield substantial returns, with reports indicating email marketing generates an average of $36 to $42 for every dollar spent (Digital Applied).

    How I model email cost (simple, but effective)

    If you want a sanity check before you commit, do this mini-model:

    1. Estimate your list growth for 12 months (be honest)
    2. Price the tool at three list sizes (now, 6 months, 12 months)
    3. Add the “hidden” lines:
      • Designer time (or template cost)
      • Copywriting time
      • Integration help (Shopify, WordPress, CRM)
      • QA/testing time (yes, it’s a line item)

    Then ask: are you building an email program, or just sending newsletters? If you’re building a program, spending more on a tool that reduces chaos can be cheaper overall.

    Agency vs in-house: the part nobody budgets for

    The $500 to $1,400 monthly agency range can be worth it when:

    • You don’t have anyone who knows lifecycle strategy
    • You need someone to build flows fast (welcome, cart, winback)
    • Your team can’t reliably test and maintain what they build

    But agencies can also create dependency. I’ve seen accounts where the agency built everything, documented nothing, and the client couldn’t change a subject line without breaking something.

    If you hire help, require:

    • Automation maps
    • Ownership of templates
    • A clear naming system
    • A handoff session recorded (seriously)

    80/20 Rule in Email Marketing

    In email marketing, the 80/20 rule suggests that 80% of your results come from about 20% of your efforts. This principle can guide your strategy significantly; focusing on high-impact areas can yield better engagement and conversions.

    More insights on applying this rule are available in this Marketing Fuel article.

    What the “20%” usually is (from what I’ve seen)

    If you’re trying to get real returns without living inside your ESP all day, focus here first:

    1. Welcome series (set expectations, deliver value, drive first action)
    2. Abandoned cart / browse abandonment (eCommerce)
    3. Post-purchase (reduce refunds, increase repeat buys)
    4. Winback (not “we miss you,” but a reason to return)
    5. Segmentation for high intent (your best customers should not get beginner messaging)

    Everything else—perfect template tweaks, fancy countdown GIFs, endless newsletter sections—tends to be the “80% effort” part.

    A concrete 80/20 example

    One team I worked with spent weeks redesigning their newsletter layout. It looked nicer, sure. But the revenue barely moved.

    Then we did a boring change: we split their list into two segments—people who clicked any product link in the last 30 days, and people who didn’t. High-intent got a tighter email with three products and a clear CTA. Low-intent got a story-driven email with one soft offer.

    Same list. Same brand. Different intent.

    That’s the kind of 80/20 that actually moves metrics.

    My Experience With This

    I’m MARIA, and throughout my years in digital marketing, I’ve seen firsthand how the right email marketing platform can transform a business’s communication strategy.

    But I’ve also seen how the wrong platform—or a platform configured badly—creates a slow-motion disaster:

    • Segments that don’t match reality
    • Automations that silently stop enrolling people
    • Duplicate contacts that inflate costs
    • Reports that can’t be reconciled with actual sales

    The most common failure mode: migration without a plan

    A lot of businesses switch platforms because they’re frustrated. Totally fair. But then they migrate in a rush:

    • They import everything (including dead contacts)
    • They recreate campaigns, but not the underlying logic
    • They forget suppression lists
    • They don’t warm up sending properly

    And then deliverability drops, or automations underperform, and they conclude the new tool is worse.

    If you’re migrating, treat it like a project. A small one, but a real one.

    My basic migration checklist:

    • Export and audit your list (remove bounces, role emails, obvious junk)
    • Document your current automations (screenshots + logic)
    • Rebuild core flows first (welcome, cart, post-purchase)
    • Run parallel tests with internal contacts
    • Start with your most engaged segment for early sends

    It’s not glamorous. It prevents pain.

    Testing emails like a QA person

    If you want fewer surprises, steal a few QA habits:

    • Inbox rendering checks: at minimum, Gmail + Apple Mail + Outlook web
    • Link verification: every CTA, every footer link, every social icon
    • UTM consistency: decide a naming convention once, enforce it always
    • Suppression sanity: confirm customers who already purchased don’t get “first order” promos
    • Edge cases: what happens if someone buys twice in one day? unsubscribes mid-flow?

    Most teams only test the happy path. The unhappy path is where your brand gets embarrassing.

    Free Email Marketing Services

    If you’re just starting or managing tight budgets, several platforms offer free email marketing services that can help you get off the ground without significant investment:

    1. MailerLite – A great option for small businesses, offering a generous free tier for up to 1,000 subscribers and 12,000 emails per month.
    2. Brevo – Provides an impressive range of features even on its free plan, including SMS integration and automation capabilities.
    3. Sender – Known for simple automation and high sending limits, making it an excellent choice for startups.
    4. Zoho Campaigns – This tool allows up to 2,000 contacts and 6,000 emails per month, making it suitable for larger lists as well.
    5. HubSpot – Their email marketing tools are robust and come at no cost, particularly beneficial for those just entering the market.

    What free plans are actually good for

    Free plans are perfect for:

    • Validating that your offer resonates
    • Building a simple lead magnet funnel
    • Learning basic segmentation and sending cadence
    • Creating your first templates and brand style

    Free plans are not great for:

    • Heavy automation
    • Complex reporting needs
    • High-volume eCommerce flows
    • Teams that need roles/permissions

    My opinion: start free if you’re truly early, but don’t build a “forever system” around a free tier. Once email is making money, upgrade quickly so you’re not constantly designing around limits.

    How to pick in 30 minutes

    If you’re overwhelmed, do this quick decision process:

    1. Are you eCommerce-first?

      • Yes → start with Klaviyo
      • No → go to step 2
    2. Do you need sales CRM + marketing automation together?

      • Yes → ActiveCampaign
      • No → go to step 3
    3. Do you care about email + SMS in one tool?

      • Yes → Brevo
      • No → go to step 4
    4. Do you want the simplest tool that won’t fight you?

      • Yes → MailerLite
      • No / already on Mailchimp and comfortable → Mailchimp is fine until you outgrow it

    That’s it. Don’t overthink it.

    Conclusion

    With the right email marketing platform, you can enhance your communication strategy, engage your audience more effectively, and drive results that contribute to your business growth.

    My advice is simple: pick the platform that matches your business model and operational reality, not the one with the prettiest feature grid. If you’re serious about email, invest in a tool you can test, maintain, and scale—without creating a fragile mess.

    Next step: choose two platforms from the list, build the same welcome flow in both, and time yourself. The one that feels clearer and more reliable at build-time will usually be the one you’re happiest owning.

    Revnix

  • AI Email Transformation: The Future of Email in 2026

    Discover how AI will revolutionize email experiences by 2026, enhancing personalization, efficiency, and deliverability.

    Featured image for How AI Will Transform Your Email Experience in 2026

    Featured image for How AI Will Transform Your Email Experience in 2026

    Understanding Email in 2026

    By 2026, email won’t feel like a dumb pipe for messages. It’ll behave more like an adaptive workspace—AI sitting between you and the inbox, constantly deciding what deserves attention, what can wait, and what’s probably junk.

    That matters because email is still massive. We’re talking nearly 4.7 billion email users globally, projected to reach around 4.89 billion by 2027 (Statista). At that scale, tiny improvements—better timing, better relevance, fewer spam complaints—compound fast.

    Here’s the part people miss: AI doesn’t just “write emails.” In the real world, the biggest gains come from three unsexy areas:

    1. Decisioning (who gets what, when)
    2. Deliverability hygiene (auth + reputation protection)
    3. Feedback loops (learning from results without waiting for a quarterly report)

    AI-Driven Personalization

    In 2026, personalization is less about sprinkling in a first name and more about predicting intent. AI will generate content and choose offers based on behavior, preferences, and interactions—not just what you say you like, but what you actually do.

    Organizations using AI in email marketing can see a 17–26% lift in revenue per send (Digital Applied). I believe that range because I’ve watched “batch-and-blast” lists turn into behavior-based segments and suddenly the same list size produces noticeably more revenue—without increasing volume.

    A concrete 2026-style personalization stack usually looks like this:

    • Behavioral inputs: pages viewed, product usage, support tickets, previous clicks
    • Context signals: device, time zone, typical open time, purchase cycle stage
    • Creative assembly: subject line + intro + offer block chosen dynamically
    • Send-time optimization: AI picks a window when the user is historically receptive

    Real example I’ve seen (and fixed): a SaaS company personalized only the hero image and subject line. Looked fancy. Revenue didn’t move. Once we switched to behavior-based branching (trial user who hit a feature limit vs. trial user who never invited teammates), conversions jumped—not because the copy was prettier, but because the email finally matched the moment.

    Common mistake: letting AI “personalize” itself into nonsense. If your product data is messy (duplicate events, wrong lifecycle stage, stale attributes), the model confidently produces the wrong email. The fix isn’t more prompts; it’s cleaning your tracking and enforcing a few hard rules (like “don’t pitch an upgrade to someone who churned last week”).

    Enhanced Deliverability

    Deliverability is where AI will quietly earn its keep. Not by “beating spam filters” with tricks—those tricks tend to die fast—but by keeping your sending program aligned with modern requirements and reputation signals.

    With evolving authentication standards like SPF, DKIM, and DMARC, emails sent without proper authentication can see inbox placement rates drop to as low as 44% (Topol). That number tracks with what I’ve seen when a domain’s auth breaks or a new subdomain is spun up without the right records—sends don’t bounce, they just vanish into spam/promo purgatory.

    By 2026, AI systems will do more of the “boring checks” automatically:

    • Verify SPF/DKIM/DMARC alignment before a campaign launches
    • Detect unusual bounce/complaint spikes early (before the damage spreads)
    • Predict which segments or subject lines are likely to trigger spam complaints
    • Recommend throttling or warm-up when volume jumps

    Step-by-step deliverability workflow I’d run in 2026 (still works now):

    1. Preflight auth: confirm SPF/DKIM/DMARC pass for the exact from-domain.
    2. Segment risk scoring: new recipients, old recipients, recent engagers.
    3. Send in waves: start with high-engagement users, then expand.
    4. Monitor complaints + bounces: adjust fast, don’t “wait and see.”
    5. Post-send learning: feed outcomes back into segmentation rules.

    Common mistake: people treat authentication as a one-time setup. Then someone changes DNS, migrates ESPs, or adds a new sending domain—and nobody re-validates. AI-driven compliance checks should catch that stuff before it costs you weeks of reputation recovery.

    AI-Powered Campaign Analysis

    The analysis piece is where AI stops being “automation” and becomes decision support. By late 2026, it’s expected that 61% of enterprise email programs will incorporate AI across multiple elements of campaign development (Digital Applied).

    In practice, that looks like:

    • Subject line tests that don’t just pick winners, but explain why something won
    • Content recommendations based on downstream metrics (not just opens)
    • Segmentation suggestions that you can approve (or reject) with guardrails
    • Real-time monitoring that flags anomalies (deliverability dip, CTA fatigue)

    Anecdote: I once watched a team celebrate a huge open-rate lift from AI-written subject lines—then revenue stayed flat. The AI had learned how to trigger curiosity opens, but the body didn’t deliver value. In 2026, better systems will optimize for what you actually care about: conversions, retention, pipeline—whatever your north star is.

    Setting Up Your Gmail Experience

    If you want to benefit from AI in email—not just read about it—your daily inbox setup matters. Gmail is where a lot of this gets productized first, and it’s also where bad habits (chaos labeling, “I’ll search later,” 9,000 unread) will punish you.

    Even if you’re focused on marketing, the way you handle email is a decent proxy for how your customers experience it. If your own inbox is a mess, odds are your program is too.

    Creating Your Gmail Account

    Creating a Gmail account is still the front door. Go to the Gmail account creation page, set the basics, and then do one thing most people skip: decide what this inbox is for.

    Quick setup that saves headaches later:

    1. Create the account.
    2. Turn on 2-step verification (not glamorous, but it prevents account takeover).
    3. Decide whether this inbox is personal, business, or “testing/newsletters.”
    4. If it’s for business, use a consistent identity (name + profile) so people recognize you.

    Why so strict? Because AI features like priority sorting and suggested replies work better when the inbox has consistent patterns—real conversations vs. random promotional junk.

    Optimizing Gmail Features

    Gmail will keep expanding AI features in 2026. Some of them are legitimately useful; some are “nice demos” that can also create risk if you blindly trust them.

    Here are the ones I’d actually bet on:

    • Smart Compose: speeds drafting. Great for repetitive replies, dangerous for nuance. I use it for structure, then I rewrite the sentence that matters.
    • Priority Inbox: reduces cognitive load by surfacing what you tend to respond to. The win isn’t magic sorting—it’s fewer context switches.
    • Smart Reply: useful for quick acknowledgments, but it can make you sound like a robot if you never edit.
    • Dynamic Email Content: emails that update based on interaction, status changes, or preferences.

    Step-by-step: a Gmail setup I’ve shipped for busy teams (support leads, founders, sales):

    1. Pick one inbox style: Priority Inbox or a clean default. Don’t keep switching.
    2. Create 3–5 labels max: “Waiting on,” “Finance,” “Customers,” “Internal,” etc.
    3. Add filters for the obvious noise: receipts, system alerts, newsletters—label them and skip the inbox when appropriate.
    4. Turn on nudges/follow-ups: the AI reminder features are worth it if you’re prone to dropping threads.
    5. Use templates cautiously: templates + AI can speed replies, but review the first two lines every time (tone mistakes happen there).

    Common mistakes I see:

    • Turning on every feature, then blaming Gmail when it feels chaotic.
    • Using Smart Reply in sensitive situations (refunds, escalations) and sounding cold.
    • Letting “Priority” hide things you actually needed—then missing a deadline.

    The goal is simple: set Gmail up so AI reduces your workload without quietly making decisions you didn’t approve.

    The Future of AI in Email Environments

    As we head into 2026, AI in email shifts from “help me write” to “help me decide.” The best systems will act like a sharp assistant: summarizing threads, suggesting next actions, and preventing avoidable mistakes.

    The worst systems will confidently do the wrong thing at scale. So you’ll want guardrails.

    Intelligent Automation

    Automation is going to eat the low-value parts of email. According to Qualtir, AI will handle low-priority emails, freeing professionals to focus on higher-value communication.

    That aligns with what I’m seeing already: the most valuable automation isn’t auto-writing full messages—it’s:

    • Summarizing long threads into decisions + open questions
    • Drafting a reply you can approve in 20 seconds
    • Auto-labeling and routing (billing vs. support vs. sales)
    • Detecting when a message shouldn’t be sent yet (missing info, wrong recipient)

    Real scenario: a support manager gets 120 emails/day. AI triage can route 40 of those to the right queue, summarize 30, and mark 20 as “FYI.” Now they’re only truly writing maybe 30. That’s a different job.

    Common mistake: automating without an “escape hatch.” Always keep a manual review path for edge cases—VIP customers, legal requests, chargebacks, anything reputational.

    Behavioral Analysis

    AI will get much better at understanding behavior patterns and using them to segment. Done right, you send fewer emails and earn more.

    Campaigns leveraging behavioral data can generate up to 760% more revenue than traditional broadcast sends (Digital Applied). Big number, but believable when you compare “everyone gets the same promo” to “only people showing intent get the right message.”

    Step-by-step: how I’d implement behavioral segmentation without making it creepy

    1. Start with 3 intent buckets: high intent, warm, cold.
    2. Define the events that move someone between buckets (pricing page view, trial activation, repeat purchase).
    3. Cap frequency per bucket (cold users get fewer emails).
    4. Add a fallback for missing data (don’t guess wildly).
    5. Measure outcomes beyond opens: revenue per send, churn, unsubscribes.

    Mistake I’ve cleaned up: teams ingest every event they can, then let AI decide. You end up targeting someone because they opened a random transactional email, not because they actually wanted the product. Fewer, higher-signal events beat “everything plus AI.”

    Enhanced User Experience

    By 2026, more emails will be interactive and preference-driven. Think:

    • Embedded actions (confirm, schedule, update preferences)
    • More transparent data use (explicit preferences, “zero-party” data)
    • Tone and accessibility improvements (clearer language, better formatting)

    This is where trust becomes the real KPI. If your AI-generated emails feel manipulative, you’ll pay for it in spam complaints and unsubscribes. If they feel helpful—short, relevant, timely—people keep you.

    A quick gut-check I use: if a recipient could reasonably say “wait, how did they know that?” then you’re probably over-targeting. Make the relevance explainable.

    Conclusion

    AI will transform your email experience in 2026, but not in the sci-fi way people pitch on slides. The practical transformation is this: less manual sorting, fewer wasted sends, faster iteration, and more pressure to be trustworthy because the tools are powerful.

    If you’re a business, the advantage won’t come from “using AI.” It’ll come from using AI with constraints: clean data, sane segmentation, authentication locked down, and humans reviewing the handful of messages where tone and judgment matter.

    If you’re an individual living in Gmail all day, set up your inbox so the AI is working for you, not just adding another layer of suggestions to ignore. Spend an hour on filters, labels, and priority rules—you’ll get that time back in a week.

    Next step: pick one area—personalization, deliverability, or automation—and improve it end-to-end. Half-implementations are where email programs go to die.

    FAQ

    What is AI email transformation?

    AI email transformation is using artificial intelligence to improve how email is created, delivered, and managed—especially personalization, deliverability, automation, and performance analysis.

    A real-world example: instead of manually writing 10 versions of an email, AI helps draft variants, predicts the best send time per segment, and flags deliverability risks before you push send.

    How will AI improve email personalization by 2026?

    By 2026, AI will use behavior and preferences to tailor content, timing, and offers. The big shift is from “static segments” (like industry or job title) to dynamic intent (what the user is doing right now).

    Practical example: a user visits your pricing page twice in 48 hours. AI can trigger a short email that answers the top objections for that plan, rather than dumping them into your next generic newsletter.

    Common mistake: over-personalizing with weak signals. If you personalize based on one accidental click, it feels random—and people unsubscribe.

    What should I do to prepare my email marketing for 2026?

    Do three things in order:

    1. Fix authentication and sending discipline (SPF/DKIM/DMARC, list hygiene, frequency caps).
    2. Define a simple behavioral model (3–5 lifecycle stages max) and map triggers.
    3. Introduce AI where it saves time safely (drafting, summarization, analysis) and keep humans in the loop for sensitive flows.

    If you can’t explain why a customer got an email in one sentence, your system’s too complicated—or your data’s lying to you.

  • Top Email Marketing Platforms for 2026

    Discover the best email marketing platforms for small businesses in 2026. Compare features, costs, and user satisfaction.

    Featured image for Email Marketing Platforms: Which Is Best for 2026?

    Featured image for Email Marketing Platforms: Which Is Best for 2026?

    Comparing Email Marketing Platforms for 2026

    If you’re doing email marketing for small businesses, your platform choice shows up everywhere: how quickly you can ship campaigns, how clean your list stays, whether automations actually run, and whether you can tie email to revenue without a spreadsheet circus.

    In 2026, most platforms can “send newsletters.” That’s table stakes. What separates them is:

    • Automation depth (can you build real branching journeys, or just simple autoresponders?)
    • Segmentation (behavioral, purchase-based, lead-source-based, engagement-based)
    • Integrations (Shopify/WooCommerce, booking tools, CRMs, forms, ad platforms)
    • Reporting that you’ll actually use (revenue attribution, cohort performance, deliverability signals)
    • Team workflow (approvals, roles, templates, multi-brand setups)

    One opinion upfront: don’t buy a “power platform” because you feel like you should. Buy it because you have a specific automation or segmentation problem you can’t solve otherwise. I’ve seen small teams spend months building elaborate flows… when two clean segments and a weekly send would’ve outperformed everything.

    Top Email Marketing Platforms

    Here are the common players you’ll keep running into, plus what they’re genuinely good at.

    1. Mailchimp

      • Best for: Small businesses focusing on ease of use.
      • Strengths: Comprehensive integrations, user-friendly interface, and strong analytics.
      • Pricing: Starts at $11/month.
    2. Klaviyo

      • Best for: E-commerce brands wanting deep insights.
      • Strengths: Advanced segmentation and reporting features.
      • Pricing: Free tier, paid plans from $20/month.
    3. ActiveCampaign

      • Best for: Marketing teams needing multi-channel engagement.
      • Strengths: Robust automation and CRM capabilities.
      • Pricing: Plans start at $39/month.
    4. MailerLite

      • Best for: Beginners and those on a tight budget.
      • Strengths: Simple drag-and-drop editor and landing page features.
      • Pricing: Free plan available, paid plans from $10/month.
    5. ConvertKit

      • Best for: Creators and bloggers.
      • Strengths: Easy funnels for lead generation and digital products.
      • Pricing: Free tier, paid plans from $15/month.

    If you’re stuck, start by labeling yourself honestly:

    • Local service business (dentist, salon, contractor): you need reminders, seasonal promos, simple segmentation.
    • E-commerce (DTC or niche retail): you need product-driven flows, purchase segmentation, abandoned cart, post-purchase, winback.
    • Creator/education (courses, coaching, newsletter): you need opt-ins, lead magnets, tagging, and simple sales sequences.
    • B2B services/SaaS-lite: you need lead scoring, CRM-ish behavior, longer nurturing.

    Then choose the platform that’s “boring and reliable” for that model. You’re not buying potential—you’re buying a system you’ll use every week.

    What I’d evaluate first

    People love comparing feature checklists. I don’t. I evaluate platforms in a practical order:

    1) Deliverability basics

    If your emails don’t land in the inbox, nothing else matters. Most reputable tools handle the fundamentals, but your outcomes depend on your list hygiene and sending habits.

    What I look for:

    • Easy-to-find unsubscribe management
    • Bounce and complaint handling that isn’t buried
    • Simple segmentation by engagement (opened/clicked in last X days)

    2) Automation you can maintain

    The best automation is the one you’ll maintain when you’re busy.

    A simple, high-performing starter set for many small businesses:

    • Welcome sequence (2–4 emails)
    • Abandoned cart (if e-commerce)
    • Post-purchase follow-up (care tips, review request, cross-sell)
    • Lapsed customer winback (after 60–120 days, depending on your cycle)

    If a platform makes those hard to build, or hard to understand six months later, you’ll pay for it later.

    3) Segmentation that matches how you make money

    Segmentation isn’t “advanced.” It’s just relevance.

    Examples that actually move revenue:

    • Customers vs. non-customers
    • High AOV buyers vs. bargain buyers
    • People who bought Category A but not Category B
    • Leads from “discount popup” vs. “content download”

    Klaviyo is particularly strong for e-commerce-style segmentation. ActiveCampaign is strong when segmentation needs to blend with CRM-ish behavior.

    4) Integrations you won’t regret

    This is where hidden cost lives.

    Common integration traps I’ve seen:

    • Your form tool doesn’t pass source/UTM cleanly, so you can’t segment by acquisition channel.
    • Your checkout tool syncs customers but not line items, so product-based segmentation becomes a hack.
    • Your booking tool doesn’t trigger events reliably, so reminders and follow-ups misfire.

    If you’re on Shopify, you’ll feel these issues immediately. If you’re on a service stack (Squarespace + Acuity/Calendly + Zapier), you’ll feel them slowly—then all at once.

    Real-world examples

    Here’s what “platform fit” looks like when it’s real, not theoretical.

    • A recent case study showed that small businesses using Klaviyo experienced an average revenue growth of 20% after implementing targeted email automation. That tracks with what I’ve seen when an e-commerce brand goes from “blast everyone” to a few tight segments plus lifecycle flows.

    • Similarly, businesses that transitioned to ActiveCampaign reported improved engagement rates by over 30% after personalizing their email campaigns. In practice, this often happens when a business stops sending generic newsletters and starts sending role- or interest-based sequences.

    A quick story from the trenches: I once watched a small online shop move to a more “powerful” platform because they wanted smarter automations. The tool wasn’t the problem—their data was. Product names were inconsistent, events were firing twice, and half the list came from an old giveaway. They spent weeks building flows that looked gorgeous and performed… fine.

    The fix wasn’t new software. It was:

    • cleaning the list,
    • standardizing product categories,
    • setting a hard rule to suppress unengaged subscribers,
    • and simplifying flows to match their actual buying cycle.

    Once that happened, the same platform finally looked “amazing.”

    Getting started with email marketing

    If you’re asking, “How do I start email marketing?”, don’t start with a 20-email automation masterpiece. Start with a system you can run every week.

    Here’s a step-by-step setup I’d recommend for most small businesses:

    1. Build your audience (opt-in only)

      • Put a signup form in obvious places: homepage, blog, checkout, booking confirmation.
      • Offer a simple reason to join (discount helps e-commerce; a useful checklist works great for services).
    2. Set up your minimum viable segments

      • New subscribers (last 30 days)
      • Active engaged (opened/clicked in last 60–90 days)
      • Customers (if you can track purchases)
      • Lapsed (no open/click in 90–180 days, depending on send frequency)
    3. Write two campaigns before you write ten

      • One “value” email (teach, show before/after, answer a common question)
      • One “offer” email (specific product/service, clear deadline, clear CTA)
    4. Create a short welcome sequence

      • Email 1: deliver the offer/lead magnet + set expectations
      • Email 2: your best proof (reviews, results, story)
      • Email 3: a clear next step (book, buy, reply)
    5. Track the right metrics

      • Don’t obsess over vanity opens.
      • Watch clicks, conversions, revenue (if applicable), unsubscribe rate, and list growth.

    Common early mistakes (I’ve made some of these myself):

    • Sending to the whole list forever (no segmentation)
    • Never cleaning unengaged subscribers (deliverability slowly tanks)
    • Over-designing emails instead of writing clear copy
    • Testing subject lines while ignoring the offer and landing page

    Assessing the Costs of Email Marketing

    Email looks cheap—until you add up the real operating cost: list growth, higher tiers, integrations, time spent building automations, and sometimes outside help to stop things from breaking.

    Still, the channel is usually worth it. As of 2026, the average ROI for email marketing continues to be impressive, with estimates showing that for every $1 spent, businesses can expect between $36 to $42 in return. I treat that range as “possible when you’re doing the basics well,” not a guarantee. But I’ve seen enough accounts where email is the highest-margin channel that I’m comfortable budgeting for it early.

    The cost buckets that actually matter

    Most small business owners only look at the monthly plan price. That’s only one slice. Here’s the full picture.

    1) Platform fees (the obvious part)

    • Basic Plans: Many platforms offer free tiers or basic packages starting around $10 to $20 per month.
    • Paid Plans: These can range from $50 to $300 monthly, depending on features and the size of your email list.

    The gotcha: pricing often scales on contacts, not sends. If you never clean your list, you’ll pay for ghosts.

    2) Integration and tooling costs (the sneaky part)

    Even if your platform is $20/month, you might also be paying for:

    • a form tool
    • an SMS add-on
    • Zapier/Make automations
    • Shopify/WooCommerce apps
    • a landing page builder

    None of those are “wrong.” But this is how a $20/month email stack turns into $180/month.

    My bias: consolidate when you can. Fewer moving parts means fewer broken zaps, fewer missing tags, fewer support tickets.

    3) Creative + operational time (the part you feel)

    Some teams do everything in-house. Others need help.

    • Freelancer/Agency Costs: Hiring external help typically ranges from $50 to $150 per hour, depending on expertise.

    Where that money tends to go:

    • template setup and brand styling
    • automation building (welcome, cart, post-purchase)
    • segmentation logic
    • monthly campaign production
    • reporting and experimentation

    If you’re hiring help, be clear about outcomes. “Build me a welcome flow” is vague. “Build a 3-email welcome flow for new leads that pushes a first purchase within 10 days” is actionable.

    A practical step-by-step cost estimate

    Let’s do a realistic scenario. Say you’re a small e-commerce brand or local business with an online booking flow.

    Assumptions (keep it simple):

    • You start on a $10–$20/month plan.
    • You send 4 campaigns per month.
    • You have one short welcome automation.
    • You spend 3–5 hours/month writing and building emails.

    Month 1 setup:

    1. Choose platform tier: $10–$39 (depends on tool)
    2. Set up forms + basic segments: 1–2 hours
    3. Write welcome sequence (3 emails): 2–4 hours
    4. Create one reusable template: 1–3 hours

    If you do it yourself, your cash cost might be low—but your time cost is real.

    Ongoing monthly:

    • Platform: $10–$300 depending on list size/features
    • Your time: ~3–8 hours/month if you’re consistent
    • Optional: freelancer help (say 2 hours/month): $100–$300/month

    The point: email is rarely expensive in cash at the beginning. It becomes expensive when you either (a) scale successfully, or (b) ignore list hygiene and pay for dead contacts.

    How much is a 1000 email list worth?

    People ask this when they’re tempted to buy lists or run lead-gen ads. The numbers get thrown around a lot, so here’s what you stated (and what I typically see quoted in the market):

    • Consumer Lists: Typically cost between $100 to $400 CPM.
    • B2B Lists: May exceed $600 to over $1,000 CPM, depending on the specificity and quality of the data.

    Now my stance: buying lists is almost always a bad move for small businesses.

    Not because it’s morally wrong. Because it’s mechanically self-sabotage:

    • You’ll get low engagement.
    • You’ll rack up complaints and bounces.
    • Your deliverability can degrade, which then hurts emails to your real subscribers.

    If you want a “worth it” framing for a list of 1,000 opt-in subscribers, I use a simpler question:

    If I email these 1,000 people once a week for the next year, can I create enough value (and offers) to earn more than the platform cost?

    When the list is permission-based and aligned with what you sell, the answer is usually yes.

    Two cost mistakes I keep seeing

    Mistake 1: Paying for features you don’t operationalize

    Example: a team pays for advanced automation but only sends a monthly newsletter. That’s not “bad,” but it’s wasted budget.

    Fix: either downgrade, or commit to 2–3 automations that match your customer journey.

    Mistake 2: Never pruning unengaged subscribers

    This one is brutal. Your list grows, your bill grows, and deliverability drifts down.

    Fix: create a segment like “no opens/clicks in 120 days,” then suppress or run a re-engagement campaign. Be willing to let people go.

    A real example: cost vs. outcome

    One of the cleanest wins I’ve seen for a small service business (think: high-margin appointments, not e-commerce) was embarrassingly simple.

    They were paying for a mid-tier plan because their list was bloated—years of contacts, most of whom hadn’t engaged in forever. Campaign performance was mediocre, and they assumed email “didn’t work anymore.”

    We did three things over two weeks:

    1. Segmented engaged vs. unengaged (based on recent opens/clicks).
    2. Stopped emailing the unengaged group (immediately lowered sends and reduced noise).
    3. Built a 3-email follow-up after a quote request: confirmation → proof → last-chance nudge.

    Result: platform costs dropped (fewer billable contacts), engagement went up, and they started getting bookings that were clearly attributable to those follow-ups.

    No fancy AI. Just discipline.

    Conclusion

    Choosing the right email marketing platform in 2026 isn’t about picking the tool with the longest feature list. It’s about picking the tool you’ll actually use to run a simple, repeatable communication system—one that earns trust and revenue without eating your week.

    Here’s the decision I’d make if I were in your shoes:

    • If you want a straightforward tool that won’t intimidate you, start with Mailchimp or MailerLite.
    • If you sell products online and want segmentation that maps to purchase behavior, Klaviyo is hard to ignore.
    • If your business needs deeper journeys, lead scoring, and CRM-like coordination, ActiveCampaign is usually worth the learning curve.
    • If you’re a creator selling digital products or building a newsletter-first business, ConvertKit stays pleasantly focused.

    The “one afternoon” next step

    If you do nothing else after reading this, do this in the next 2–3 hours:

    1. Pick one platform you can afford today.
    2. Create two segments: engaged (last 90 days) and everyone else.
    3. Write one welcome email that sets expectations and gives a clear next step.
    4. Send one campaign this week to the engaged segment only.
    5. Measure one thing that matters (clicks, replies, bookings, purchases)—not just opens.

    That’s enough to get momentum, data, and confidence.

    A common trap to avoid

    Don’t wait for the “perfect” platform before you start sending. I’ve seen owners spend a month comparing tools and zero weeks communicating with customers. Email rewards consistency. Even a basic platform plus a clean list and steady cadence beats a premium platform sitting idle.

    Frequently Asked Questions

    1. How do I start email marketing?
    To start email marketing, first build an opt-in list, choose an email marketing platform that suits your needs, and begin creating engaging content that resonates with your audience.

    2. How much is a 1000 email list worth?
    Consumer email lists typically range from $100 to $400 CPM. B2B email email lists can be more expensive, ranging from $600 to over $1,000 CPM.

    3. Is email marketing still worth it in 2026?
    Absolutely. Email marketing remains one of the highest-performing channels for ROI, with the potential to earn between $36 to $42 for every $1 spent.

    4. What are some effective email marketing examples?
    Examples include personalized welcome emails, automated cart abandonment reminders, and targeted content newsletters.

    5. What is the salary range for email marketers in 2026?
    As of 2026, the average salary for an email marketing specialist in the U.S. is around $72,172 per year, with variations depending on experience and location.

    If you want the “best platform,” stop thinking in brands and start thinking in workflows. Pick the tool that makes the next 10 emails easy—and go send them.

  • How to Become a Project Manager in 2026

    Discover the step-by-step guide on how to become a project manager in 2026, even without experience. Explore career pathways in project management today!

    Featured image for Step-By-Step Route to Project Management Careers in 2026

    Featured image for Step-By-Step Route to Project Management Careers in 2026

    Step-by-Step Guide: How to Become a Project Manager

    Getting started in project management can feel daunting, especially if you don't have prior experience. However, there are various routes you can take to secure a project management position. Here’s a step-by-step guide on how to become a project manager, including insights on breaking into the field without existing experience.

    1. Understand the Role of a Project Manager

    Before you dive into courses and applications, get painfully clear on what the job is.

    A project manager’s real job isn’t “being organized.” It’s making sure the team delivers the agreed outcome by the agreed date, within the agreed constraints—while reality keeps changing.

    In practice, that means you’re doing four buckets of work over and over:

    1. Define: What are we doing, for whom, by when, and what’s not included?
    2. Plan: Tasks, owners, dependencies, risks, budget/time tradeoffs.
    3. Run the work: Meetings that matter, unblock people, keep decisions moving.
    4. Close: Confirm acceptance, capture learnings, stop the project from limping along forever.

    Common early-career misconception: PMs “own the work.” You don’t. You own the system around the work—clarity, commitments, and follow-through.

    A quick self-check I use when coaching someone new: if you can explain the project’s goal, current status, top 3 risks, and next 3 decisions in under 60 seconds, you’re already thinking like a PM.

    2. Identify Your Transferable Skills

    You might be surprised to realize that you already possess many skills relevant to project management from previous jobs, school projects, or volunteer work. Skills such as communication, leadership, organization, and problem-solving are key assets.

    But “transferable skills” only help if you translate them into project-shaped stories.

    Here’s a simple way to do that—take anything you’ve done and map it into a mini project:

    • Goal: What was the outcome?
    • Stakeholders: Who cared (boss, customer, teammates, vendors)?
    • Constraints: Time, budget, tools, rules.
    • Plan: How did you break it down?
    • Execution: How did you coordinate people?
    • Result: What changed because you did it?

    For instance, coordinating a group project during college or managing a community event can be classified as project management experience, even if it’s informal. As mentioned in a recent article, "this reflects what employers value: an individual's ability to lead regardless of the title or role" (FlashGenius).

    Real example (the kind hiring managers actually respect):

    You worked retail and got tired of closing shifts being chaos. So you:

    1. Listed the recurring closing tasks (cleaning, cash, restock, signage).
    2. Noticed two tasks blocked each other (restock couldn’t happen until inventory count finished).
    3. Swapped the order, made a one-page checklist, and assigned owners by shift.
    4. Tracked close time for two weeks.

    That’s project management. Not glamorous, but it’s scope, sequencing, ownership, and measurement.

    Common mistake: writing “strong communicator” on a resume. Nobody cares. Write: “Aligned 6 stakeholders on scope, reduced rework by standardizing intake checklist.” Even if your “stakeholders” were classmates—own it.

    3. Pursue Relevant Education or Certifications

    While a degree is not strictly necessary, pursuing a formal education in project management can be beneficial. Consider obtaining certifications such as:

    • PMI Project Management Professional (PMP): Highly recognized in the industry.
    • Certified Associate in Project Management (CAPM): Ideal for beginners looking to enter the field.
    • Agile Certifications: Particularly valuable in tech and construction sectors.

    Courses are often available online, making them accessible while you work or study. In fact, online platforms like Coursera and Udemy offer courses that can help you quickly gain the knowledge necessary for this field.

    My opinionated take after seeing a lot of resumes:

    • If you’re brand new, CAPM or a solid fundamentals course is usually enough to get interviews.
    • If you already run work informally (ops lead, coordinator, team lead), PMP can help you break through HR filters.
    • If you’re applying in software teams, you don’t need to cosplay a Scrum Master—but you do need to speak “backlog, sprint, dependency, release.” Agile certs can help, but only if you can back them up with examples.

    Step-by-step: how I’d choose a cert (without wasting money):

    1. Pull 15 job postings in your target niche (construction, IT, healthcare, etc.).
    2. Make a tally of what shows up repeatedly (PMP, CAPM, Agile, tools).
    3. If a cert appears in more than half, it’s a signal—not gospel, but a signal.
    4. Pick one program and finish it. Don’t collect half-certificates like merit badges.

    Common mistakes:

    • Getting certified and stopping there. A certificate is vocabulary; experience is proof.
    • Listing “Agile” because you used Trello once. Interviewers will probe.

    4. Gain Practical Experience

    Getting hands-on experience might be easier than you think. Look for opportunities to volunteer for project management roles in community organizations, or take on additional responsibilities at your current job. Even shadowing a project manager can provide invaluable insights.

    The key is to gather experience that demonstrates your ability to handle projects effectively, which can set you apart from other candidates. As a recent guide notes, you can leverage existing skills and find ways to showcase them (Medium).

    If you need a practical “experience plan” that isn’t vague, here’s what works:

    The 30-day project you can run inside almost any job

    1. Pick a tiny problem with a clear finish line. Examples: reduce customer response time, clean up a shared drive, improve onboarding, coordinate a small launch.
    2. Write a one-paragraph charter. Objective, scope (in/out), deadline, success metric.
    3. Build a simple plan. 10–25 tasks max. Owners + dates.
    4. Run one weekly check-in. 20 minutes. Decisions and blockers only.
    5. Close it loudly. Share results: metric before/after, what you learned, what’s next.

    Do that twice and you can truthfully say you’ve managed projects end-to-end.

    A persona anecdote I see a lot:

    A customer support rep wants to pivot to PM. She starts owning a “help center refresh” project—pulls top 20 ticket topics, rewrites articles, coordinates reviews with product/legal, publishes, measures ticket deflection. That’s stakeholder management, scope control, and delivery. In interviews, that story lands harder than “I’m passionate about project management.”

    Common mistake: taking on “extra responsibility” that never ends. If there’s no definition of done, it’s not a project—it’s unpaid operations. Put a deadline on it.

    5. Networking and Building Connections

    Networking is crucial in any career path, but especially in project management. Attend industry conferences, join professional organizations like the Project Management Institute, and connect with individuals on platforms like LinkedIn. Engaging with the community can often lead to job opportunities and mentorship.

    According to my experience, attending meetups frequently resulted in discovering unadvertised job openings.

    Here’s how to network in a way that doesn’t feel like begging:

    • Ask for a 15-minute “role reality check.” Not a job.
    • Bring three specific questions:
      1. “What’s the hardest part of PM in your org?”
      2. “What do you wish new PMs did in their first 30 days?”
      3. “What would make a junior candidate stand out to you?”
    • End with: “Is there anyone else you think I should talk to?”

    Do that five times and you’ll have better intel than any generic career article.

    Common mistake: only networking with other beginners. Talk to hiring managers, senior PMs, ops leads—people who actually feel the pain when projects go sideways.

    6. Tailor Your Resume and Apply for Positions

    When you're ready, it’s time to apply. Tailor your resume to highlight your transferable skills and any relevant experiences. Be sure to emphasize your ability to communicate, lead teams, and manage timelines effectively. Many job postings often list desired soft skills like adaptability, and these should be mirrored in your application materials.

    What “tailor your resume” should mean in practice:

    • Match the job posting’s language without copying it.
    • Put your best project story in the top third of page one.
    • Use numbers wherever you can—time saved, dollars avoided, cycle time reduced, stakeholders aligned.

    A structure that works (especially for career changers):

    • Headline: “Project coordinator / aspiring PM — ops + delivery”
    • Core skills: scope, scheduling, stakeholder comms, risk tracking, tools
    • Selected projects: 2–4 mini case studies
      • Project name
      • Goal + constraints
      • What you owned
      • Result

    If you don’t have “project” job titles yet, make a “Projects” section anyway. That’s not a trick; it’s clarity.

    7. Prepare for Interviews

    Finally, prepare for your interviews. Be ready to articulate how your past experiences relate to project management. Use the STAR method (Situation, Task, Action, Result) to structure your responses, making it easier to convey your capabilities.

    I’d add one more layer: interviewers want to know how you think when things break.

    So prep these stories:

    • A time scope changed late—what did you cut or renegotiate?
    • A time a stakeholder disagreed—how did you align them?
    • A time a dependency blocked you—what did you do in the first 24 hours?

    Step-by-step: the “PM interview drill” I recommend

    1. Pick one project story.
    2. Write it in STAR.
    3. Add a “what I’d do differently next time” line.
    4. Practice out loud until it’s under 2 minutes.

    That last part matters. Rambling is the silent killer in PM interviews.

    With over 25 million new project management roles expected globally by 2030, the demand for skilled project managers is significant, especially in sectors like construction and tech. But remember, even entry-level positions may require demonstrable skills, so showcasing what you already have is critical (FlashGenius).

    Exploring Pathways in Project Management Careers

    You don’t have to take the same route everyone else takes. In fact, most good PMs I’ve worked with came in sideways—from operations, support, design, engineering, the military, events, you name it.

    The trick is picking a pathway where your existing strengths are already valued, then adding just enough PM skill to become “obvious” for the role.

    Here are a few concrete paths, what they actually look like day-to-day, and how I’d break into each.

    Project Management in Construction

    The construction industry is among the most significant arenas for project managers. Construction project managers oversee building projects from inception to completion, ensuring compliance with safety regulations and budgets.

    To get into construction project management, consider pursuing courses that include:

    • Construction Management Certificates: These often cover essential topics such as budgeting, scheduling, and safety regulations.

    According to the U.S. Bureau of Labor Statistics, construction managers are projected to grow by 9% through 2033, which translates to about 45,800 job openings each year (The Birmingham Group).

    What people underestimate about construction PM: your calendar is the project. Site visits, inspections, permit timing, subcontractor schedules, material lead times—if you miss one dependency, everything wobbles.

    Step-by-step entry plan (if you’re outside construction today):

    1. Learn the basics of scheduling. Get comfortable reading a Gantt chart and understanding critical path.
    2. Pick up the language. RFIs, change orders, punch lists—know what they are.
    3. Shadow or coordinate. Even a role like project coordinator/assistant PM is gold.
    4. Build one portfolio story. Example: “Coordinated vendor schedules and inspections for a small renovation; reduced delays by tightening the weekly lookahead.”

    Common mistakes I’ve seen (and they’re expensive):

    • Treating change orders as paperwork instead of a scope negotiation.
    • Not documenting decisions. Verbal agreements vanish the moment there’s a dispute.
    • Overpromising on timelines because you didn’t validate lead times.

    Project Management in Tech

    The tech industry also offers diverse opportunities for aspiring project managers. Here, project managers often work with software development teams to oversee project timelines and deliverables.

    Experience in Agile methodologies can be particularly advantageous. Familiarize yourself with tools like Jira or Trello, which are commonly used in tech environments.

    Moreover, the project management software market is expected to grow significantly, from $9.76 billion in 2025 to $11.27 billion in 2026 (monday.com).

    What tech PM work actually feels like: less “schedule everything to the hour,” more “keep priorities clean and decisions unblocked.” You’re constantly translating between product, engineering, design, support, and leadership.

    A real example (small but real):

    I once watched a new PM get crushed because they ran sprint planning like a lecture. Tickets were vague, acceptance criteria were missing, and devs kept discovering requirements mid-sprint. Velocity tanked. The fix wasn’t more meetings—it was better inputs.

    Here’s the exact approach that got the team back on track:

    1. Add a lightweight “definition of ready” (clear title, problem statement, acceptance criteria, dependencies).
    2. Run a 30-minute backlog grooming before planning.
    3. Limit WIP and stop pulling in surprise work unless someone explicitly trades it for something.
    4. Track one metric for a month (carryover work, cycle time, or escaped bugs).

    That’s PM value in tech: making the work legible so the team can ship.

    Common mistakes in tech PM:

    • Confusing “Agile” with “no deadlines.” Leadership will still ask for dates.
    • Letting stakeholders inject work mid-stream without a tradeoff.
    • Reporting status without highlighting decisions needed. Status isn’t the point—movement is.

    Engineering Project Managers

    For those with an engineering background, becoming a project manager in engineering can be a natural progression. Here, project managers are needed to coordinate technical teams and ensure projects meet engineering standards. The specialized knowledge you have can set you apart in this competitive field.

    What I’d watch out for if you’re an engineer moving into PM:

    • Your instinct will be to solve the technical problem yourself. Sometimes that helps. Often it hurts—because the team still needs coordination, and you’ll become the bottleneck.
    • Practice saying: “Who owns this?” and “What’s the next decision?” That’s the PM muscle.

    A clean way to transition without whiplash:

    Start by owning one cross-team initiative (tooling migration, reliability improvements, compliance project). Keep your technical credibility, but deliberately shift your energy to aligning people, sequencing work, and communicating risk.

    Conclusion

    Stepping into a project management career is entirely possible, but the path that works isn’t “wait until you’re ready.” It’s: start managing small projects now, collect proof, then level up your scope.

    If you take only one idea from this: hiring managers don’t need you to have the title—they need you to have evidence. A tight project story with a measurable result beats a fluffy resume every time.

    Here’s a practical next step you can do this week (seriously, in a few hours):

    1. Pick one project you’ve already done (work, school, volunteering).
    2. Write a 6-line case study:
      • Goal
      • Stakeholders
      • Timeline
      • Your actions
      • Result (number if possible)
      • What you learned
    3. Turn that into:
      • One resume bullet
      • One LinkedIn post (optional)
      • One interview story

    A quick “I’ve seen this work” anecdote:

    A friend of mine was stuck in an admin role, constantly told she wasn’t “technical enough” to be a PM. She started running a small internal rollout—new intake form, new process, training session, two-week check-in cycle. She documented the before/after (fewer missed requests, clearer priorities), and she brought that one-page write-up to interviews. She didn’t just say she could manage projects; she showed she already had.

    Also—don’t ignore the messy reality: you will mess up a timeline, you’ll underestimate a dependency, you’ll have a stakeholder go silent. That’s the job. The difference between a beginner and a pro is how fast you surface the risk, how clearly you communicate tradeoffs, and whether you close the loop.

    For assistance in crafting content that aligns with project management strategies, tools like Sibgha Jamil can streamline your process significantly.

    Pick your first small project, ship it, write it up, and go apply. That’s the whole game.